Analytics
Find aggregate access, web, and firewall block trends.
Use Security → Analytics to spot patterns in blocked traffic: which destinations, categories and users draw the most blocks, and how that changes over time. Use it to find a trend, then move to Audit to investigate single events.
Before you start#
- You need the
audit:viewpermission (theaudit.readpermission on the control plane). On tenants without a permission list, the owner and admin roles have it. Without it you see “You don’t have permission to view audit logs. Contact your administrator for access.” - Access counts come from access decisions recorded by gateways. Secure Web counts come from content filter logs. If neither source has produced events, every chart is empty.
- Firewall telemetry is not connected yet. The Firewall card always reads Unavailable.
Investigate a trend#
- Open Security → Analytics. The header reads Security Analytics with the description “Blocked access attempts, web filtering decisions, and top offenders.”
- Choose a range: 24h, 7d or 30d. The default is 7d. Each range is measured back from now.
- Compare the three count cards. Access shows blocks over “total decisions”. Secure Web shows blocks over “DNS queries”, plus a “malware blocked” count that links to the matching audit view.
- Read Block trend. The chart plots Access and Secure Web blocks per bucket, labelled “Last 24 Hours”, “Last 7 Days” or “Last 30 Days”.
- Scan Top blocks by category. It has an Access, Secure Web and Firewall column.
- Scan Top users by blocks. Users appear by display name, then email, then the first eight characters of their ID. Users with no ID show as “Unknown user”.
- Check Recent Blocks in the side panel. Each row shows the user, the detail (a destination or domain), the policy or category, a BLOCKED chip, a relative time, and a source link reading Access or Secure Web.
- Click View audit logs to open Audit filtered to denied decisions, or click a source link in Recent Blocks to open Audit filtered to that source.
You should see non-zero totals as soon as gateways have recorded decisions in the chosen range. Recent Blocks shows a Live indicator and polls every 30 seconds while the browser tab is visible. Rows that arrive from a poll fade in.
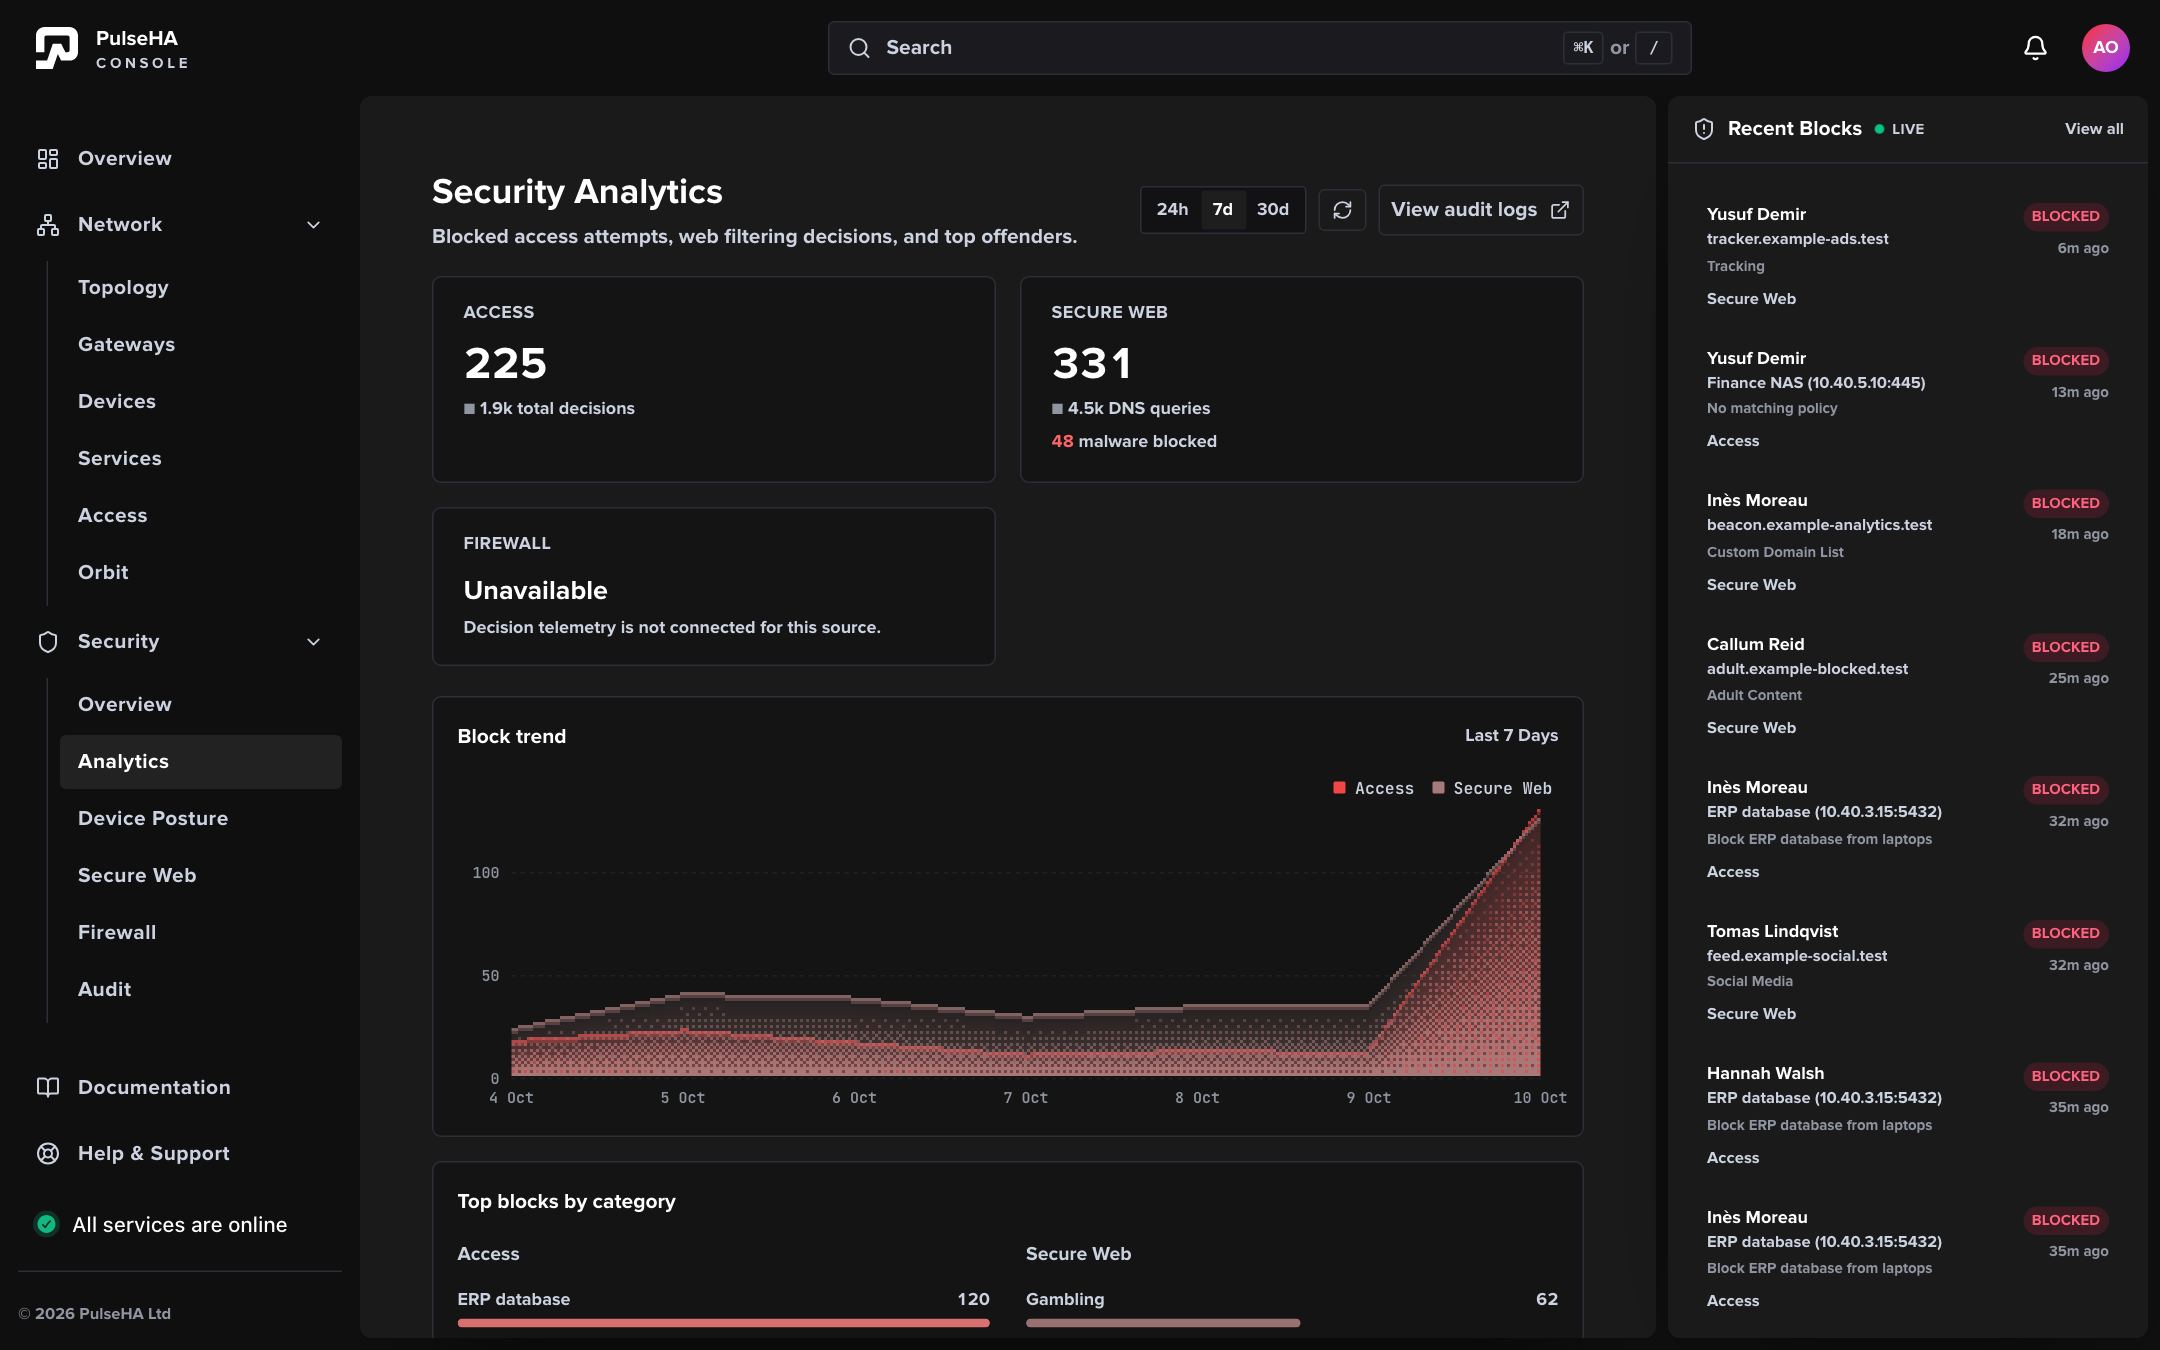
The 7d range populated: 225 access blocks out of 1.9k decisions, 307 Secure Web blocks out of 4.5k DNS queries, and the Firewall card still reads Unavailable.
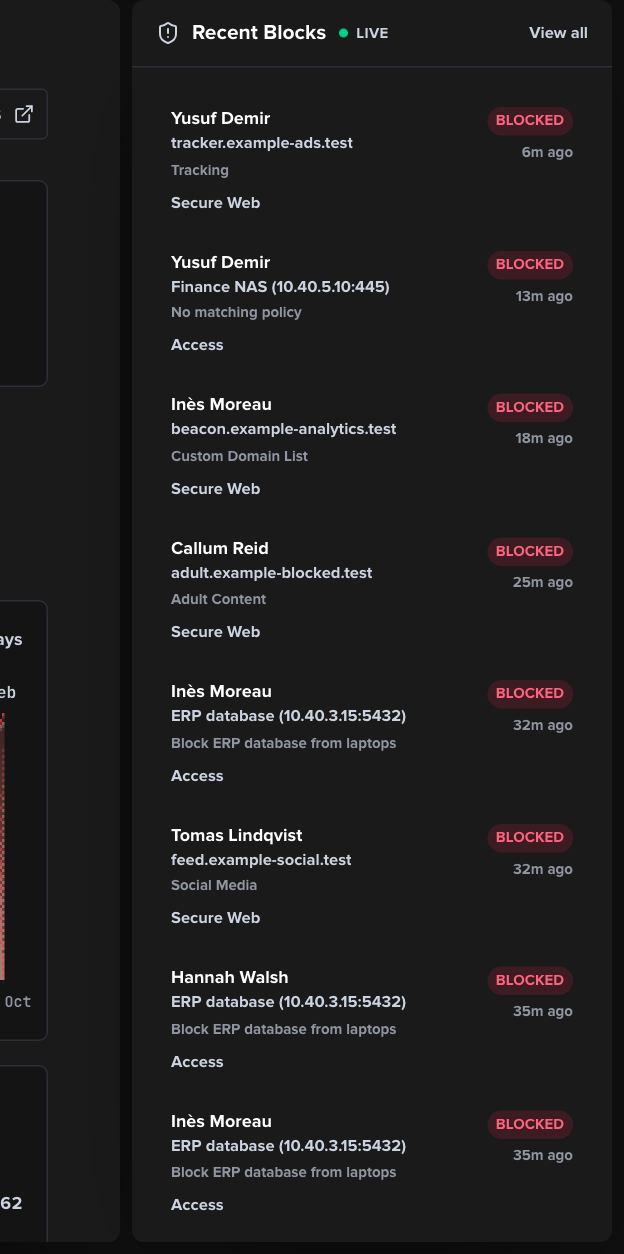
Each Recent Blocks row carries the user, the destination, the policy or category that matched, and a source link that opens Audit filtered to that source.
Reference#
How counts are defined#
| Field | Source | Meaning |
|---|---|---|
| Access total | Access decisions | Every access decision in the range |
| Access blocks | Access decisions | Decisions with the value deny |
| Secure Web total | Content filter logs | Every DNS query logged in the range |
| Secure Web blocks | Content filter logs | Logged queries with the action deny |
| Firewall | Not connected | Always reported as unavailable with zero counts |
Lists and limits#
| List | Definition |
|---|---|
| Top blocks by category, Access | Blocked decisions grouped by service name, then destination CIDR, then “Unknown”. Top seven. |
| Top blocks by category, Secure Web | Blocked queries grouped by category, then reason, then “Uncategorized”. Top seven. |
| Top users by blocks | Access and Secure Web blocks combined per user. Top ten. |
| Recent Blocks | The 15 newest blocks across both sources. |
| Block trend | 24 buckets for 24h, 7 for 7d, 30 for 30d. |
The “malware blocked” figure on the Secure Web card sums the malware category entries in the top-seven list. If malware is outside the top seven for that range, the card undercounts it.
The control plane rejects analytics windows longer than 31 days and accepts between 1 and 90 buckets.
Category names#
Content filter categories arrive as slugs and are displayed with friendly names, for example “Malware”, “Adult Content”, “Gambling”, “Social Media”, “Ads & Trackers” and “Custom Domain List”.
Troubleshooting#
- “Unable to load analytics. Try refreshing.” No data loaded at all. Use the Refresh analytics button (the circular arrow icon).
- “Security analytics timed out. Try again.” The request hit a timeout (HTTP 408 or 504). Try a shorter range.
- “Couldn’t reach security analytics. Check your connection and try again.” The browser got no response from the console.
- “Security analytics is temporarily unavailable. Try again.” The control plane returned a server error.
- “No blocks in this period” or “No user blocks in this period”. The range has no denied decisions from that source. Widen the range or check that gateways are enforcing policies.
- “No recent block events”. The side panel has nothing to show for this tenant yet.
- Firewall card shows “Decision telemetry is not connected for this source.” Expected. Firewall decisions are not yet fed into analytics.
- Error toasts only appear on foreground loads. Background polls fail silently, so the page may show stale data. Refresh to confirm.
Related tasks#
- Audit for searchable event details and the event inspector.
- Reports for fixed historical windows and downloadable summaries.
- Security overview for the posture score.
- Secure Web to change the policies behind Secure Web blocks.
- Access policies to change the policies behind Access blocks.