Firewall
Apply ordered L3/L4 rules at gateways.
Use Security → Firewall to control which IP traffic a gateway forwards, accepts or emits. Rules are evaluated at the gateway after routing context exists. A firewall rule does not grant a device a route to a private service; access policies still apply.
Before you start#
- Viewing needs
firewall:view. Adding, editing, reordering, toggling and deleting needfirewall:update(owner and admin by default). Read-only users see the tables without Add buttons, row menus or drag handles. - Rules only take effect on gateways that report firewall capability. The gateway page states “Firewall reporting requires gateway 2.6.3 or later.”
- Enabling rules needs every targeted gateway upgraded and tenant-exclusive. Otherwise the control plane answers “Upgrade all targeted gateways and use tenant-exclusive gateways before enabling firewall rules”.
- Rule names must be 3 to 100 characters.
Create a rule#
- Open Security → Firewall. The page has four tabs: Rules, IP Lists, Rule Groups and Port Forwards.
- On Rules, click Add Rule.
- Under Basic Information, enter Rule Name, an optional Description, and a Priority from 1 to 10000 (default 100). The help text reads “Lower numbers are evaluated first (1-10000).” Pick a Rule Group if any exist.
- Under Action, choose Allow, Deny or Reject.
- Under Direction, choose Forward, Inbound or Outbound. The default is Forward.
- Under Traffic Match, set Source and Destination to Any, Single IP, CIDR or IP List. Set Protocol / Port to Any, TCP, UDP or ICMP. For TCP and UDP enter a port, a range such as
80-443, or a comma-separated list. - Under Gateways, leave Apply to gateways empty to target all gateways, or select specific ones.
- Under Options, turn on Log traffic if you want matches recorded, and leave Enabled on.
- Review the Rule Summary panel and any Broad rule warning, then click Create Rule.
You should see “Rule created” and the new row in the table. The header chip changes to Applying changes… until gateways confirm.
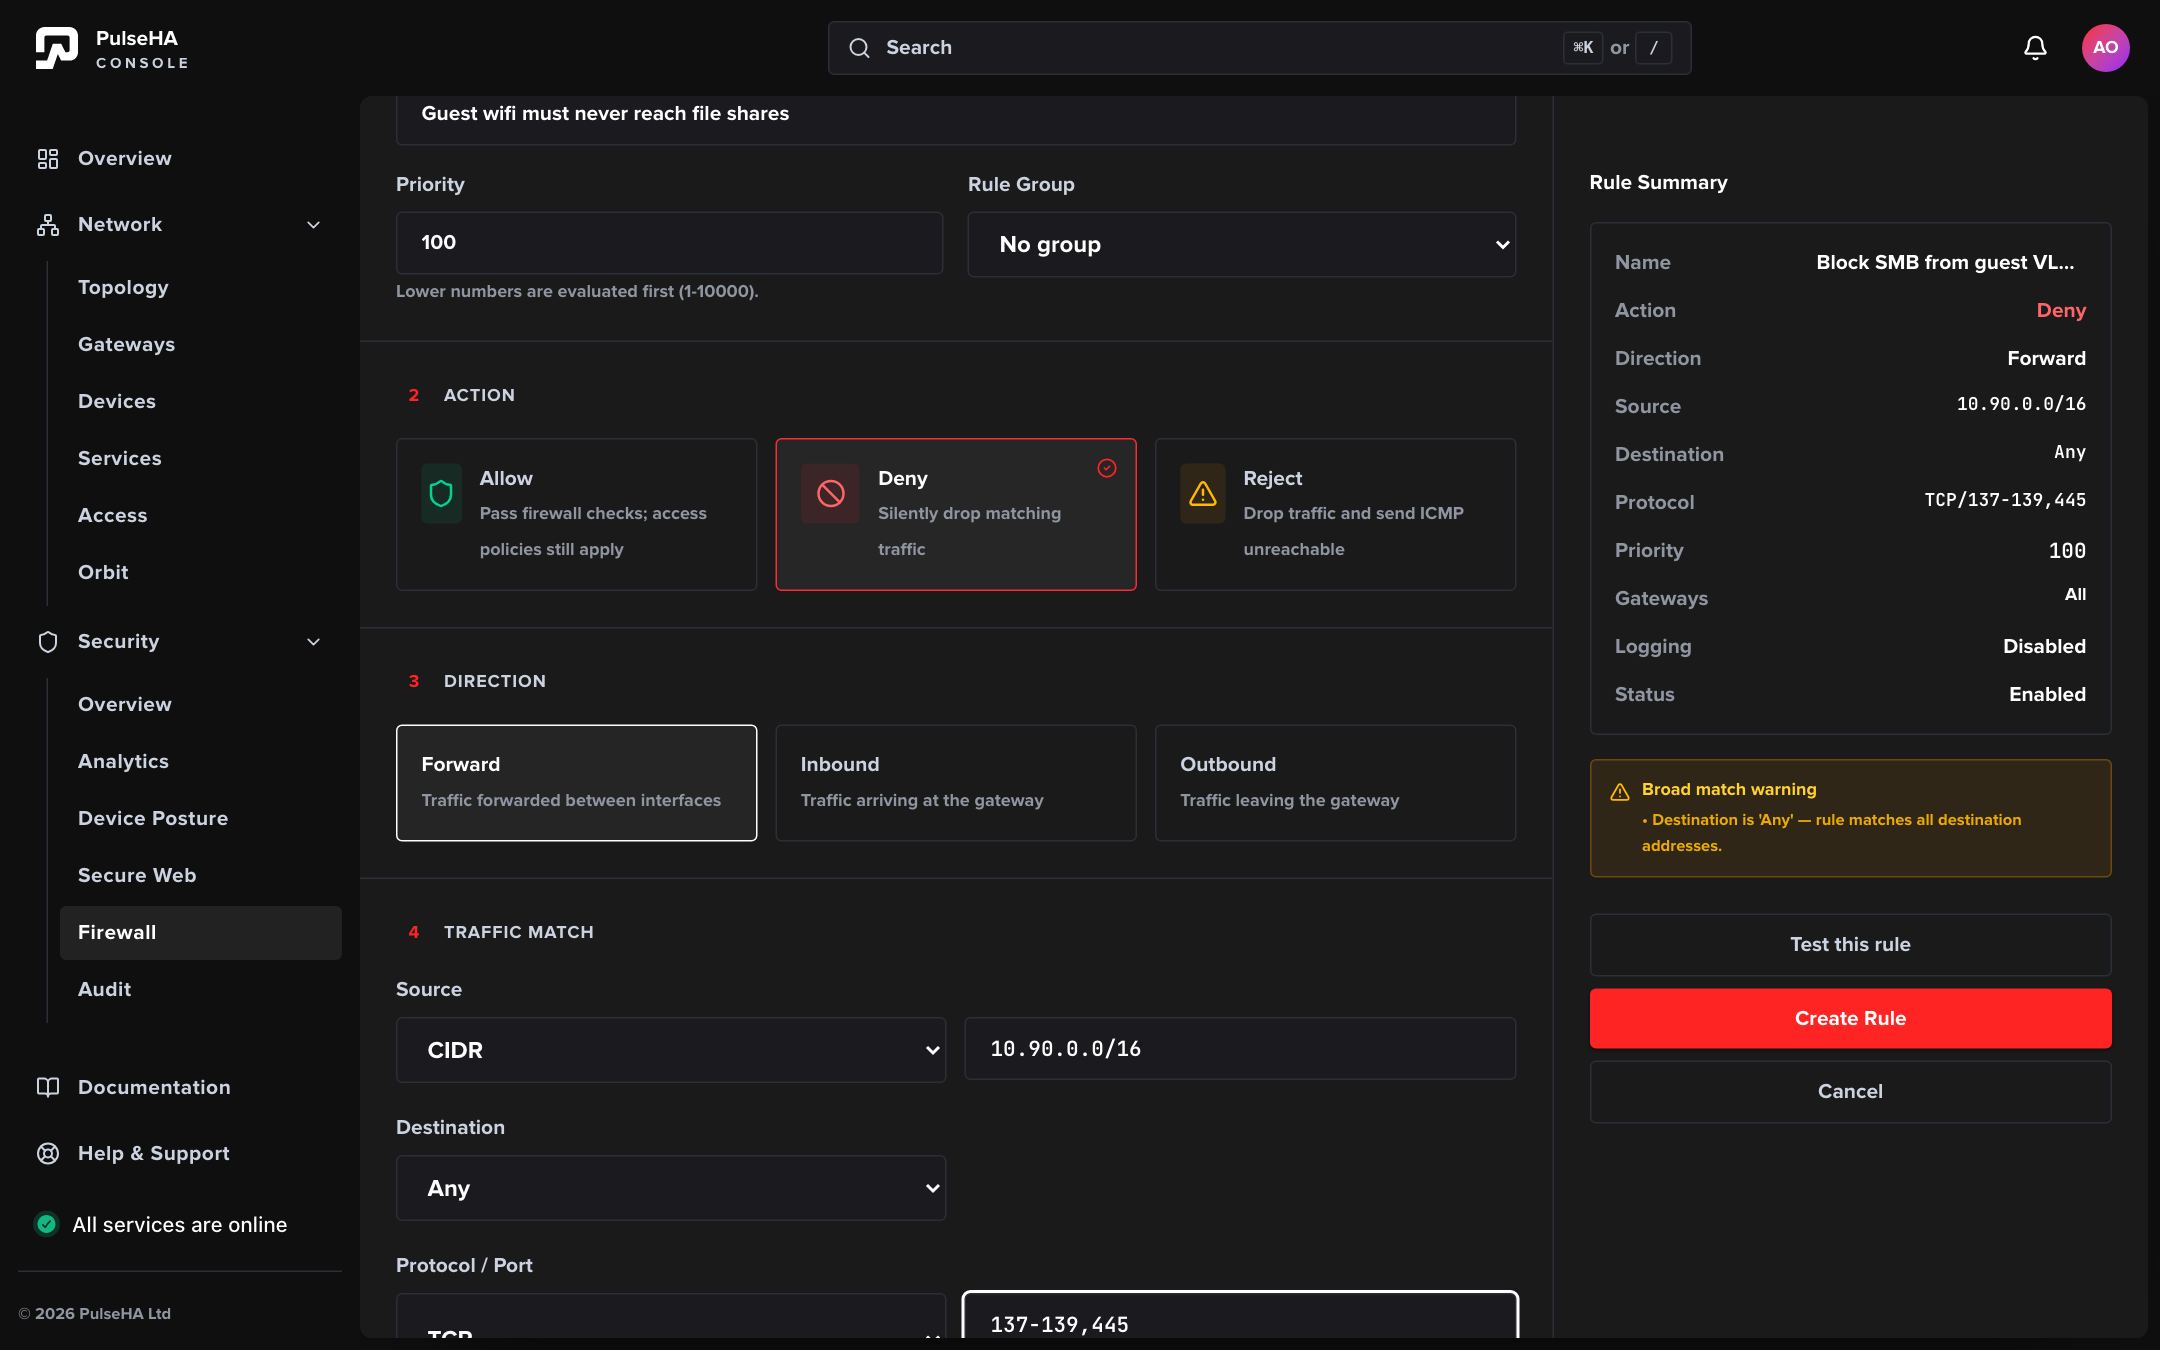
The rule form builds the Rule Summary as you type; an Any destination triggers the Broad match warning before you save.
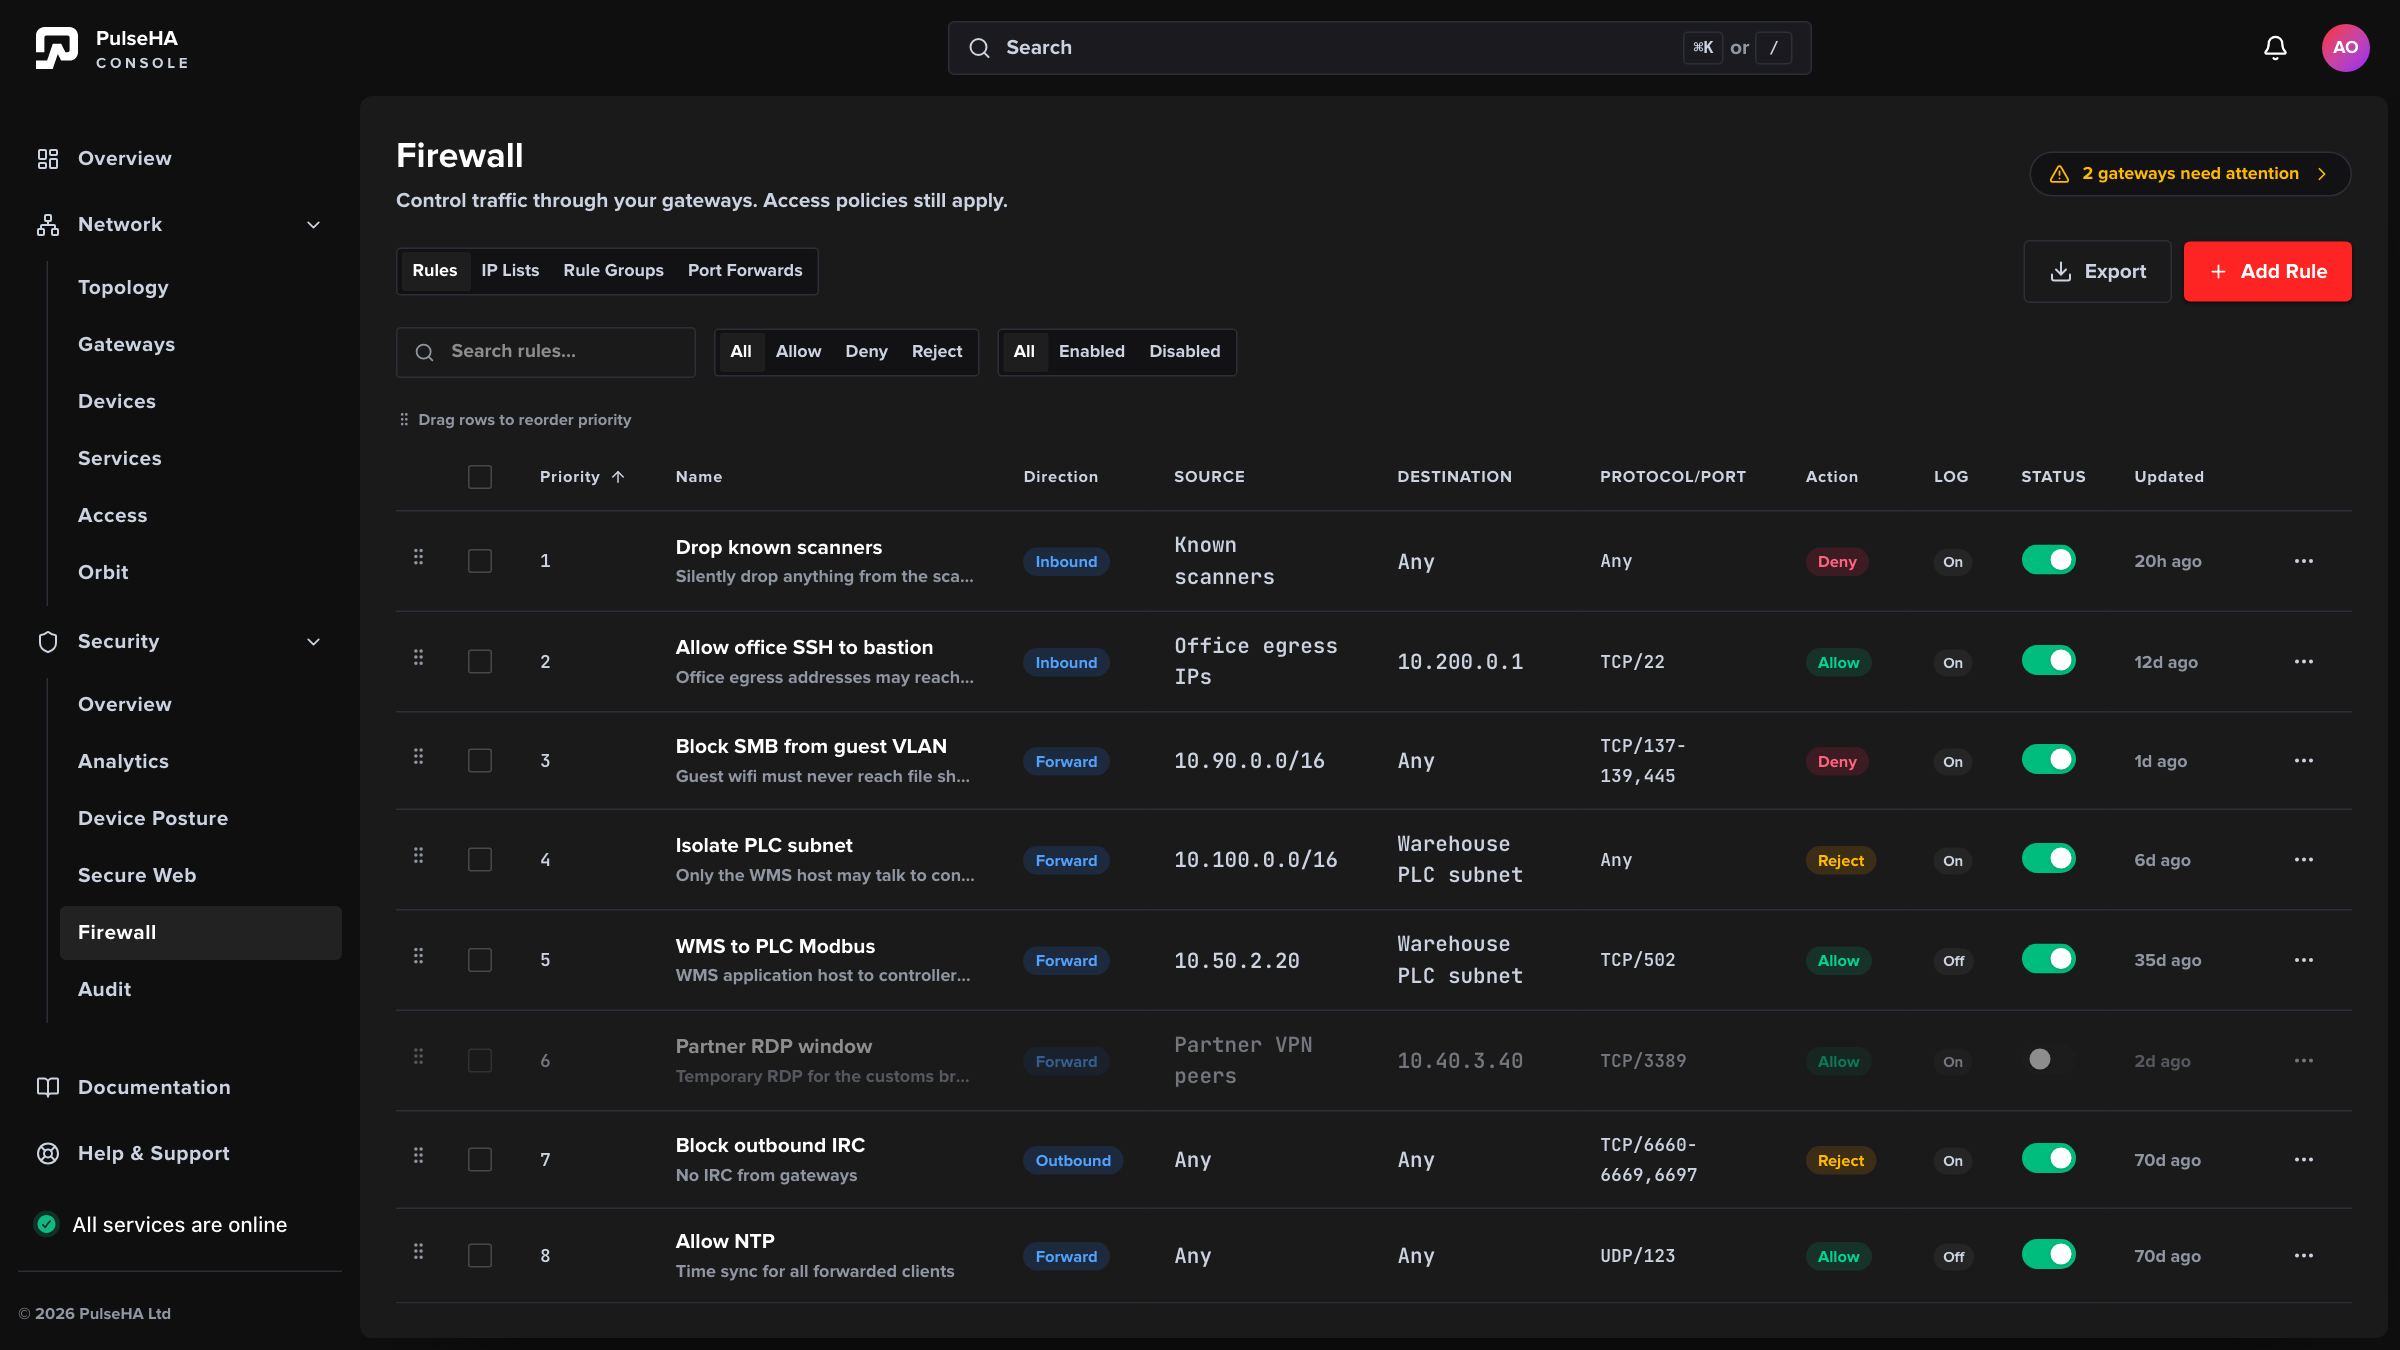
The rules list shows action chips and status toggles per row; the header chip summarises gateway confirmation, here flagging gateways that need attention.
Reorder rules#
- Clear any search or filter on the Rules tab.
- Drag rows into the order you want. The hint reads “Drag rows to reorder priority”.
Dropping renumbers every rule’s priority from 1 upward. Gateways receive enabled rules sorted by priority, then ID.
Test a rule before saving#
- In the rule form, click Test this rule.
- Enter Source IP, Destination IP, Protocol and Port (1-65535), or click Match example.
- Read the result: MATCHES ALLOW, MATCHES DENY, MATCHES REJECT or NO MATCH, with a Per-field breakdown.
The drawer states: “Advisory single-rule match only. This does not check gateway scope, direction, rule ordering, enabled or applied state, or the final ZTNA outcome.” Use Policy simulation for identity-aware access decisions.
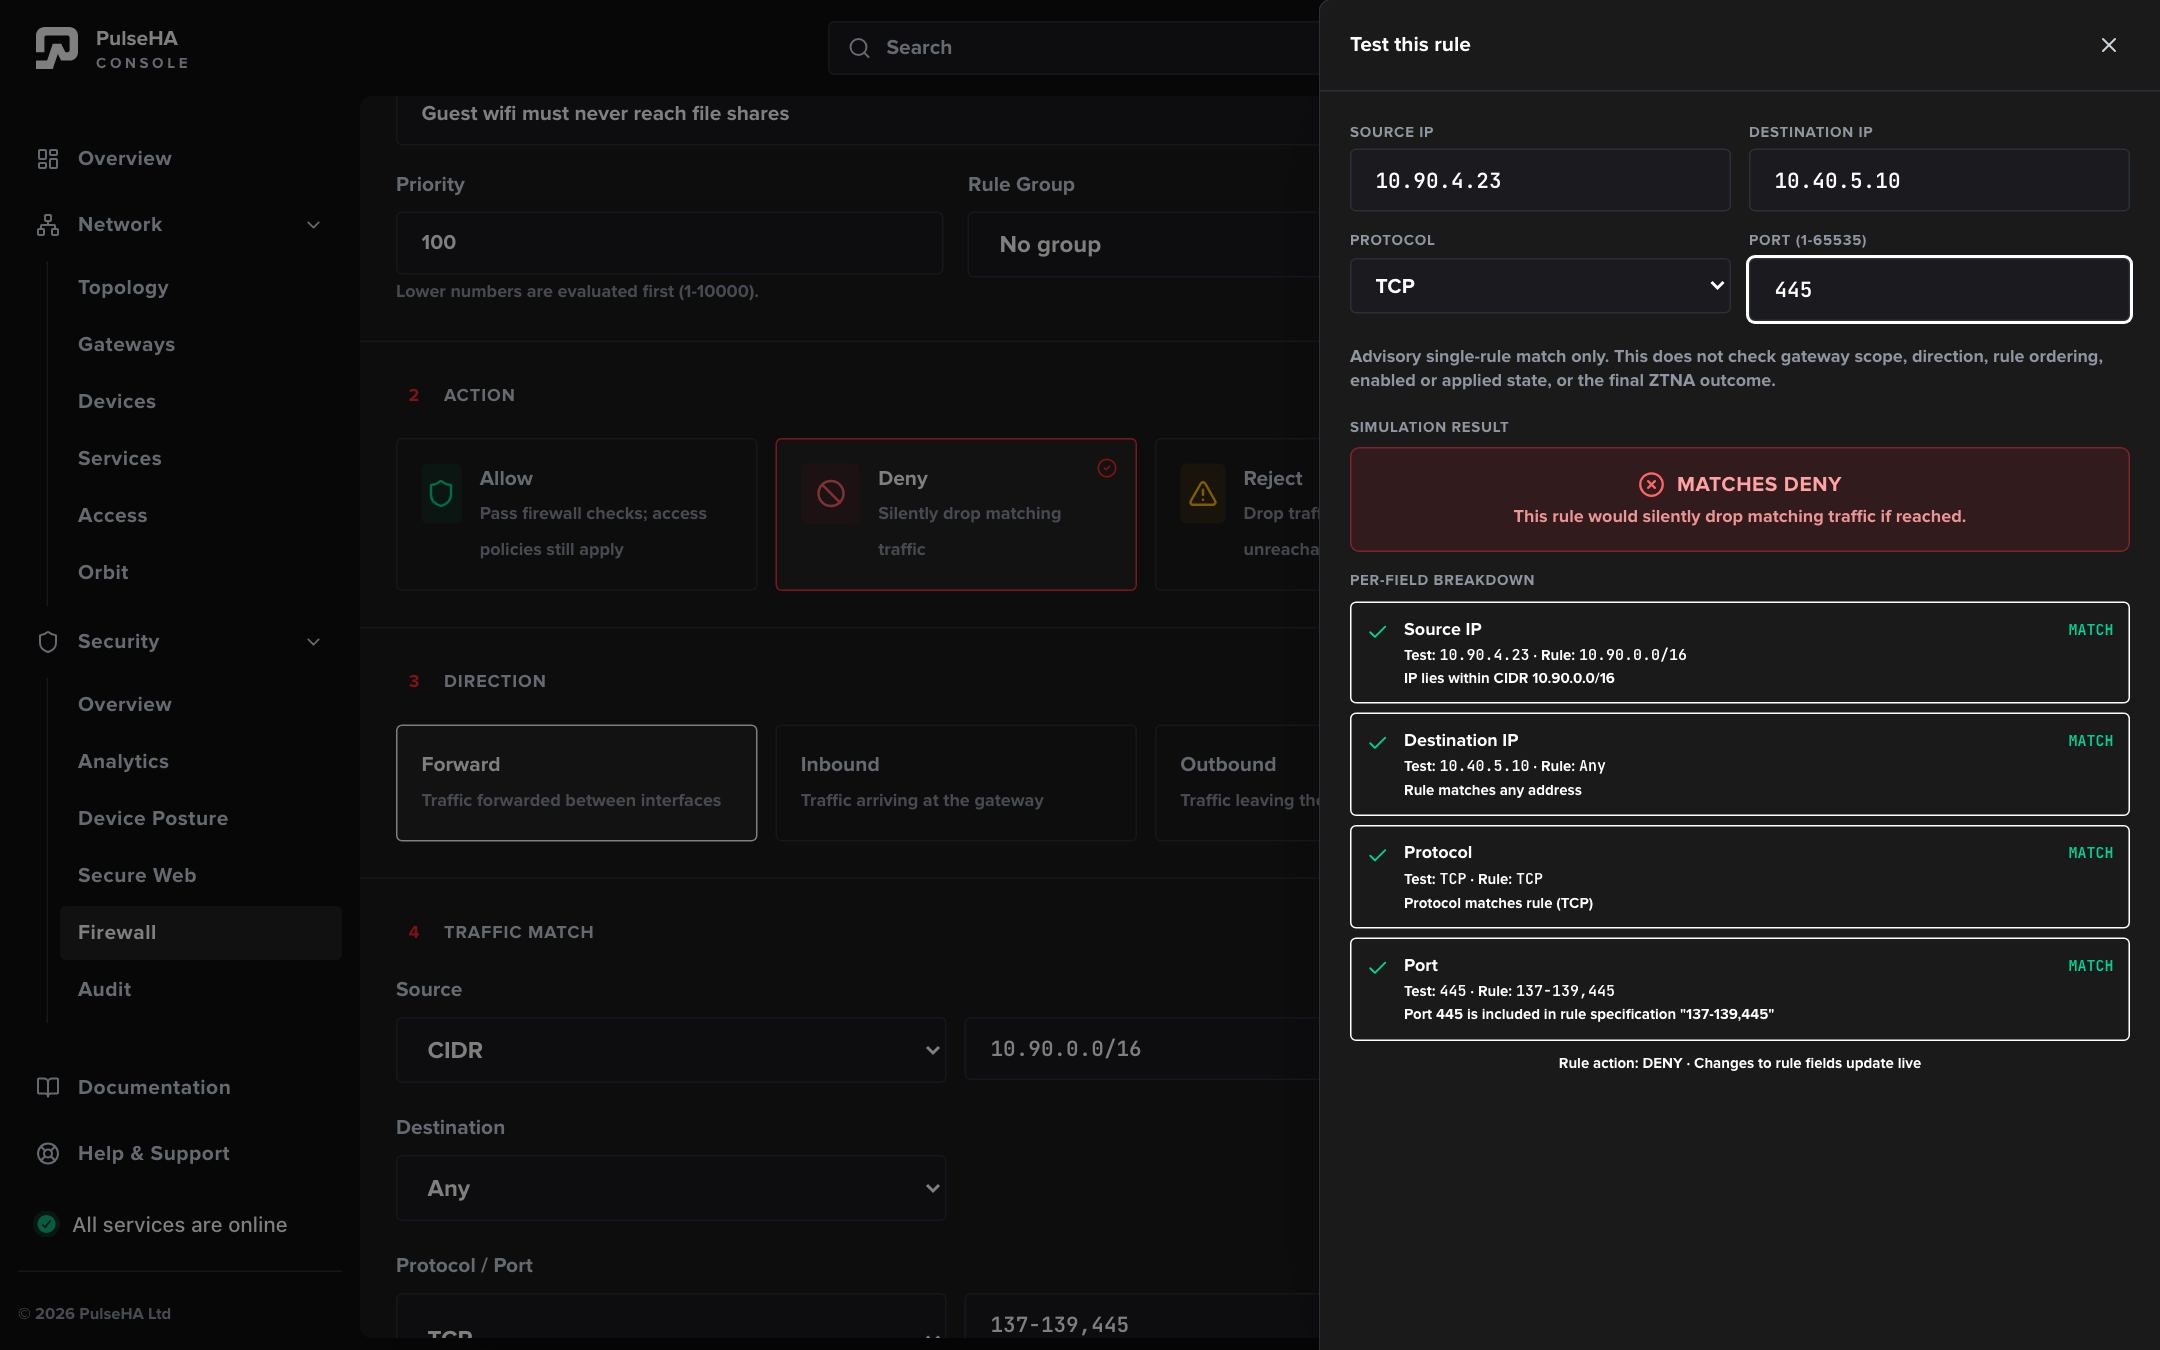
The simulator checks one rule against a single packet and explains each field; MATCHES DENY here means the guest VLAN source and port 445 both fit the rule.
Reference#
Actions#
| Action | Effect |
|---|---|
| Allow | Pass firewall checks; access policies still apply |
| Deny | Silently drop matching traffic |
| Reject | Drop traffic and send ICMP unreachable |
Directions#
| Direction | Meaning |
|---|---|
| Forward | Traffic forwarded between interfaces |
| Inbound | Traffic arriving at the gateway |
| Outbound | Traffic leaving the gateway |
Rules table columns#
Priority, Name, Direction, Source, Destination, Protocol/Port, Action, Log (On or Off), Status (an enable toggle) and Updated. Filters are Action (All, Allow, Deny, Reject) and Status (All, Enabled, Disabled). Bulk actions are Delete, Enable and Disable. The Export menu offers Export as CSV and Export as JSON.
Gateway application status#
The header chip summarises confirmation from gateways. Reports older than two minutes do not count.
| Chip | Meaning |
|---|---|
| No active rules | No enabled rules or port forwards |
| Status unavailable | No desired revision was reported |
| No gateways available | No targeted gateways exist |
| Applying changes… | Some gateways have not yet applied the latest revision |
| N gateways need attention | Gateways are missing, need an upgrade, or have no recent report |
| Changes applied | Every targeted gateway reports the current revision |
Per gateway, the drawer Firewall application shows Applied, Awaiting changes, Confirmation unavailable or Upgrade required.
IP Lists and Rule Groups#
IP Lists hold 1 to 1000 IPs or CIDRs and are referenced by the IP List endpoint type. Lists referenced by rules cannot be deleted. A plain IP is saved as a /32 or /128. Rule Groups only organise rules; deleting a group leaves its rules ungrouped. The control plane allows 1000 rules, 1000 lists and 1000 groups per tenant.
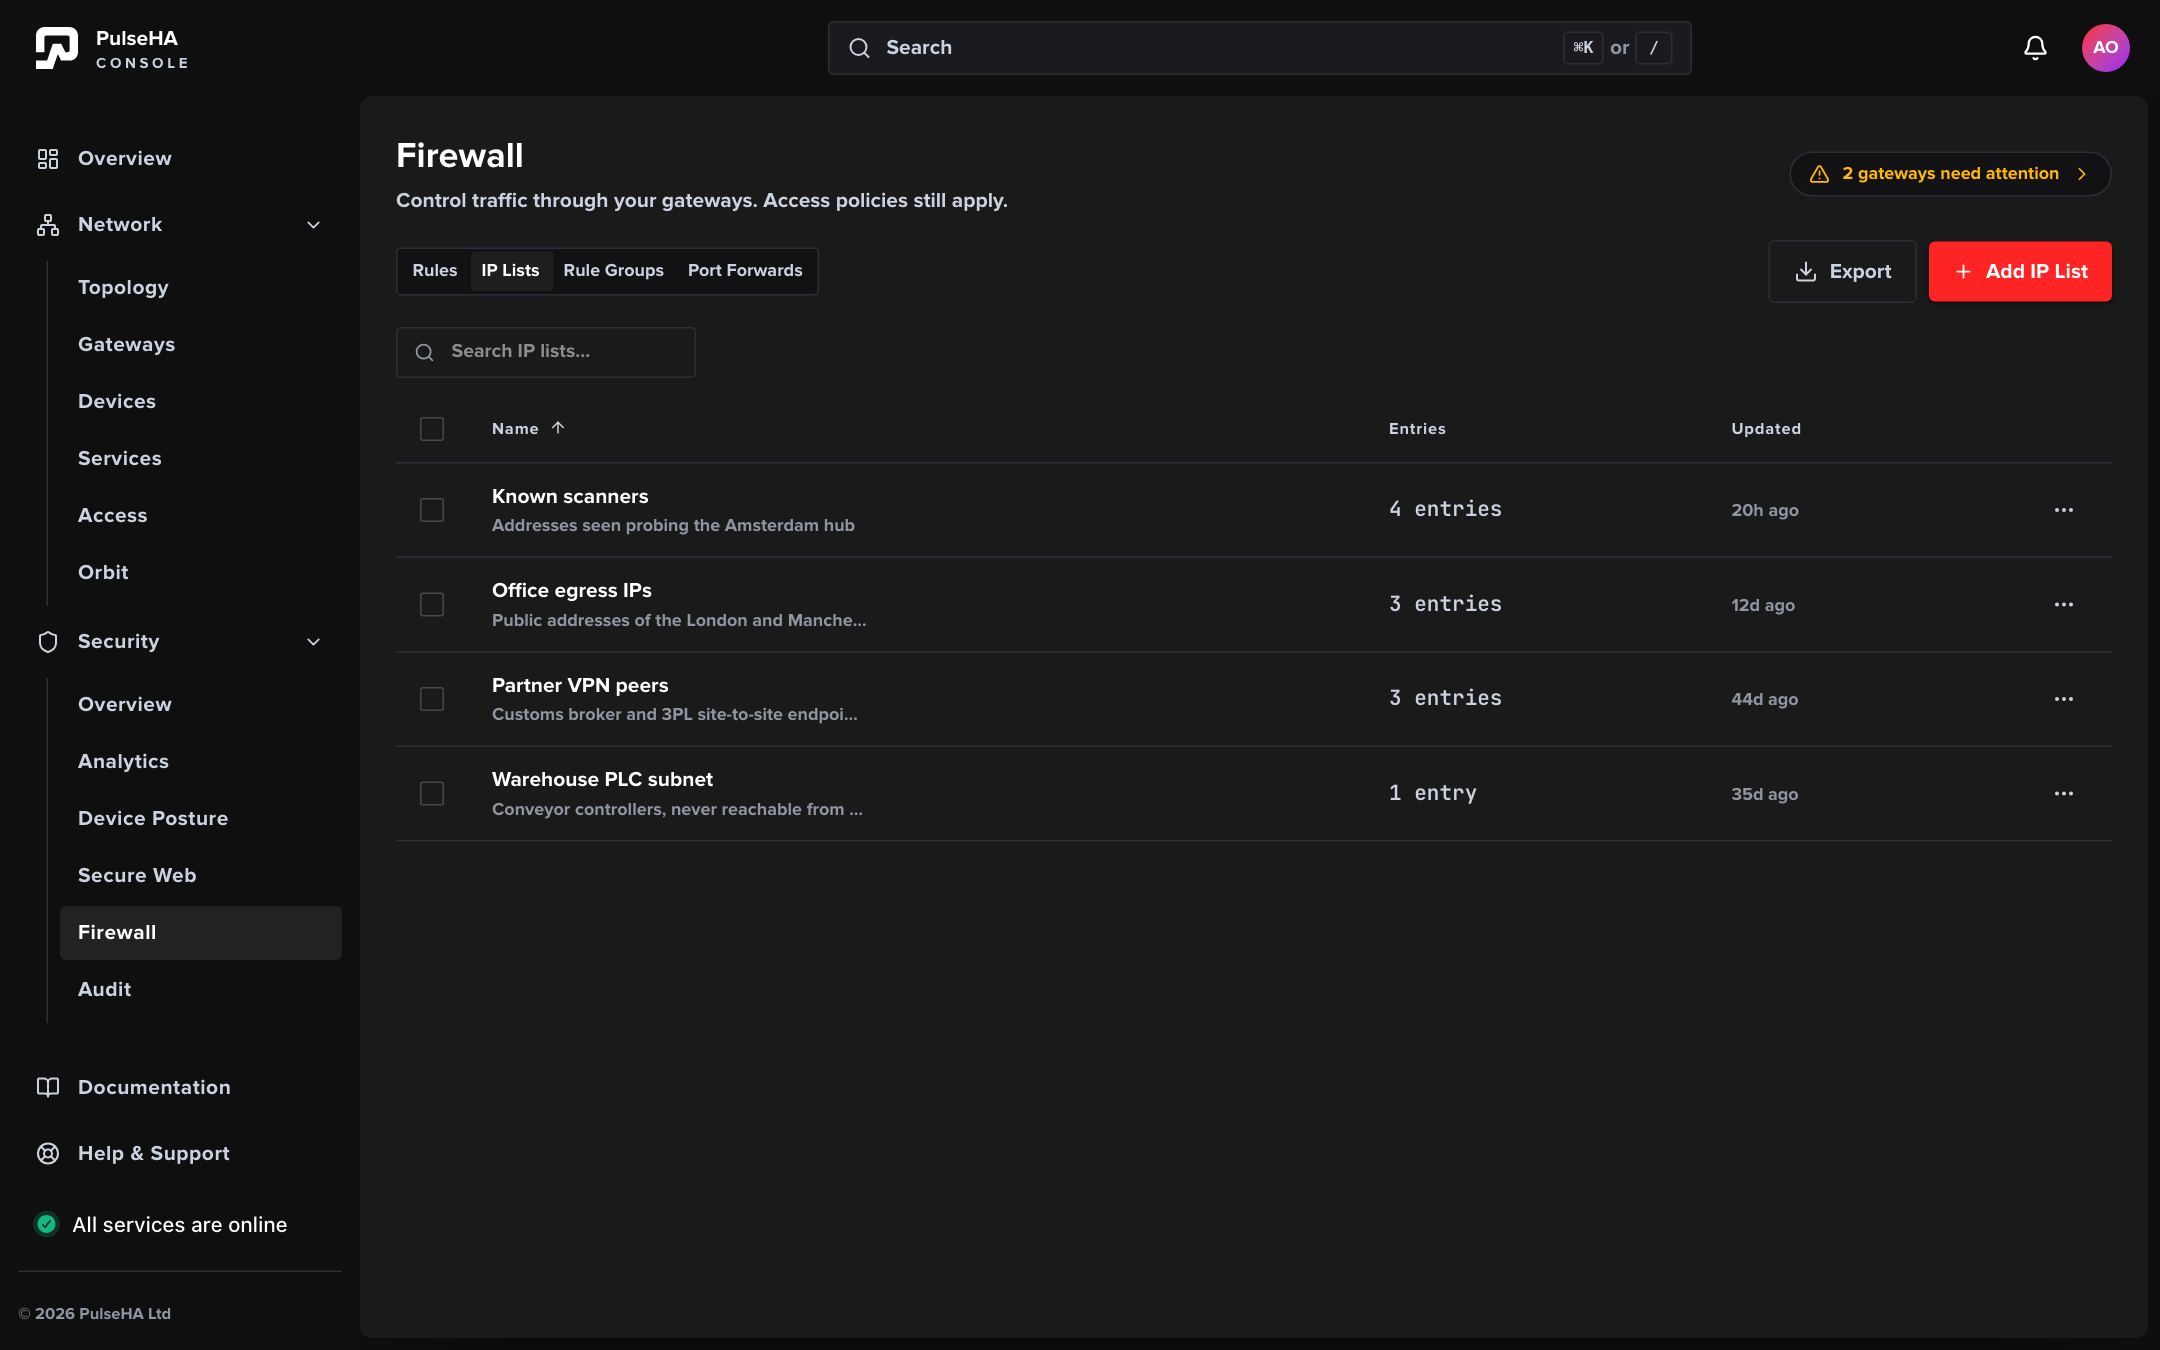
IP Lists give a name to a set of addresses so rules can reference them; entry counts update as you edit the list.
Troubleshooting#
- “Firewall configuration unavailable” with “The existing gateway policy remains in effect. Try again before making changes.” The page could not load rules, lists, groups or port forwards. Click Try again.
- “Upgrade required” on a gateway. Its heartbeat does not report firewall capability. Upgrade it.
- “Confirmation unavailable”. The gateway has no report, or its last report is two minutes old or more. Check the gateway is online.
- “Reorder requires the complete ruleset”. The reorder request did not include every rule. Clear filters and drag again.
- “Invalid port format. Use single port, range (80-443), or comma-separated.” Fix the port field. Ports are only valid for TCP and UDP.
- “Lists referenced by rules cannot be deleted. Remove their rule references first.” Edit the rules that use the list.
- Traffic still flows after a Deny rule. Confirm the rule is enabled, its gateways show Applied, and that a lower-priority Allow does not match first.
Related tasks#
- Policy simulation for identity-aware access decisions.
- Audit for observed events.
- Gateways to upgrade gateways and check their status.
- Access policies to grant service access.
- Exit nodes for internet egress through gateways.