Your first access policy
Grant one subject access to one published service.
Nothing is reachable through PulseHA until an access policy allows it. This page walks through creating one Allow policy that lets one user reach one published service, and explains how the control plane evaluates it.
Prerequisites#
- The owner, admin or user role, or a custom role with
policies.create. Editing and deleting policies later needspolicies.updateandpolicies.delete, which only owner and admin hold by default. - At least one gateway that is Online. See Enroll a gateway.
- At least one enrolled device, so you can test. See Install the agent.
- A service to grant. Publish one first (see Services), or create it from the policy form with + New service, which needs
services:create. The form cannot be submitted without a service.
Create the policy#
- Open Network → Access. The Access Policies tab is selected. Choose Add Policy (also Create Policy on Overview).
- Under section 1, enter a name. The placeholder suggests the shape:
Engineering → Prod Services. Names must be 3 to 100 characters and unique within the organisation. Notes and Tags are optional. - Under section 2, keep Allow selected (Permit access to selected resources). Leave Priority at
100for now. The panel beside it shows where this policy ranks against existing ones. - Under 3 Who (Subjects), do one of the following:
- Tick All subjects to cover every user and device in the organisation.
- Leave it unticked and pick at least one entry under Users, Groups or Devices using Select users…, Select groups… or Select devices….
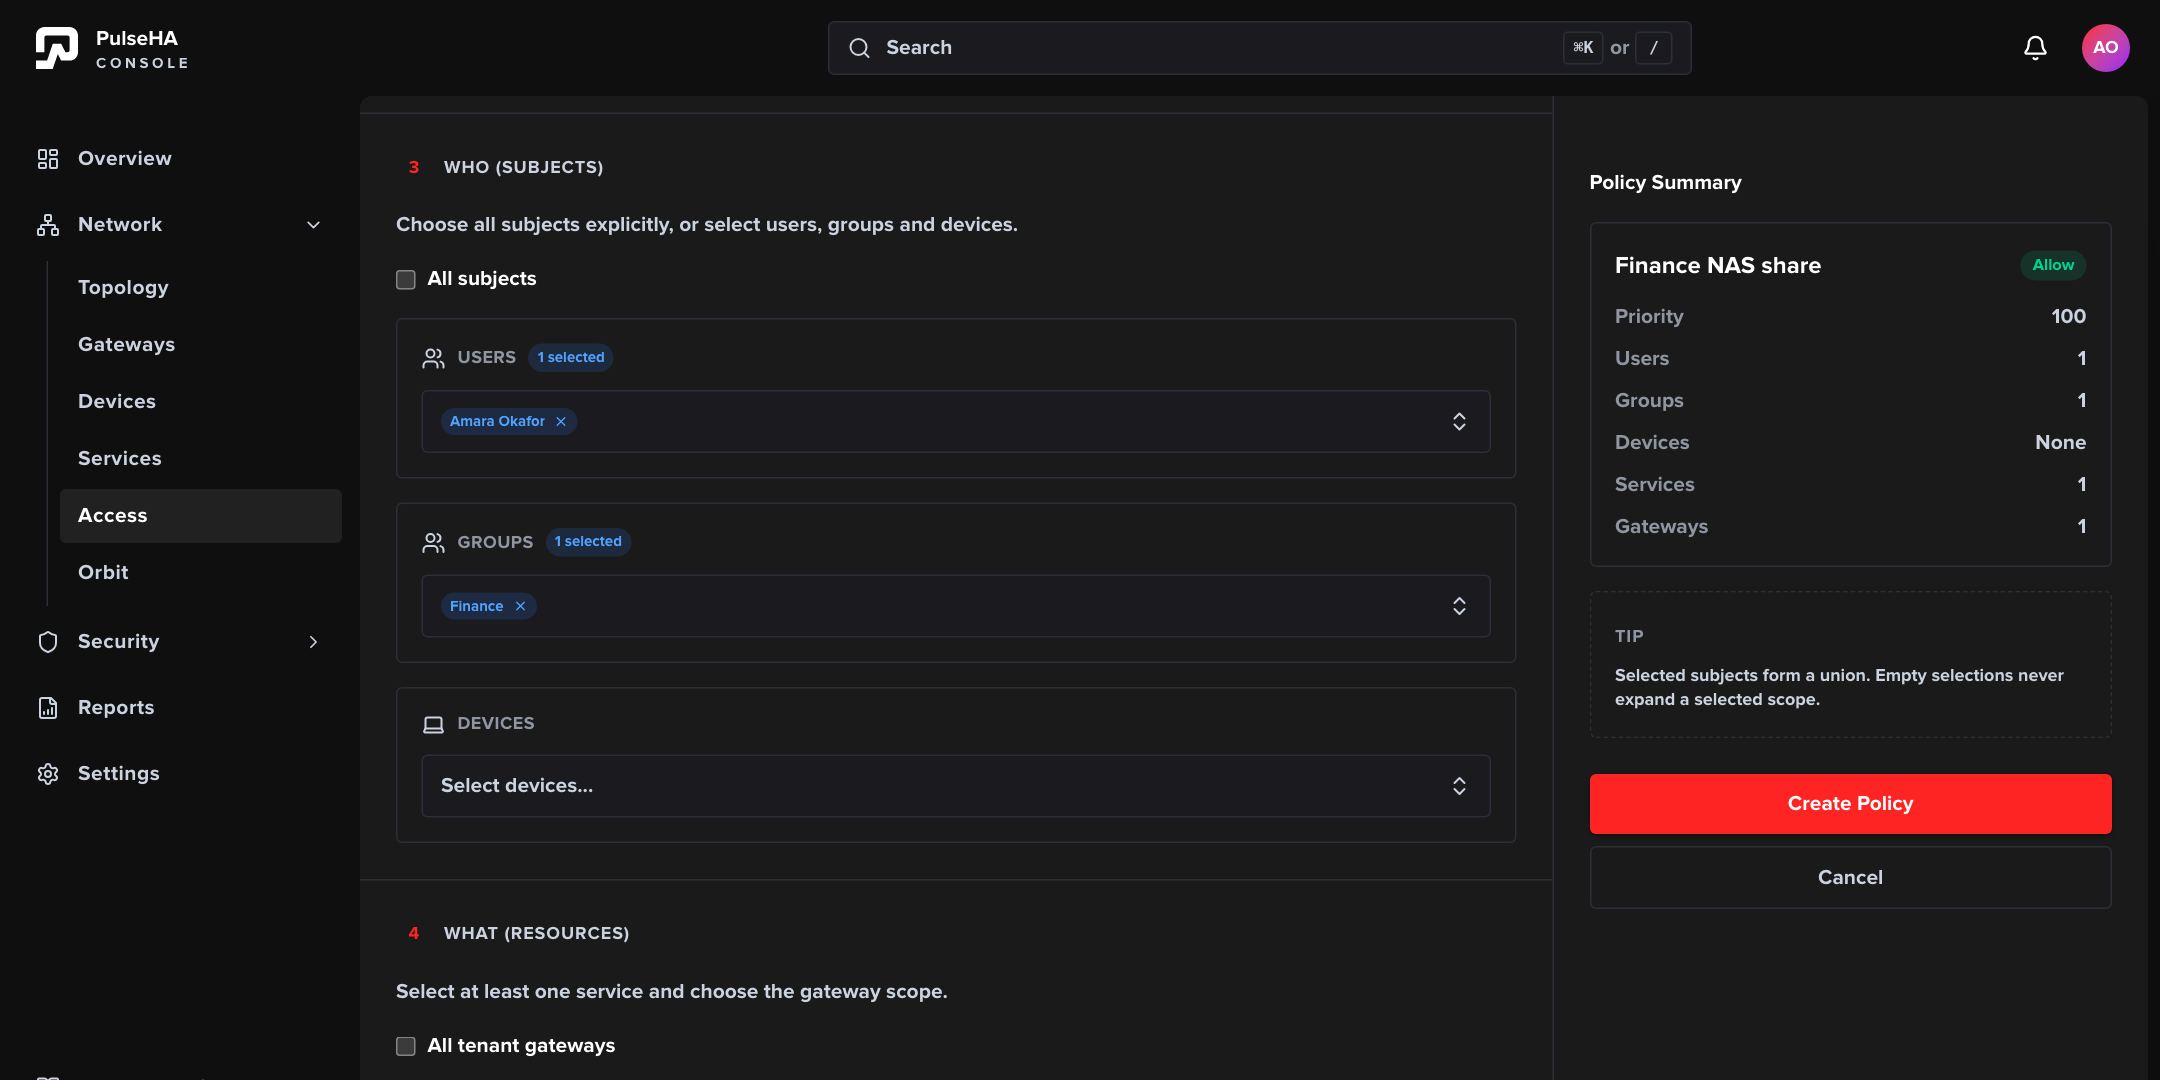
Who (Subjects) with All subjects unticked, one user and one group selected. The chips show what is in scope.
- Under 4 What (Resources):
- Under Services, choose Select services… and pick your service. This is required. If it does not exist yet, click + New service, enter its IP address or CIDR, ports and gateways, and click Create Service; it is selected for you. Access policies walks through this for SSH.
- Either tick All tenant gateways or pick the serving gateway under Gateways.
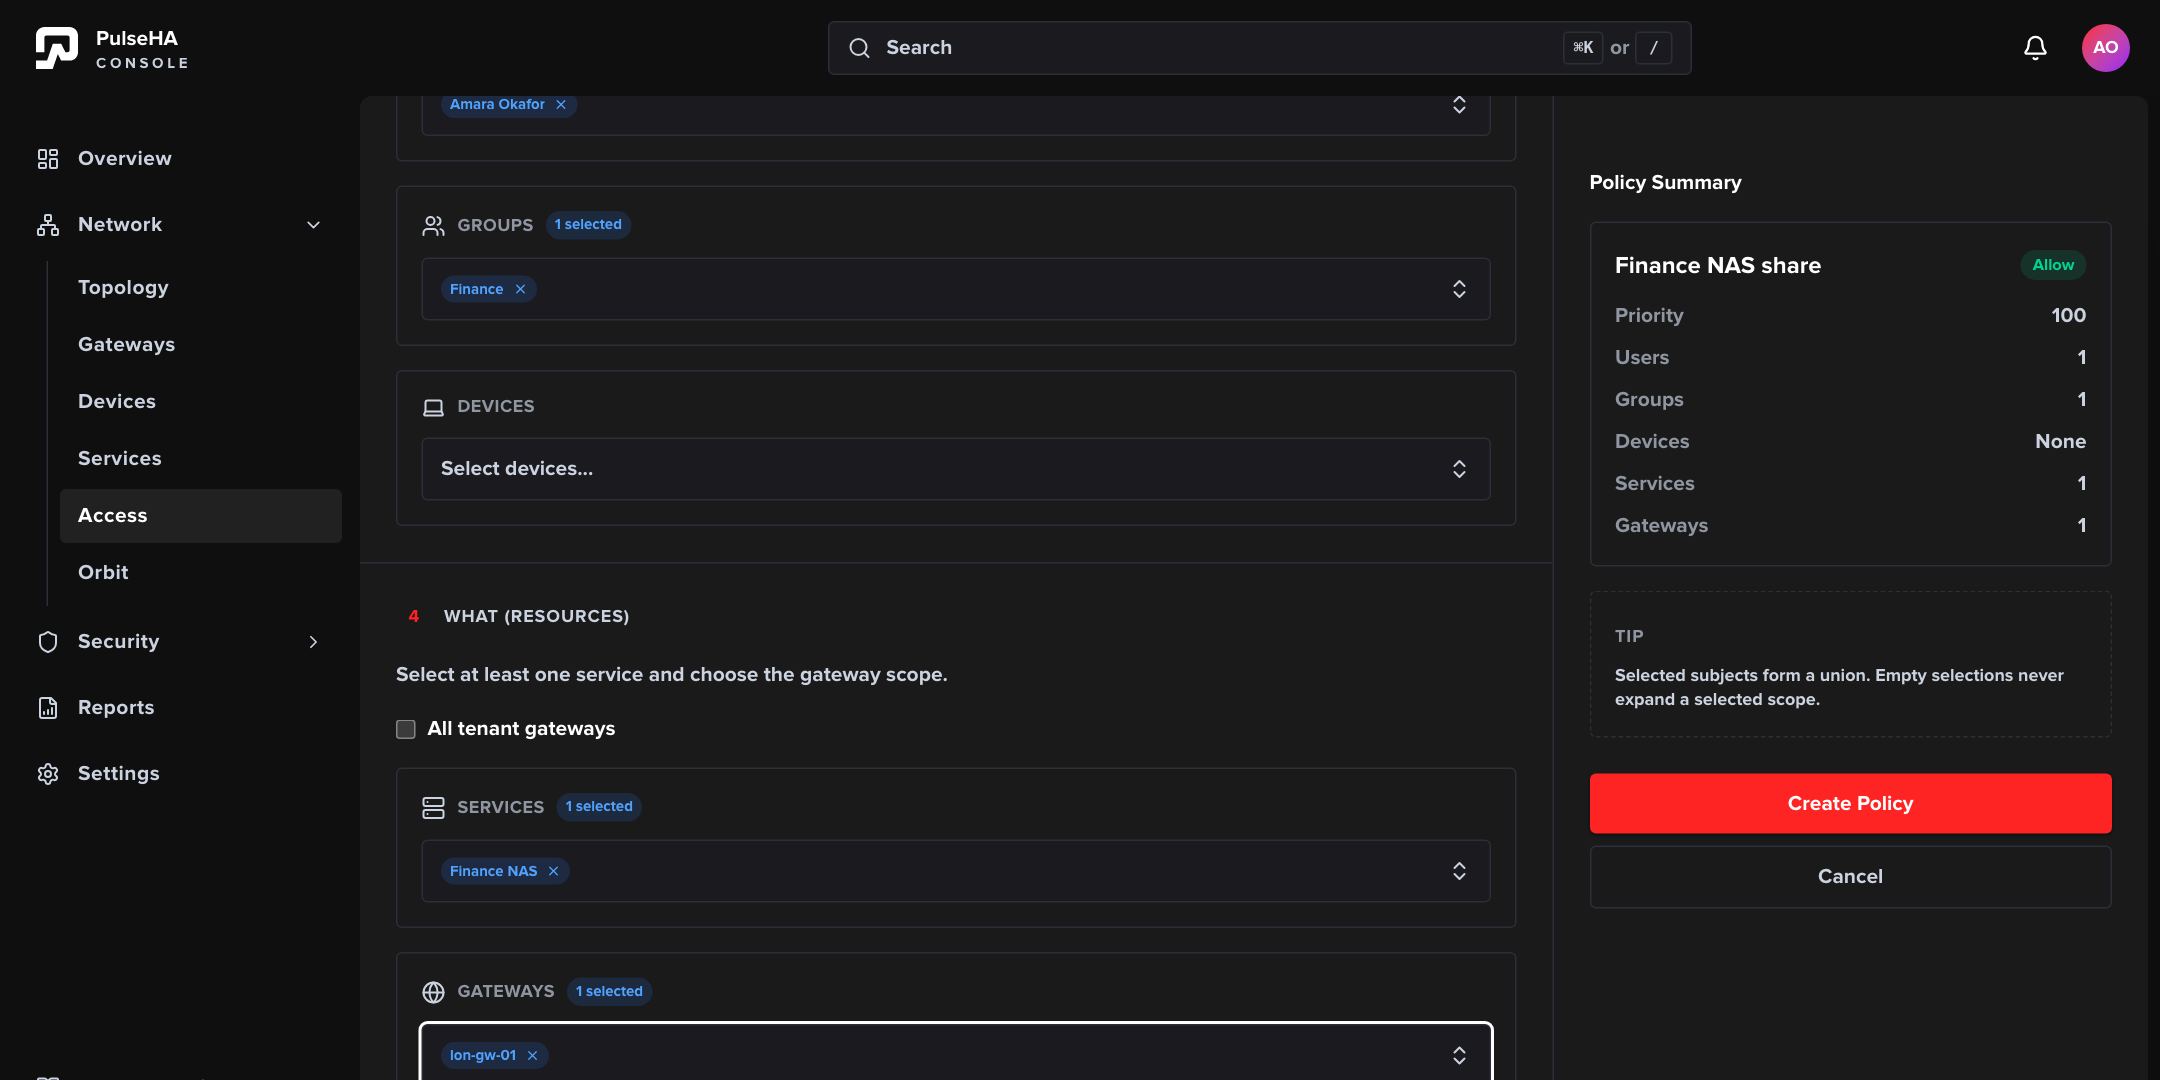
What (Resources): the service is required, and the gateway scope is either all gateways or a specific list.
- Leave 5 When (Conditions) empty. The section states that conditional policies are unavailable until their restrictions can be enforced, and the form refuses to submit with conditions attached.
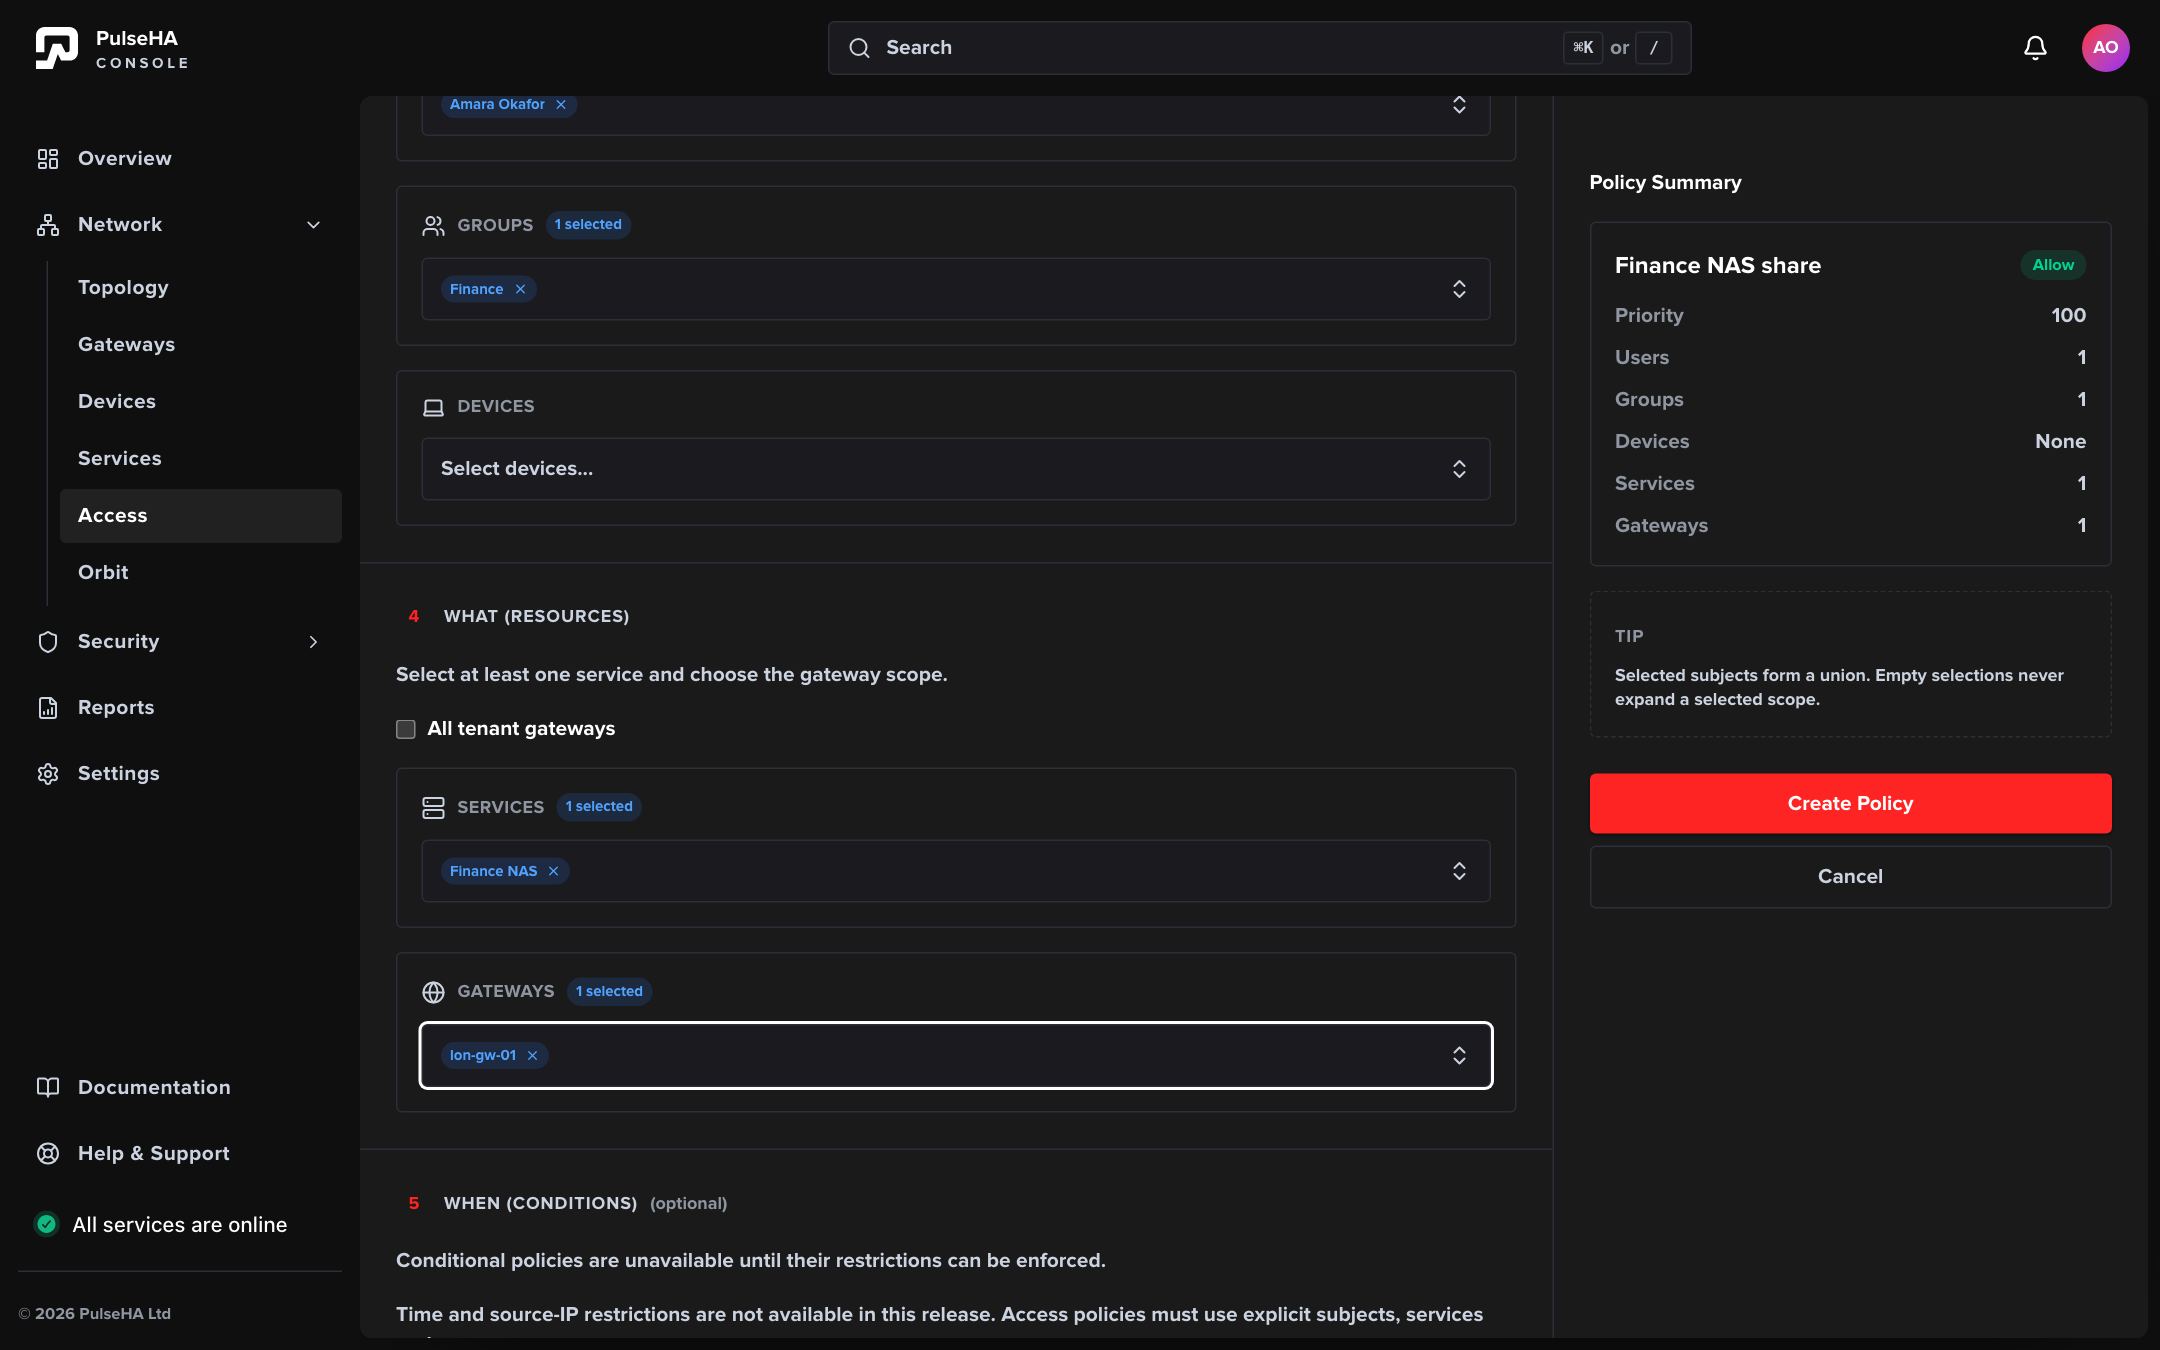
When (Conditions) stays empty. The summary card on the right is the last check before Create Policy.
- Review the summary card on the right. It lists Priority, Users, Groups, Devices, Services and Gateways. None under Users, Groups and Devices with All subjects unticked means nobody matches.
- Choose Create Policy.
What you should see#
Network → Access lists the policy with effect Allow and status Enabled. The row’s action menu offers Edit policy, Simulate access, Clone policy, View history and Delete policy.
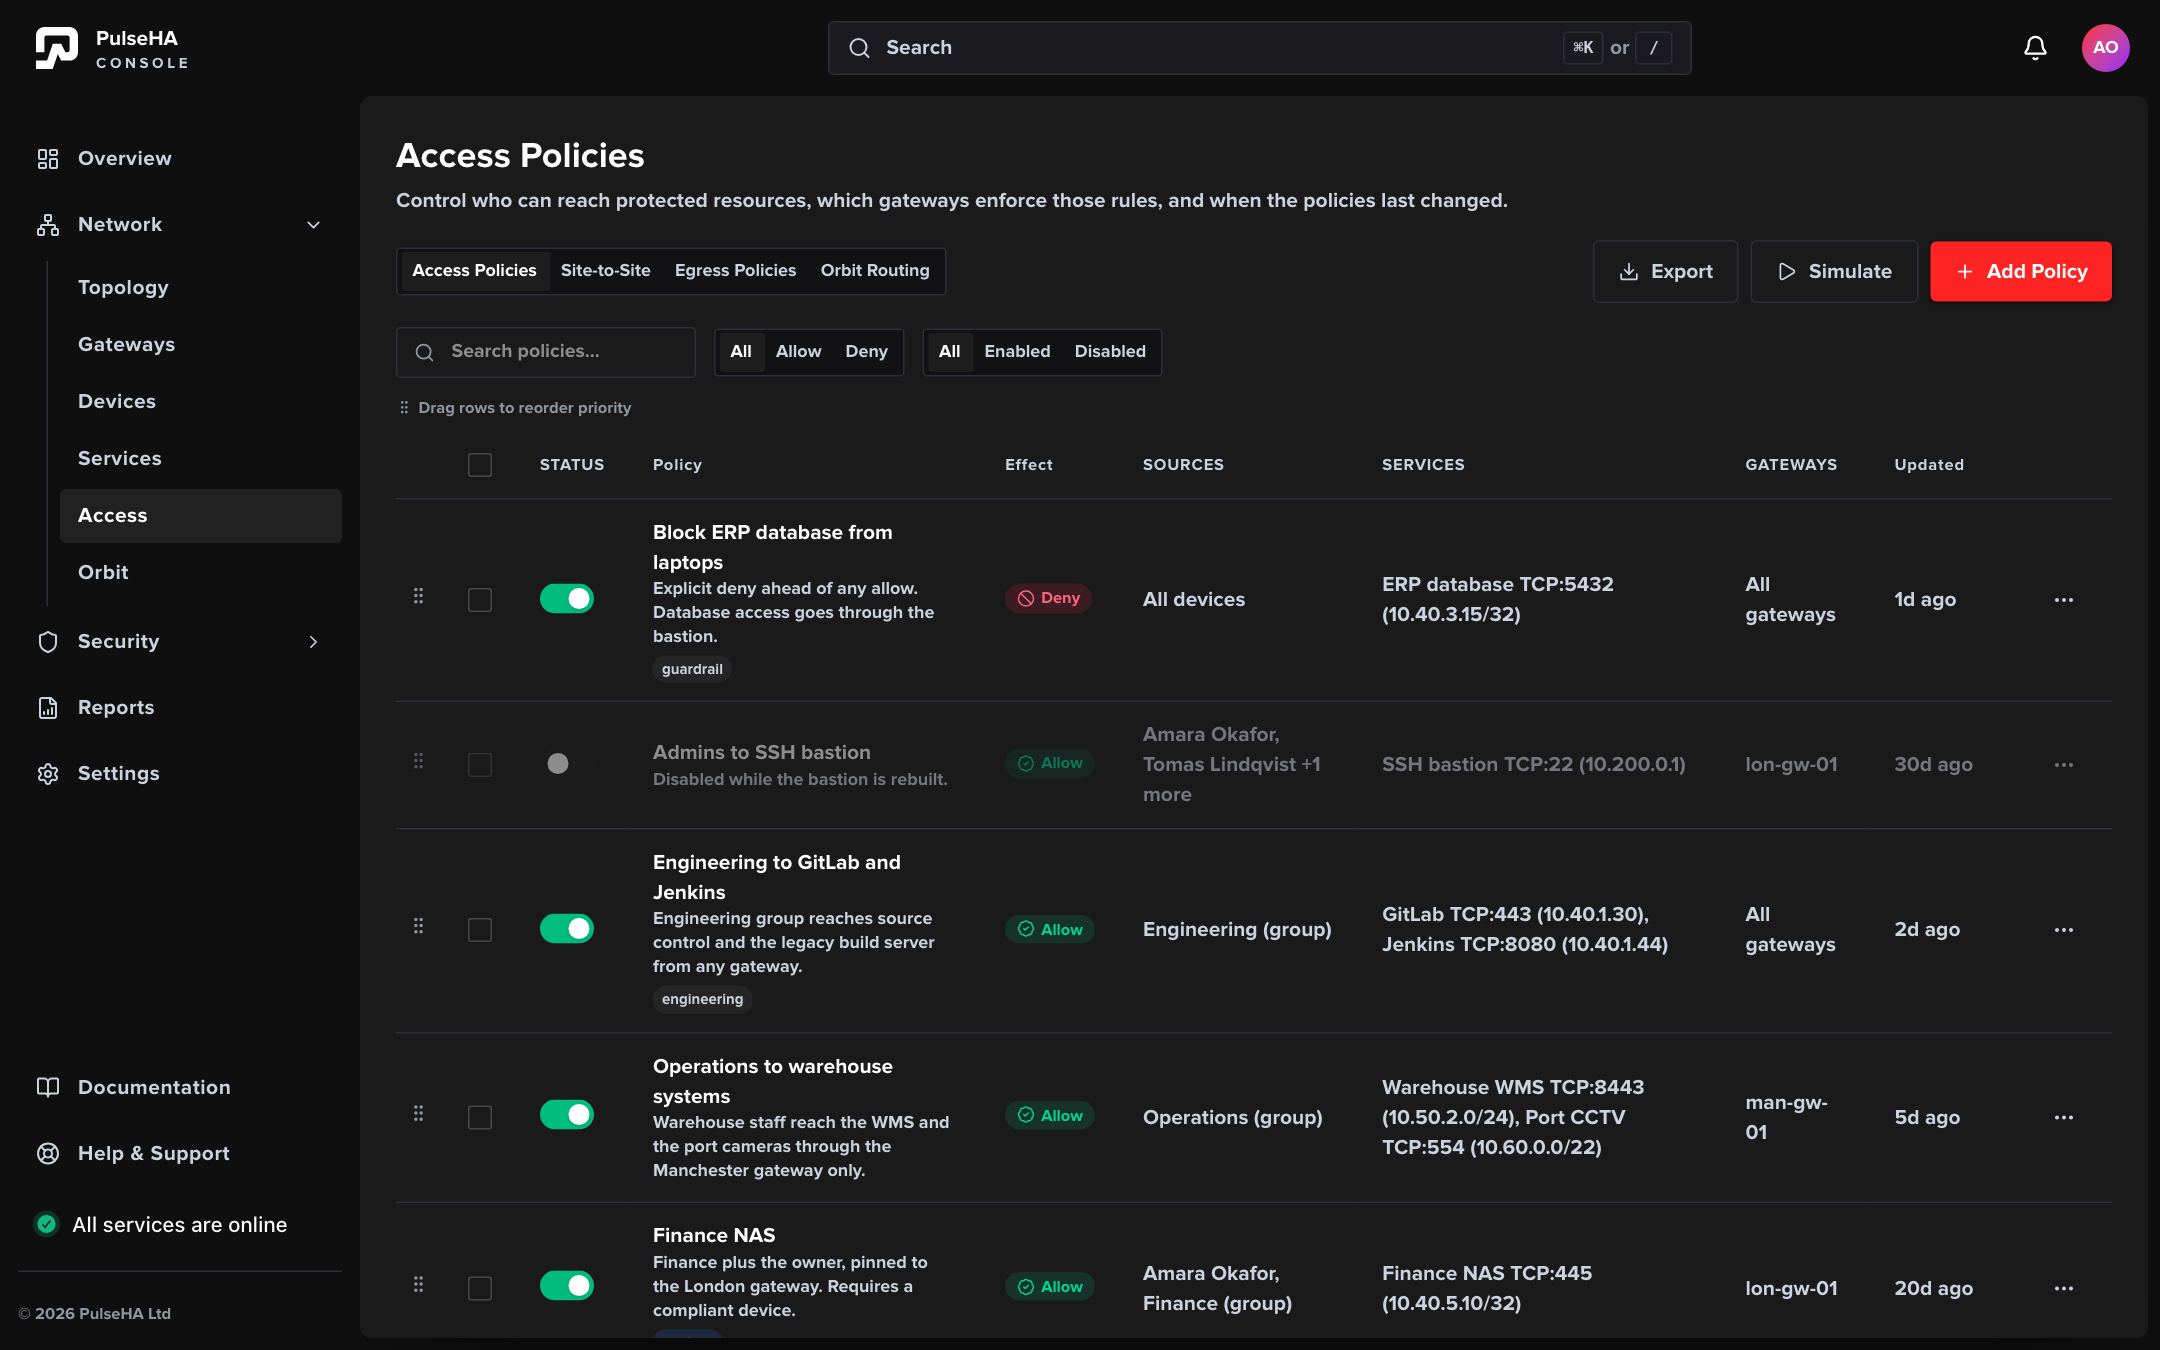
The Access Policies list. A saved policy appears here with its effect chip and its status toggle.
On the device, the route arrives on the next policy sync. On Linux, pulsectl refresh forces it and pulsectl status shows the Policy row with the last sync time. Then open the service.
How evaluation works#
The control plane rebuilds each device’s routes from the enabled policies. These rules come straight from that code:
| Rule | Effect |
|---|---|
| Disabled policies | Ignored |
| Policy with no services | Skipped entirely |
| All subjects unticked and nothing selected | Matches no one; empty selections never widen a selected scope |
| Selected users, groups and devices | Combined as a union |
| All tenant gateways unticked and no gateways selected | Skipped entirely |
| Two policies on the same service | The lower Priority number wins |
| Same priority, one Allow and one Deny | Deny wins |
| Any policy with conditions | Route publication for the organisation is refused, so keep conditions empty |
| Enforcing posture policy and a Non-compliant device | All routes for that device are stripped |
Only allowed routes are pushed to the device. Denied routes are recorded for simulation and audit.
Form validation reference#
| Message | Fix |
|---|---|
| Policy name is required | Enter a name |
| Policy name must be at least 3 characters | Lengthen the name |
| Policy name must be less than 100 characters | Shorten the name |
| A policy with this name already exists | Names are compared case-insensitively; pick another |
| Priority cannot be negative / Priority cannot exceed 10000 | Use a value from 0 to 10000 |
| Select services and any required subjects or gateways, and remove unsupported conditions. | Add a service; either tick an All box or select entries; clear When (Conditions) |
| Potential Policy Conflicts | A warning, not a block. It names the overlapping policy and which one takes precedence by priority |
Empty-state hints inside the pickers tell you what is missing upstream: No users available, No groups defined, No devices enrolled, No services defined, No gateways registered.
Troubleshooting#
- The page fails with Policy data is unavailable. Reload before making changes. One of the lists the form needs (devices, services, gateways, users, groups or policies) did not load. Reload the page.
- Save fails with Policy save could not be confirmed. Reload before retrying. The control plane did not confirm the write. Reload and check whether the policy exists before retrying.
- Policy saved but the device has no route. Check, in order: the device is Online; the policy is Enabled; the subject scope includes this user, one of their groups, or this device; the service is selected; the gateway scope includes the gateway assigned to the service; no higher-ranked Deny covers the same service; posture is not Non-compliant under an enforcing policy.
- The route appears but the application does not answer. The gateway must reach the application’s address and port. Check the service’s health in Services and the gateway’s status in Gateways.
- Unsure which policy decides. Use Simulate access from the row menu or Policy simulation, then read the decision in Audit.