Policy simulation
Preview an access decision before changing a grant.
Policy Simulation answers “would this user, on this device, reach this service through this gateway, and why?” It runs the same evaluation the control plane uses to build routes, then adds the posture, device, exit and site-to-site stages so you can see where a request would stop.
Before you start#
- You need
policies:view. Without it the page reads You need policies:view permission to use this feature. - A simulation needs at least one gateway and one service. The scenario panel shows No gateways or No services with a link when either catalog is empty.
- A simulation is a prediction from current configuration. It does not prove that a tunnel is up, that a gateway is reachable or that a firewall path is open.
- Every run is written to the audit log as a
policy.simulatedevent with the decision.
Run a simulation#
- Open Network → Access and click Simulate, or choose Simulate access on a policy row to open the simulator prefilled with that policy’s first service, gateway and subject.
- In the Scenario panel pick a User identity (or leave Any user), an optional Group override, and a Source device (or Any device). Choosing a user filters the device list to that user’s devices.
- Pick the Gateway and the Target service. Both are required.
- Click Run simulation. The pipeline strip animates through the stages and the Simulation report fills in.
- Use Copy share link to copy a URL that reproduces the scenario. Add
run=1(the link does this when both required fields are set) and the simulation runs on open. Export downloads the report; Copy summary copies a text version.
On first open the simulator preselects you as the user, and the gateway and service when the tenant has exactly one of each.
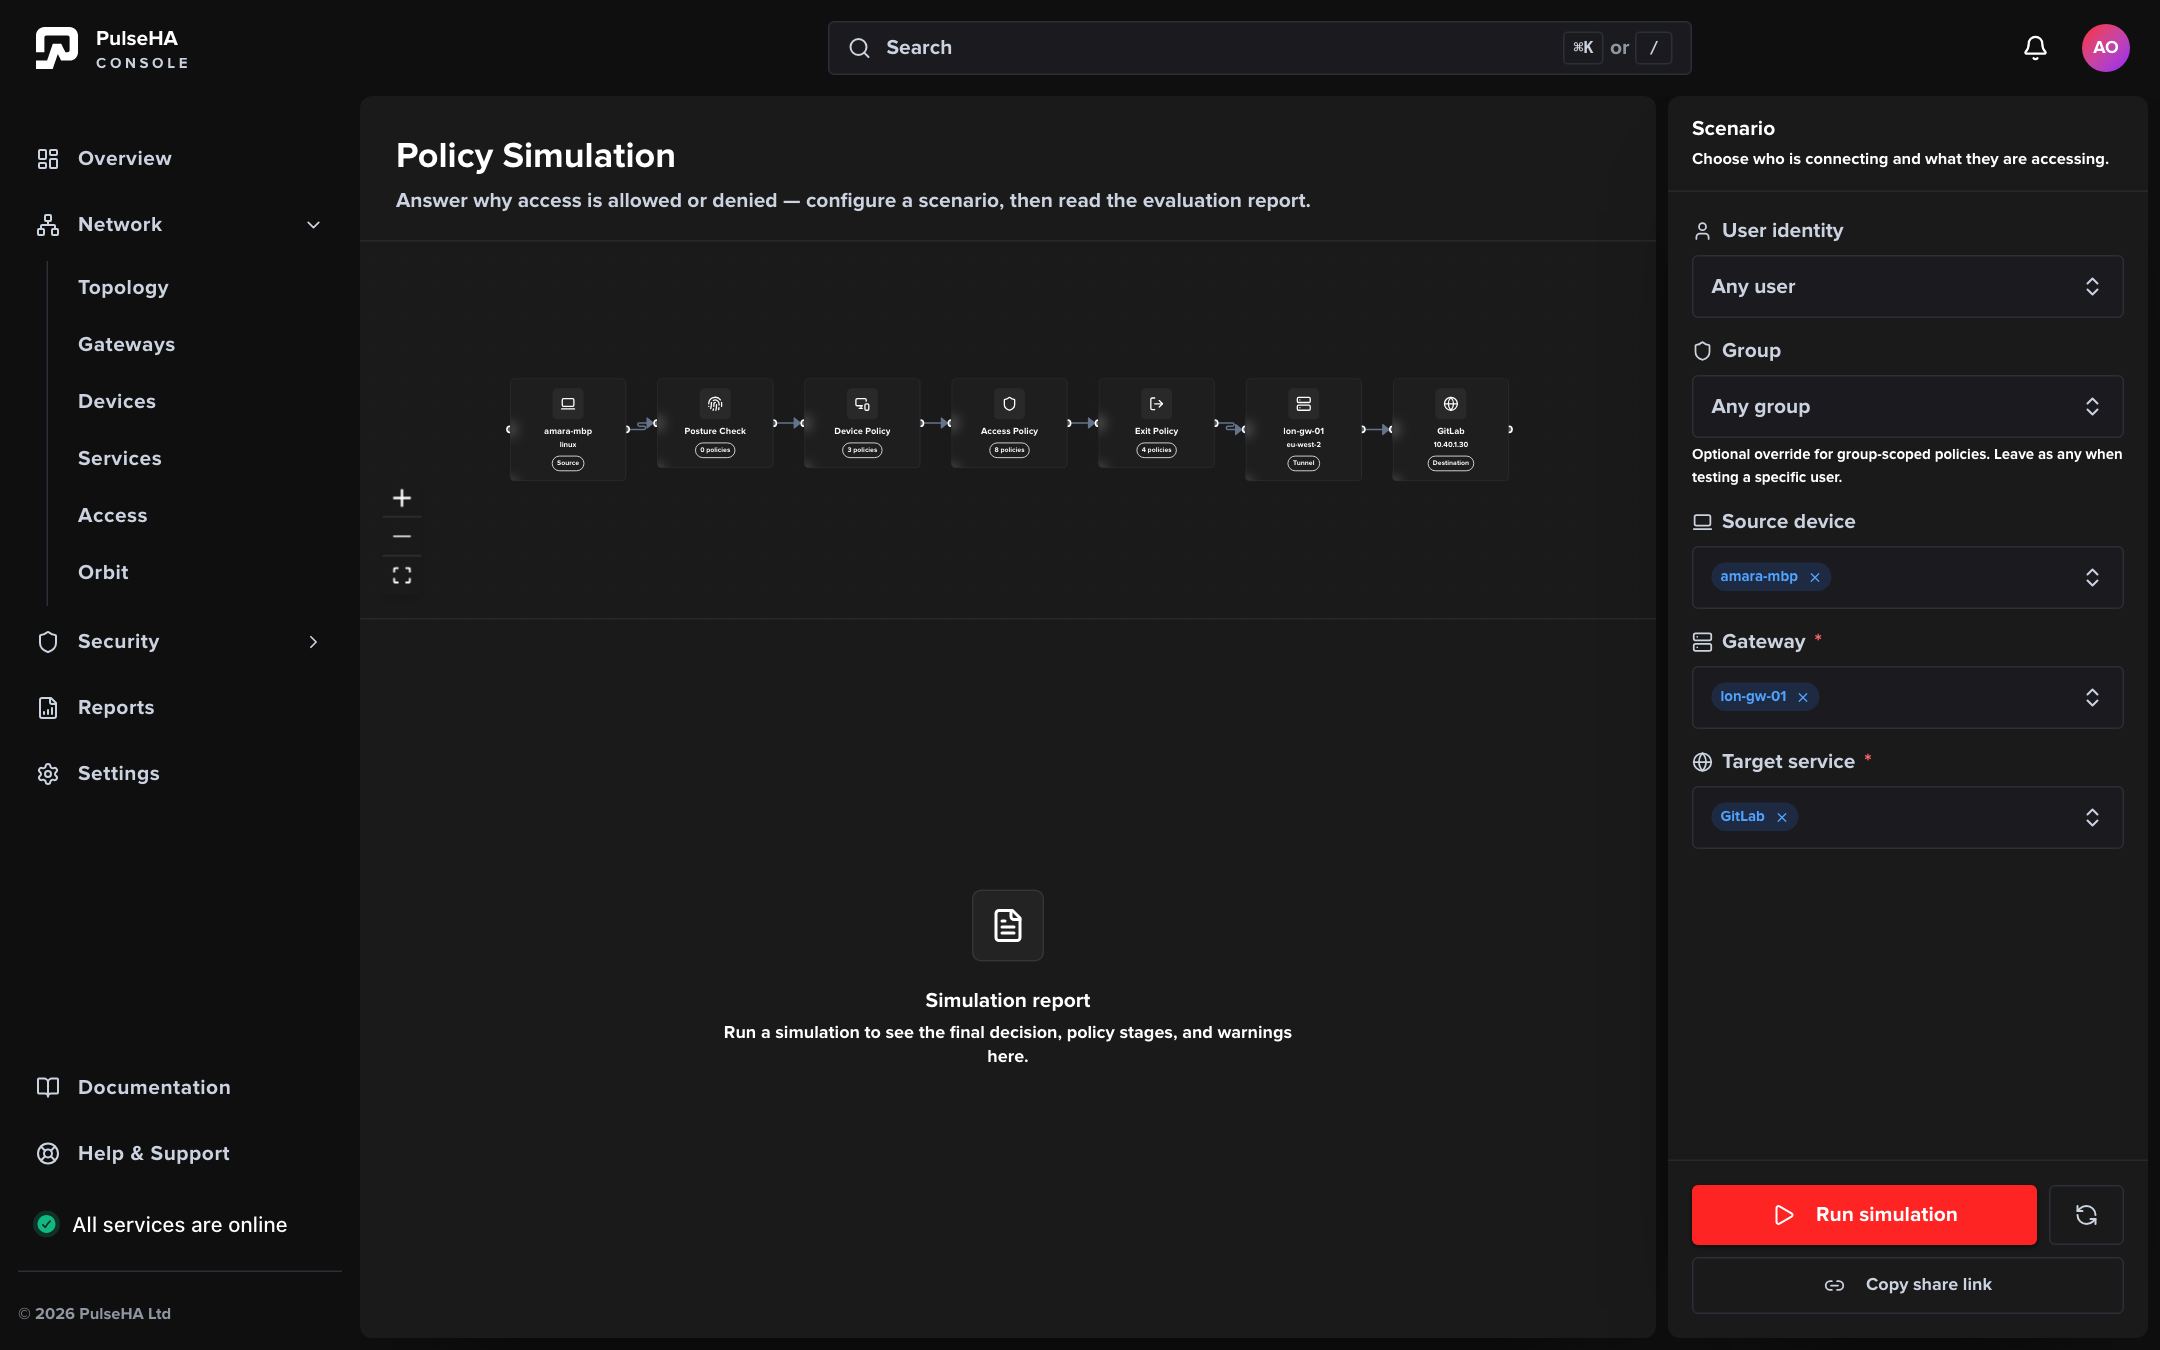
The Scenario panel holds the user, device, gateway and service pickers; Run simulation stays disabled until gateway and service are set.
Read the report#
The report header reads Access allowed or Access denied and shows Evaluated in N ms. A denial adds Blocked at <stage> by <policy> and an Edit blocking policy link; an allow adds Matched access policy and Edit matched policy. A Reason line carries the evaluator’s explanation.
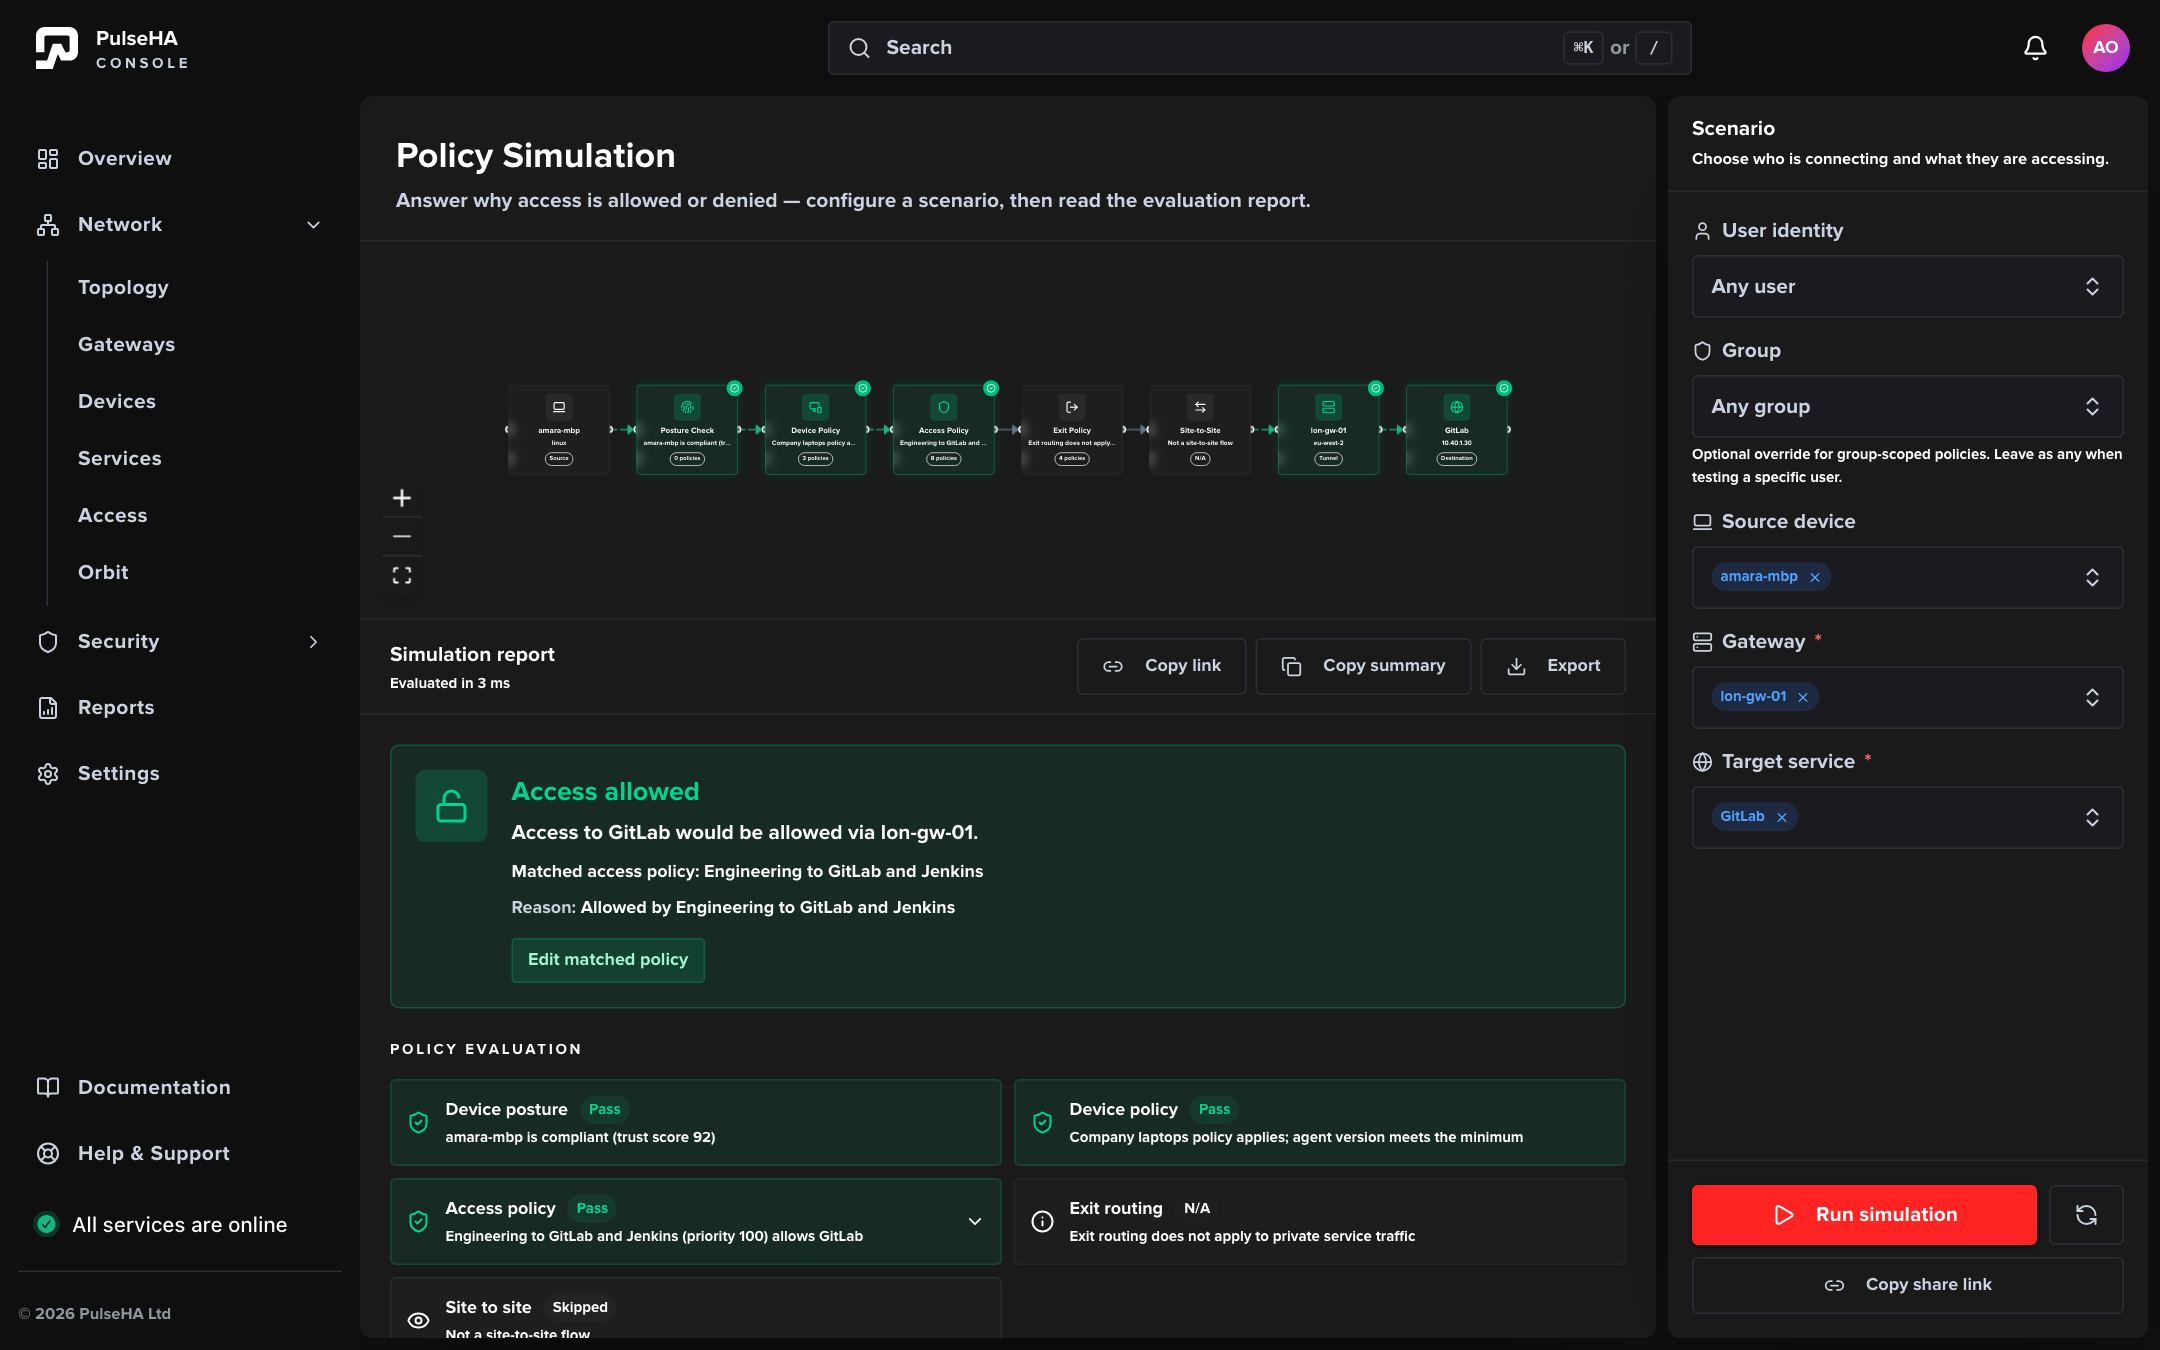
The report names the matched policy and shows one card per stage; expand a card to see which policies it considered.
Policy evaluation lists one card per stage with a status of Pass, Denied, Warning, Skipped or N/A. Expand a card to see the policies it matched and open them.
| Stage | What it checks |
|---|---|
| Posture Check | Posture policies that apply to the device |
| Device Policy | Device policies that apply. Fails when the agent version is below a policy’s Minimum Agent Version |
| Access Policy | The route decision for this device, service and gateway |
| Exit Policy | Egress policies that apply. Fails when a policy is Disallowed, or Required and the gateway is outside its allowed gateways or regions |
| Site-to-Site | Reported as N/A: site-to-site policies are not evaluated for service access |
Access policy trace lists the policies considered and marks the one that matched. Evaluation path shows the order of nodes, for example user → device → posture → device → access → exit → gateway → service.
Warnings flag context that might make the prediction wrong: the device is not connected, the device was last seen over 24 hours ago, or the selected gateway differs from the device’s last connected gateway.
If you change any scenario field after a run, a banner reads that the scenario changed and the report is out of date, with a Re-run button.
How the device is chosen#
The access stage evaluates a concrete device. The evaluator uses the Source device if set; otherwise the first device belonging to the selected user; otherwise the first device of any member of the selected group. If none resolves, the result is Access denied with reason no matching peer. Pick a device explicitly when a user has several.
Troubleshooting#
- “Simulation failed”. The control plane returned an error. The message appears under the heading; try again, and check that the service still exists.
- Access denied with “no matching peer”. No device could be resolved for the scenario. Select a Source device, or check that the user has an enrolled device with a public key and tunnel IP.
- Denied but no policy is named. The implicit default deny applied: no enabled Allow policy covers this device, service and gateway. Create one, then re-run.
- The result does not match what the user experiences. Read the Warnings. A disconnected device, a stale device, or a different gateway than the one simulated all change the live outcome. Check the device’s Connection chip on the Devices page and the service health on the Services page.
- “Some catalog data failed to load” appears above the pipeline. One of the catalogs (devices, services, gateways, users, groups or policies) did not load, so pickers may be incomplete. Reload the page.