Services
Publish a private application through reachable gateways.
A service is a private destination (an IP address, a CIDR range, or a process on the gateway host) that gateways advertise to agents. Network → Services is where you publish services, assign the gateways that can reach them and watch their health probes. Publishing a service grants nobody access; an access policy does that. You can also create a service without leaving the policy form, with + New service.
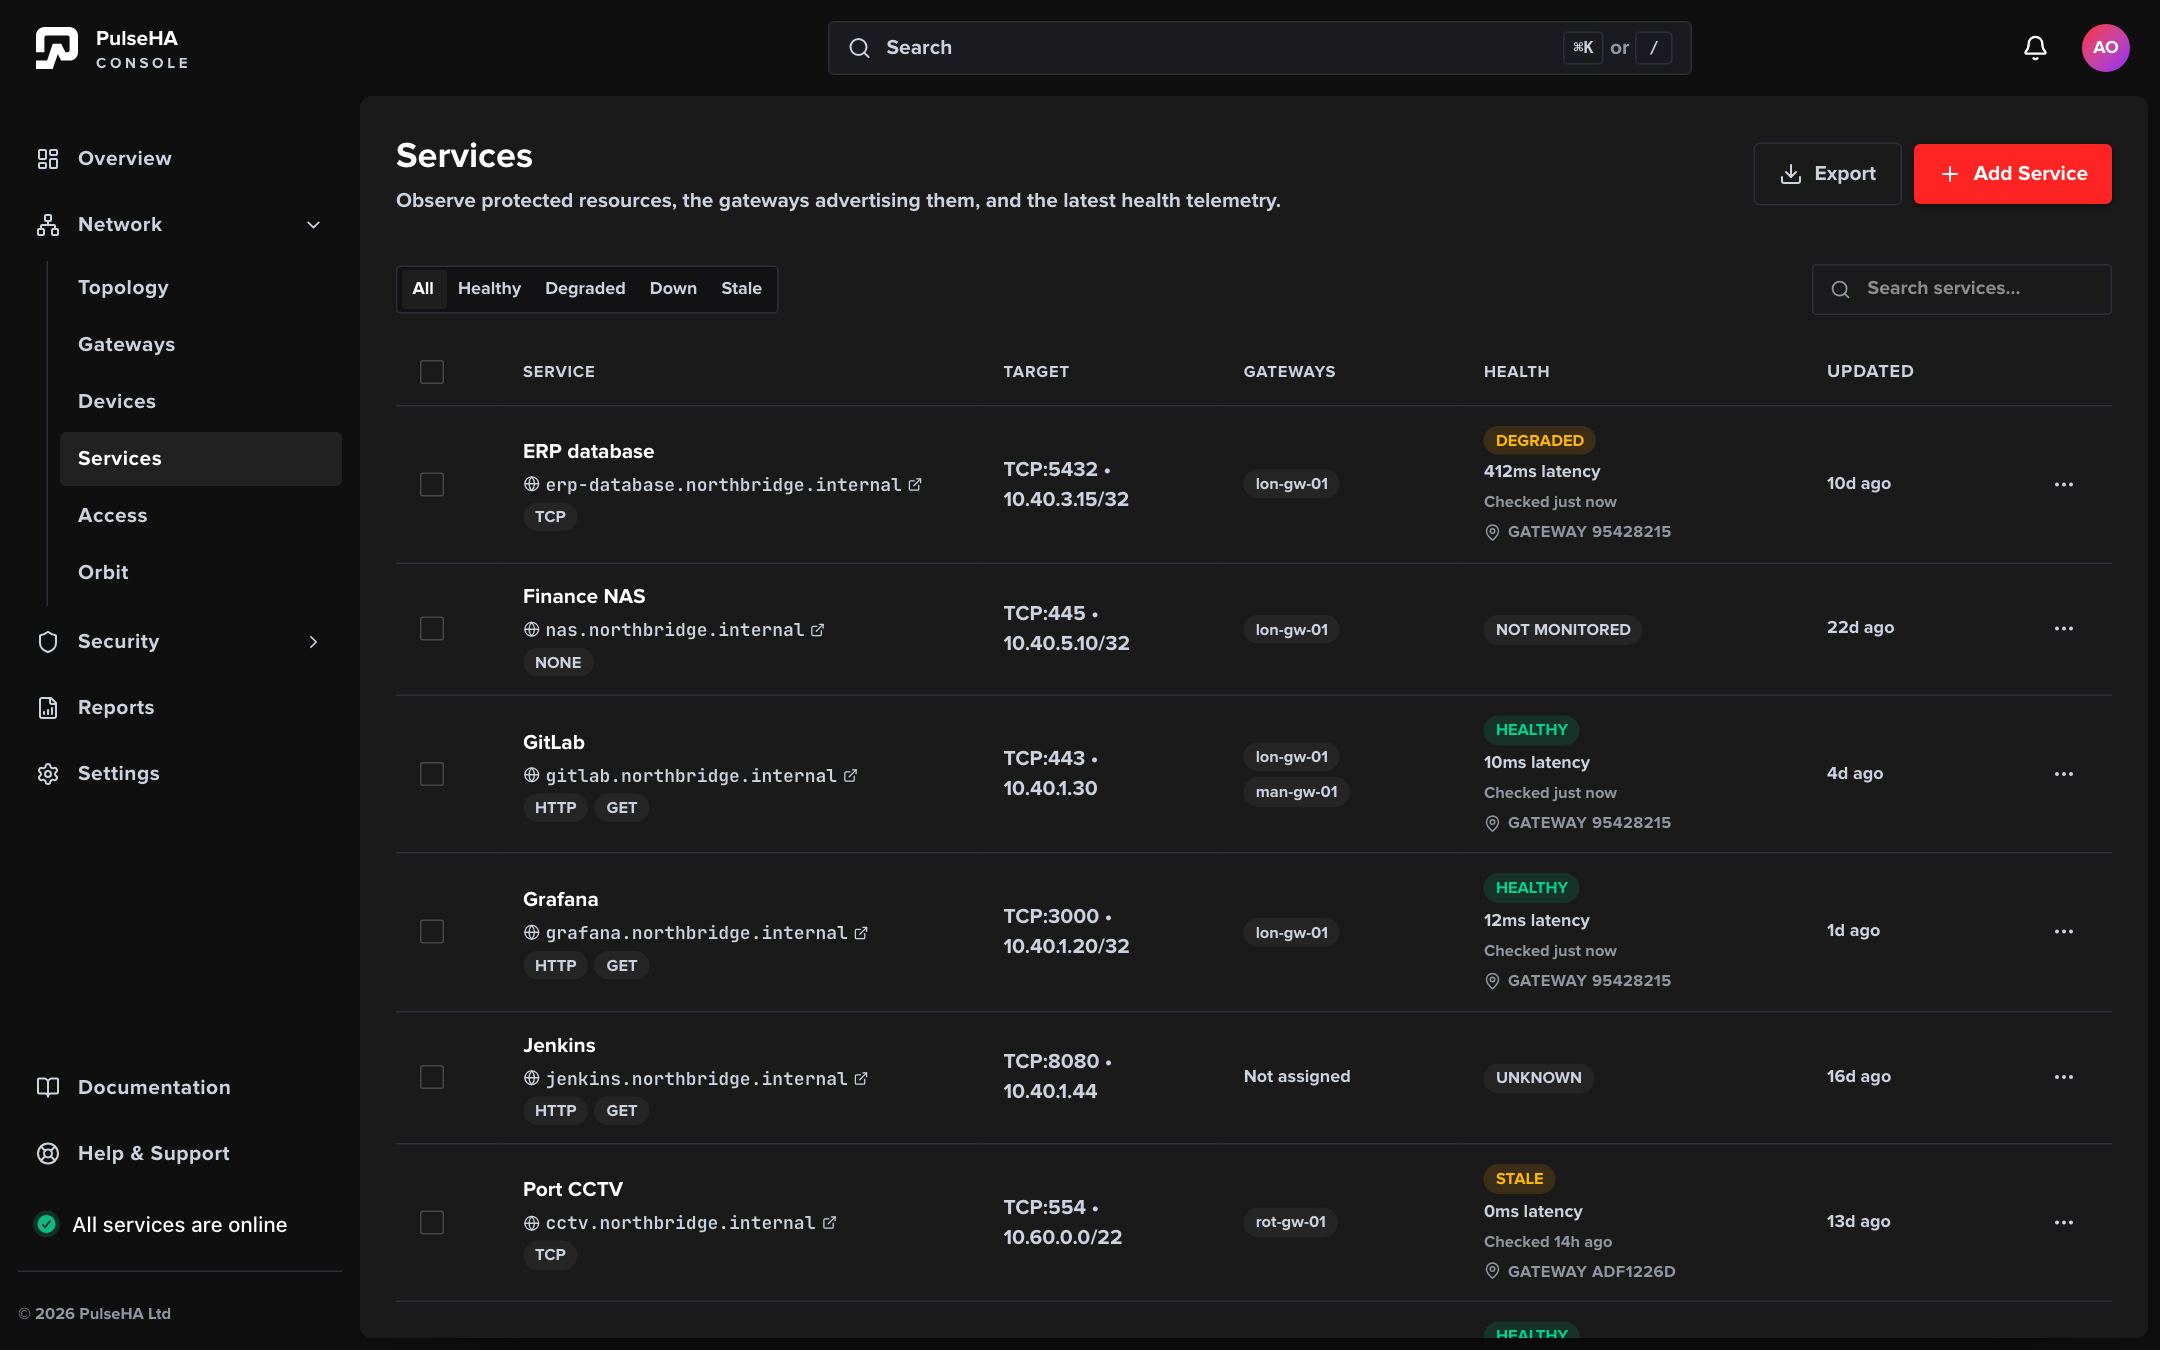
Health aggregates fresh probe results across the assigned gateways; Port CCTV shows STALE because its only gateway has not probed it for 14 hours.
Before you start#
- Reading the list needs
services:view. Add Service, Edit service and Delete service needservices:create,services:updateandservices:delete, which owners and admins hold by default. The drawer’s Activity tab needsaudit:view. - At least one gateway should exist and be able to reach the destination. The gateway picker is empty otherwise (No gateways registered.).
- Know the destination’s IP address or CIDR. Hostname destinations are not supported: gateways match traffic on IP addresses, and none of them resolves names yet.
- If DNS is enabled under Settings → DNS, each service gets a name under your suffix (default
pulseha.internal). This is private service discovery and is unrelated to Secure Web filtering.
Publish a service#
- Open Network → Services and click Add Service.
- Under Basic Information enter a Service Name (required), an optional Description and an optional DNS Name. Leave DNS Name blank to derive it from the service name when auto-generation is on.
- Under Network Address, optionally pick an Application Type: SSH, RDP, Web, Database, API or Custom. SSH, RDP and Web fill in the usual protocol, ports and health check for any of those fields you have not changed yourself. See Application types.
- Pick an Address Type:
- IP / CIDR: enter the IP address or CIDR, for example
10.0.0.5or10.0.0.0/24. Do not include a port. - Gateway Host: a service listening on the gateway itself. There is no address to enter.
- IP / CIDR: enter the IP address or CIDR, for example
- Enter Ports: one port, a list or ranges, for example
22,22, 80, 443or8000-8100. Leave it empty for every port of the protocol. A Gateway Host service takes exactly one port. See Ports. - Choose the Protocol: TCP or UDP. Gateway Host is TCP only.
- Under Health Checks choose a Probe Type: HTTP, TCP, UDP or None. For HTTP set the HTTP Method (GET, HEAD or POST), Health Check Path, Expected Status Code and optional Expected Body. Set the Check Interval (seconds); the default is 30. None shows the service as Not monitored and runs no probes.
- Under Gateway Assignment select the gateways that can reach the destination. Leave it empty to advertise on all gateways. For Gateway Host, select the gateway that runs the process; its tunnel IP becomes the service address.
- Click Create Service. The new service appears in the list.
If any gateway that would serve the service runs a release older than 2.21.8 and the ports are a list or a range, the form shows Some gateways enforce only one port. See Older gateways.
Application types#
The type labels the service and can fill in fields for you. A preset only fills fields you have not typed in or picked yourself, and you can change anything it fills.
| Application type | Protocol | Ports | Health check |
|---|---|---|---|
| SSH | TCP | 22 | TCP |
| RDP | TCP | 3389 | TCP |
| Web | TCP | 443 | HTTP |
| Database, API, Custom | Unchanged | Unchanged | Unchanged |
Until you pick a probe yourself, the health check follows the type and ports. Web gets an HTTP check. With no ports, the check is None. Otherwise it is a TCP check (UDP for a UDP service) on the lowest port, every 30 seconds. A new service with no type and no ports therefore starts with None.
Changing the type of an existing service on Edit service only changes the type. It never overwrites the protocol, ports or health check that were saved.
Ports#
Ports takes single ports and ranges separated by commas. Spaces are allowed.
- Each port is 1 to 65535. A range is written low to high, such as
8000-8100. - The list is saved in a standard form: sorted, with overlapping or adjacent entries merged.
443, 80,22, 21-23is saved as21-23,80,443. The field shows Saved as with that form while you type. - At most 32 entries after merging.
- Empty means every port of the protocol.
- A Gateway Host service takes exactly one port.
The address must not include a port. 10.0.0.5:22 is rejected; enter 10.0.0.5 as the address and 22 under Ports.
Validation messages#
The console checks the form before sending it, and the control plane applies the same rules with the same messages.
| Message | Fix |
|---|---|
| Service name is required. | Enter a name |
| Address value is required. | Enter an IP address or CIDR |
| Hostname destinations are not supported yet. Use an IP address or CIDR. | Enter the server’s IP address, or a CIDR |
| Put the port in the Ports field, not the address. | Remove :port from the address and enter it under Ports |
| Ports: ‘70000’ is out of range (1-65535) | Use ports from 1 to 65535 |
| Ports: range 90-80 is reversed | Write the range low to high: 80-90 |
| Ports: at most 32 entries | Merge ports into ranges, or split the service |
| Ports: ‘x’ is not a port or a range like 8000-8100 | Use numbers and ranges only |
| Ports: empty entry in ‘22,,80’; separate ports with single commas | Remove the extra comma |
| Port is required for gateway host services. | Enter the port the process listens on |
| gateway_local services take a single port | Enter one port for a Gateway Host service |
| Gateway host services support TCP only. | Choose TCP |
| Health interval must be greater than zero. | Set a check interval |
| UDP probes require the service protocol to be UDP. / UDP services must use a UDP health probe. | Match the probe to the protocol |
| TCP probes require the service protocol to be TCP. / HTTP probes require the service protocol to be TCP. | Match the probe to the protocol |
| Port is required for TCP or UDP probes. | Enter a port, or choose None |
| HTTP method is required. | Choose GET, HEAD or POST |
| Expected status must be between 100 and 599. | Enter a valid HTTP status code |
Older gateways#
Gateways older than 2.21.8 enforce only the lowest port of a list or range until they are updated. Traffic to that port works; traffic to the other ports is dropped. Nothing extra is opened.
The console warns wherever this applies: Some gateways enforce only one port on the service forms, the drawer and the policy form, naming each gateway, its version and the one port it enforces, and a Gateway update needed chip in the list. Update those gateways from Gateways.
Read the list#
Filter with All, Healthy, Degraded, Down or Stale and search by name, description or address. Health data refreshes every 30 seconds.
| Column | Meaning |
|---|---|
| Service | Name, the DNS name as a link when DNS is enabled, and the probe type chip |
| Target | Protocol, ports and address, such as TCP:22,80,443 • 10.0.0.5, or Gateway host. Chips below show the application type, Not enforced and Gateway update needed when they apply |
| Gateways | Assigned gateways, or Not assigned when it is advertised everywhere |
| Health | Status chip, latency, Checked time and the reporting gateway |
| Updated | Last change |
Health is aggregated across gateways. Only probe results from the last 5 minutes count; the worst fresh result wins.
| Status | Meaning |
|---|---|
| HEALTHY | Latest fresh probe passed on every reporting gateway |
| DEGRADED | A fresh probe reported degraded |
| DOWN | A fresh probe failed |
| STALE | No probe result within 5 minutes |
| UNKNOWN | No probe result at all |
| NOT MONITORED | Probe type is None |
Click a row to open the drawer. Overview shows Avg Latency, Assigned Gateways, Last Probe and Protocol, a per-gateway table (Gateway, Health, Latency, HTTP Status, Last Check) and the rows Health, Application Type (when set), Protocol, Address, Address Type, DNS, Health Probe, Probe Path, Probe Interval and Last Updated. Protocol shows the protocol and the saved ports, for example TCP:22,8000-8100, or the protocol alone when the service covers every port. A Not enforced or Some gateways enforce only one port warning appears above the tiles when it applies. Activity shows audit events for the service.
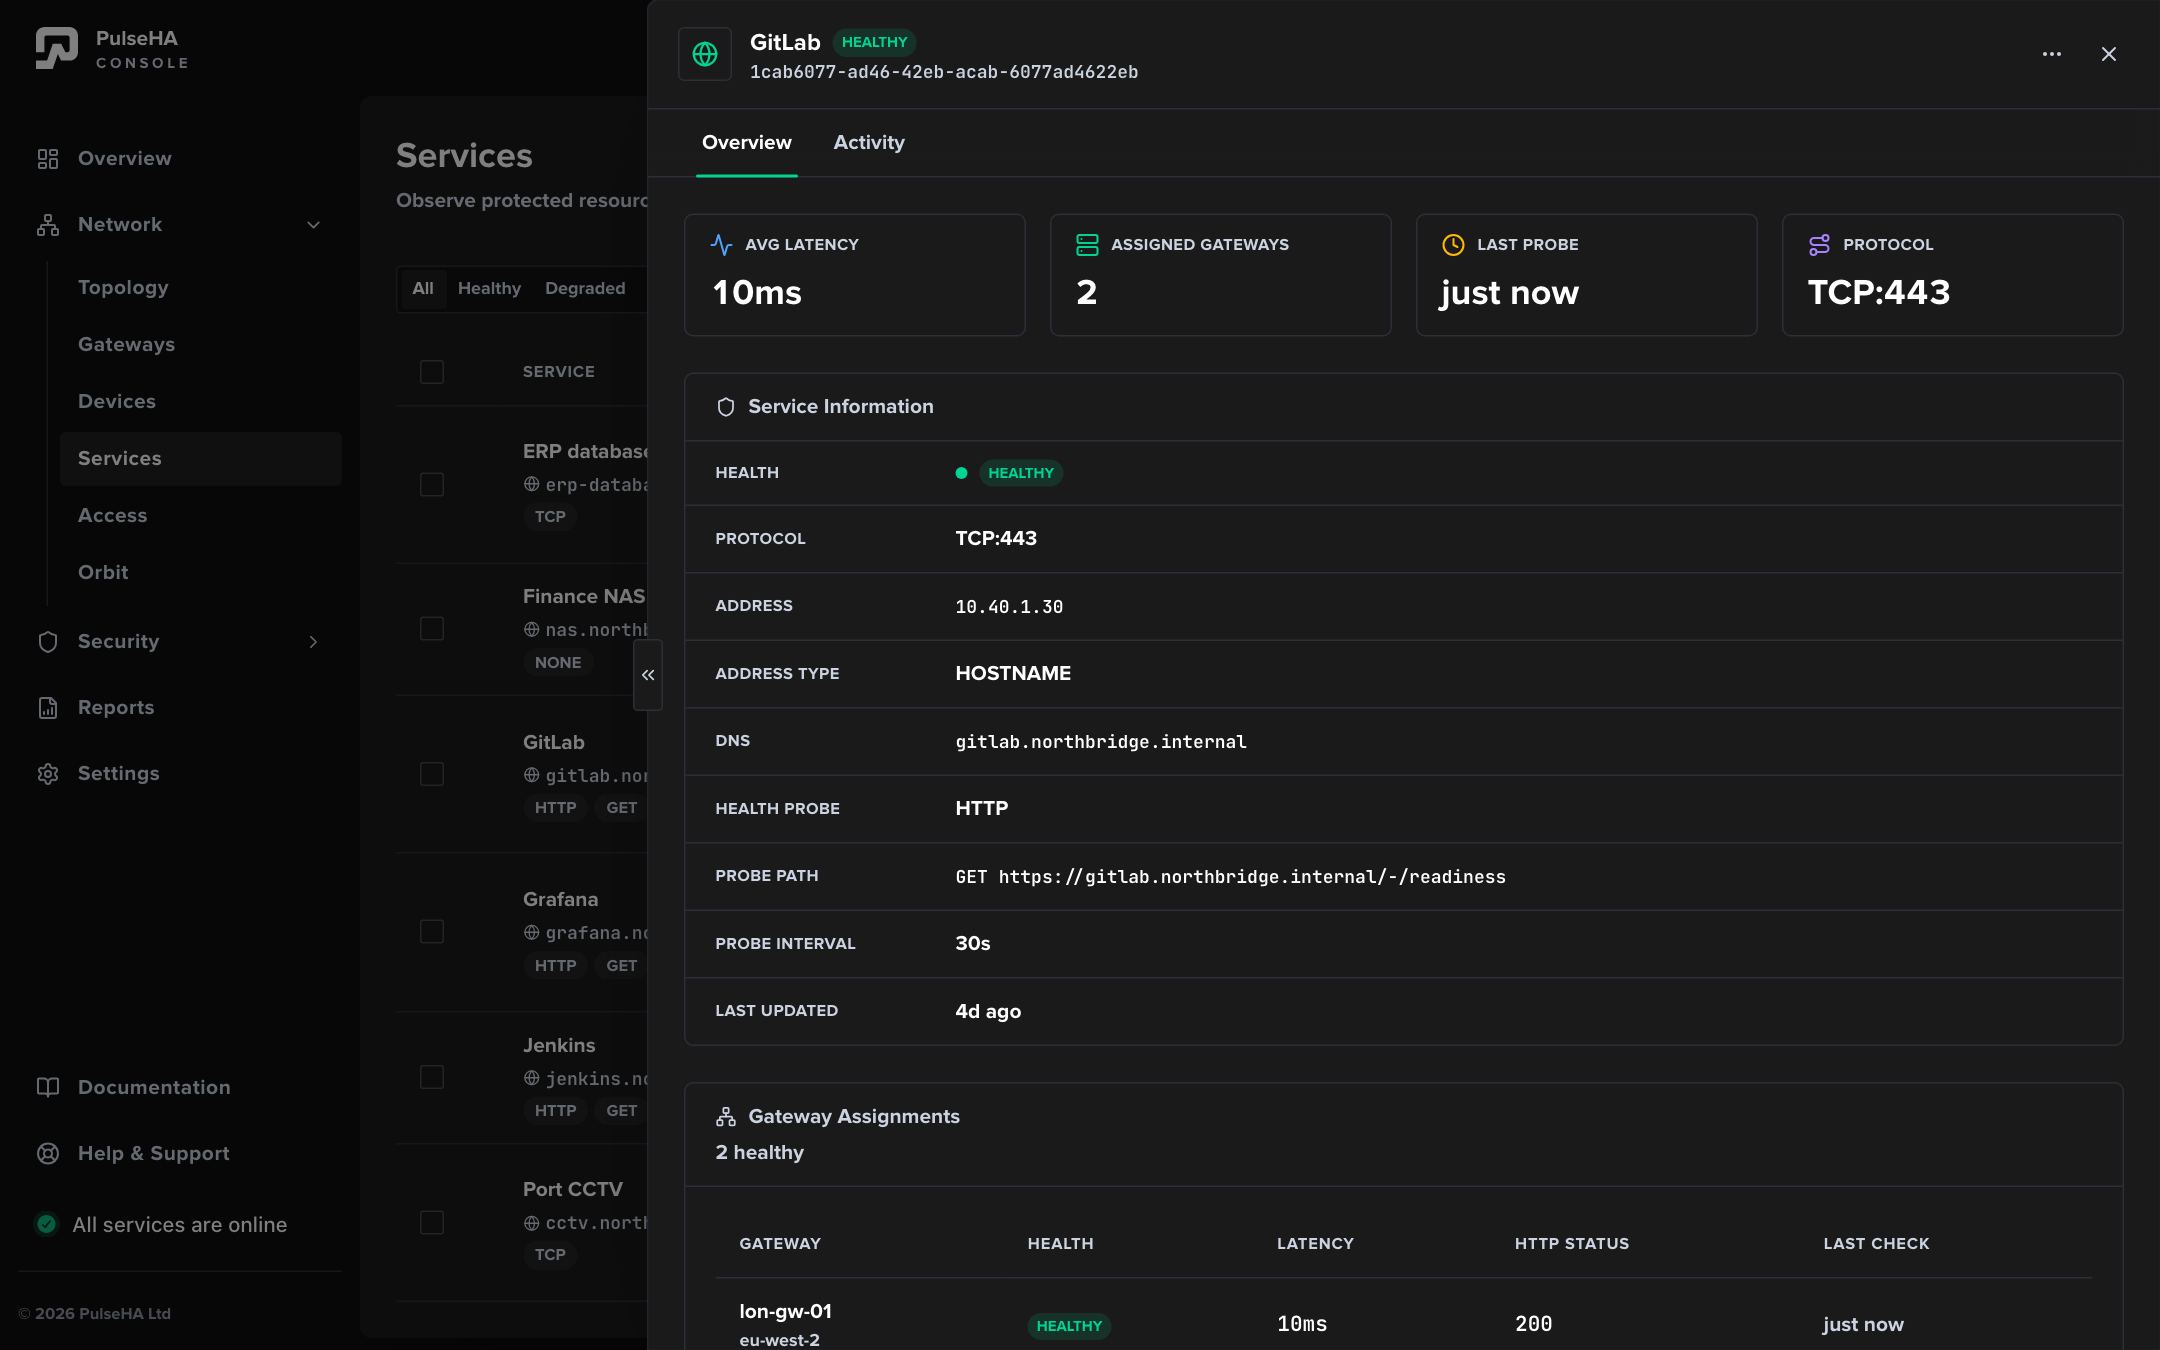
The drawer shows average latency and last probe time, then one row per gateway with its own health, latency and HTTP status.
Edit or delete a service#
Choose Edit service from the row menu, change the fields and click Save Changes. Services saved before port lists existed show their single port in Ports; you can extend it to a list or range. If the service references a gateway that has since been revoked, the edit form shows N revoked gateway(s) referenced. with Remove all; the list shows an amber warning with This service references revoked gateways. Edit to update. Revocation does not clean up assignments on its own.
Convert a hostname service#
Services created with the old Hostname address type are kept. If the address is a DNS name rather than an IP address, gateways cannot match traffic to it, so the service is not enforced: no device gets access to it through any policy. The list shows a Not enforced chip whose tooltip reads Hostname destinations are not supported yet. Use an IP address or CIDR., and the drawer shows the same warning.
- Choose Convert to IP address from the row menu, or from the warning in the drawer. The edit page opens with a Not enforced warning.
- Click Convert to IP address. The address type changes to IP / CIDR, the address is cleared, and the form shows the hostname the service used to have.
- Enter the IP address or CIDR the service should reach, and click Save Changes.
A Hostname service whose address is already an IP address is still enforced and shows no warning, but like every service still marked Hostname, it cannot be saved until it is converted. Use Edit service and the Convert to IP address button on the edit page.
Delete a service#
Delete service asks for confirmation; the action cannot be undone. Select several rows and click Delete to remove them together.
Troubleshooting#
- Health shows STALE for every service. No gateway has posted a probe within 5 minutes. Check the assigned gateways are Online on the Gateways page.
- Health shows UNKNOWN after creation. No probe has run yet. Wait one interval, or check that the probe type suits the protocol.
- A service is healthy but users cannot reach it. Health proves the gateway can probe the destination, not that a user is allowed. Check access policies and run a simulation.
- The DNS link does not appear. DNS is disabled, or the DNS settings call failed. See Configure DNS.
- “You don’t have permission to view services.”, “The service API is having trouble. Try again.” or “Couldn’t reach the service API. Check your connection and try again.” The first is a role issue; the others are transient. Use Retry.
- Users reach one port of a service but not the others. A gateway serving it runs a release older than 2.21.8 and enforces only the lowest port. Look for Gateway update needed in the list and update the gateway named in the drawer’s warning.
- A service shows Not enforced. Its address is not an IP address or CIDR. Convert it.
- The policy editor says a policy has no services. Access policies must reference at least one service, and the control plane skips policies without services when it builds routes.