Start guide
Connect a device, publish an application, and grant first access.
This guide takes a new organisation from an empty Console to one working private-application connection. Follow it once, end to end, before you roll PulseHA out to other people.
Before you start#
You need:
- A Console account in the organisation you are setting up. Enrolling a gateway and publishing a service need the owner or admin role. Adding a device and creating an access policy also work with the user role.
- A Linux host with
sudoand outbound HTTPS that can reach the application you want to publish. This becomes your first gateway. Gateway enrollment is Linux-only. - A laptop or desktop to enrol as the first device. Linux, Windows and macOS agents ship today. iOS and Android are coming soon.
Nothing is reachable until you create an access policy. A connected device with no policy has no routes.
The five steps#
The Console’s Overview page (Network) shows a setup checklist with the same order: connect a gateway, enrol a device, publish a service, create an access policy. The quick actions at the top (Add Device, Add Gateway, Create Policy) only appear for roles that are allowed to use them.
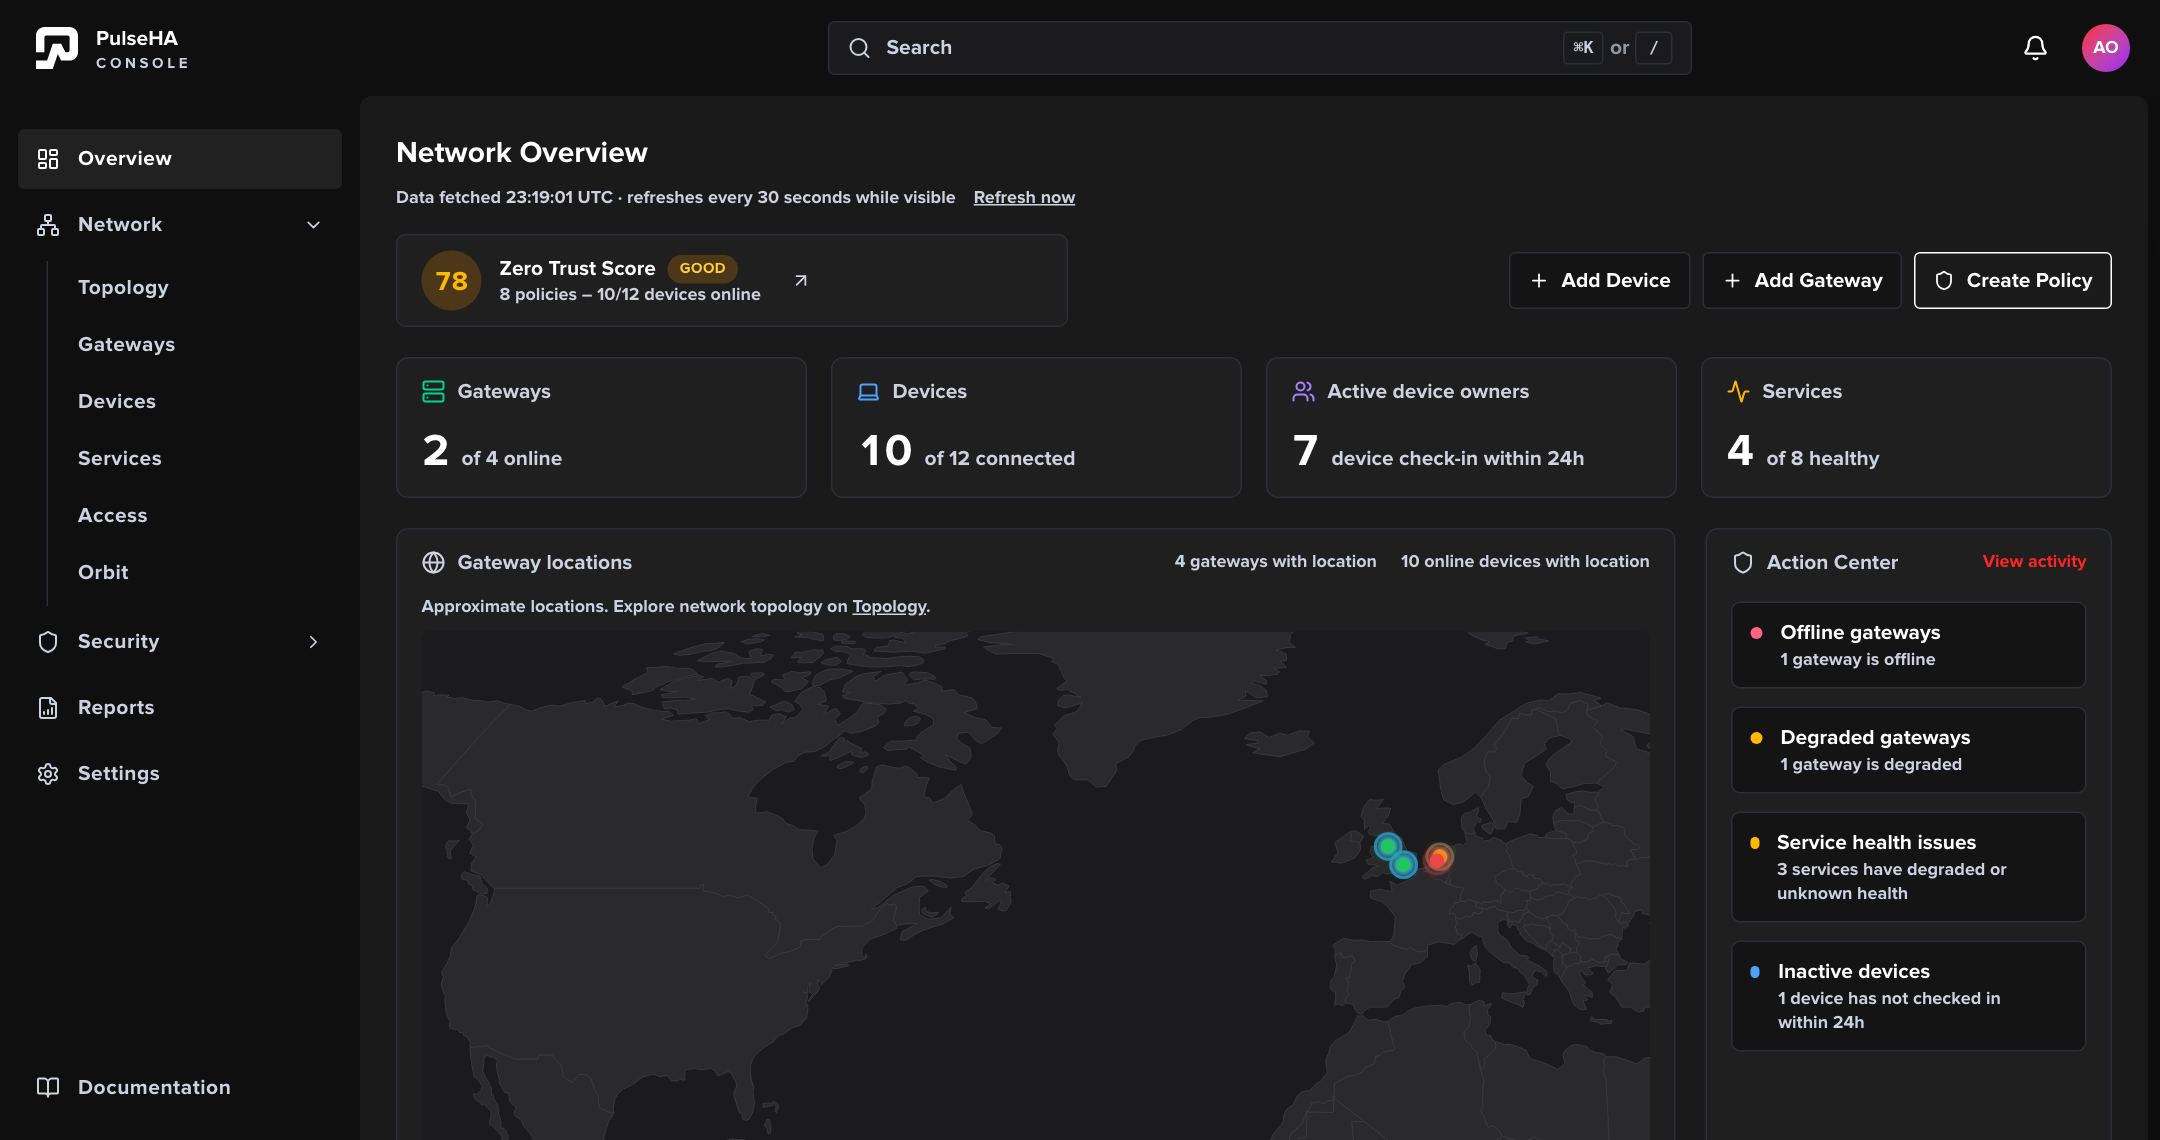
The Overview checklist tracks the same steps as this guide, and the quick actions open each form directly.
1. Enrol a gateway#
- Open Network → Gateways → Add Gateway (or Add Gateway on Overview).
- The page mints a single-use enroll code and shows it inside one command under Install & enroll (one command). Choose Copy.
- Paste the command into a shell on the Linux host. It must run with
sudo. - Leave the Console page open. Under Connect, the panel moves from Waiting for your gateway to check in to Gateway connected once the host reports in.
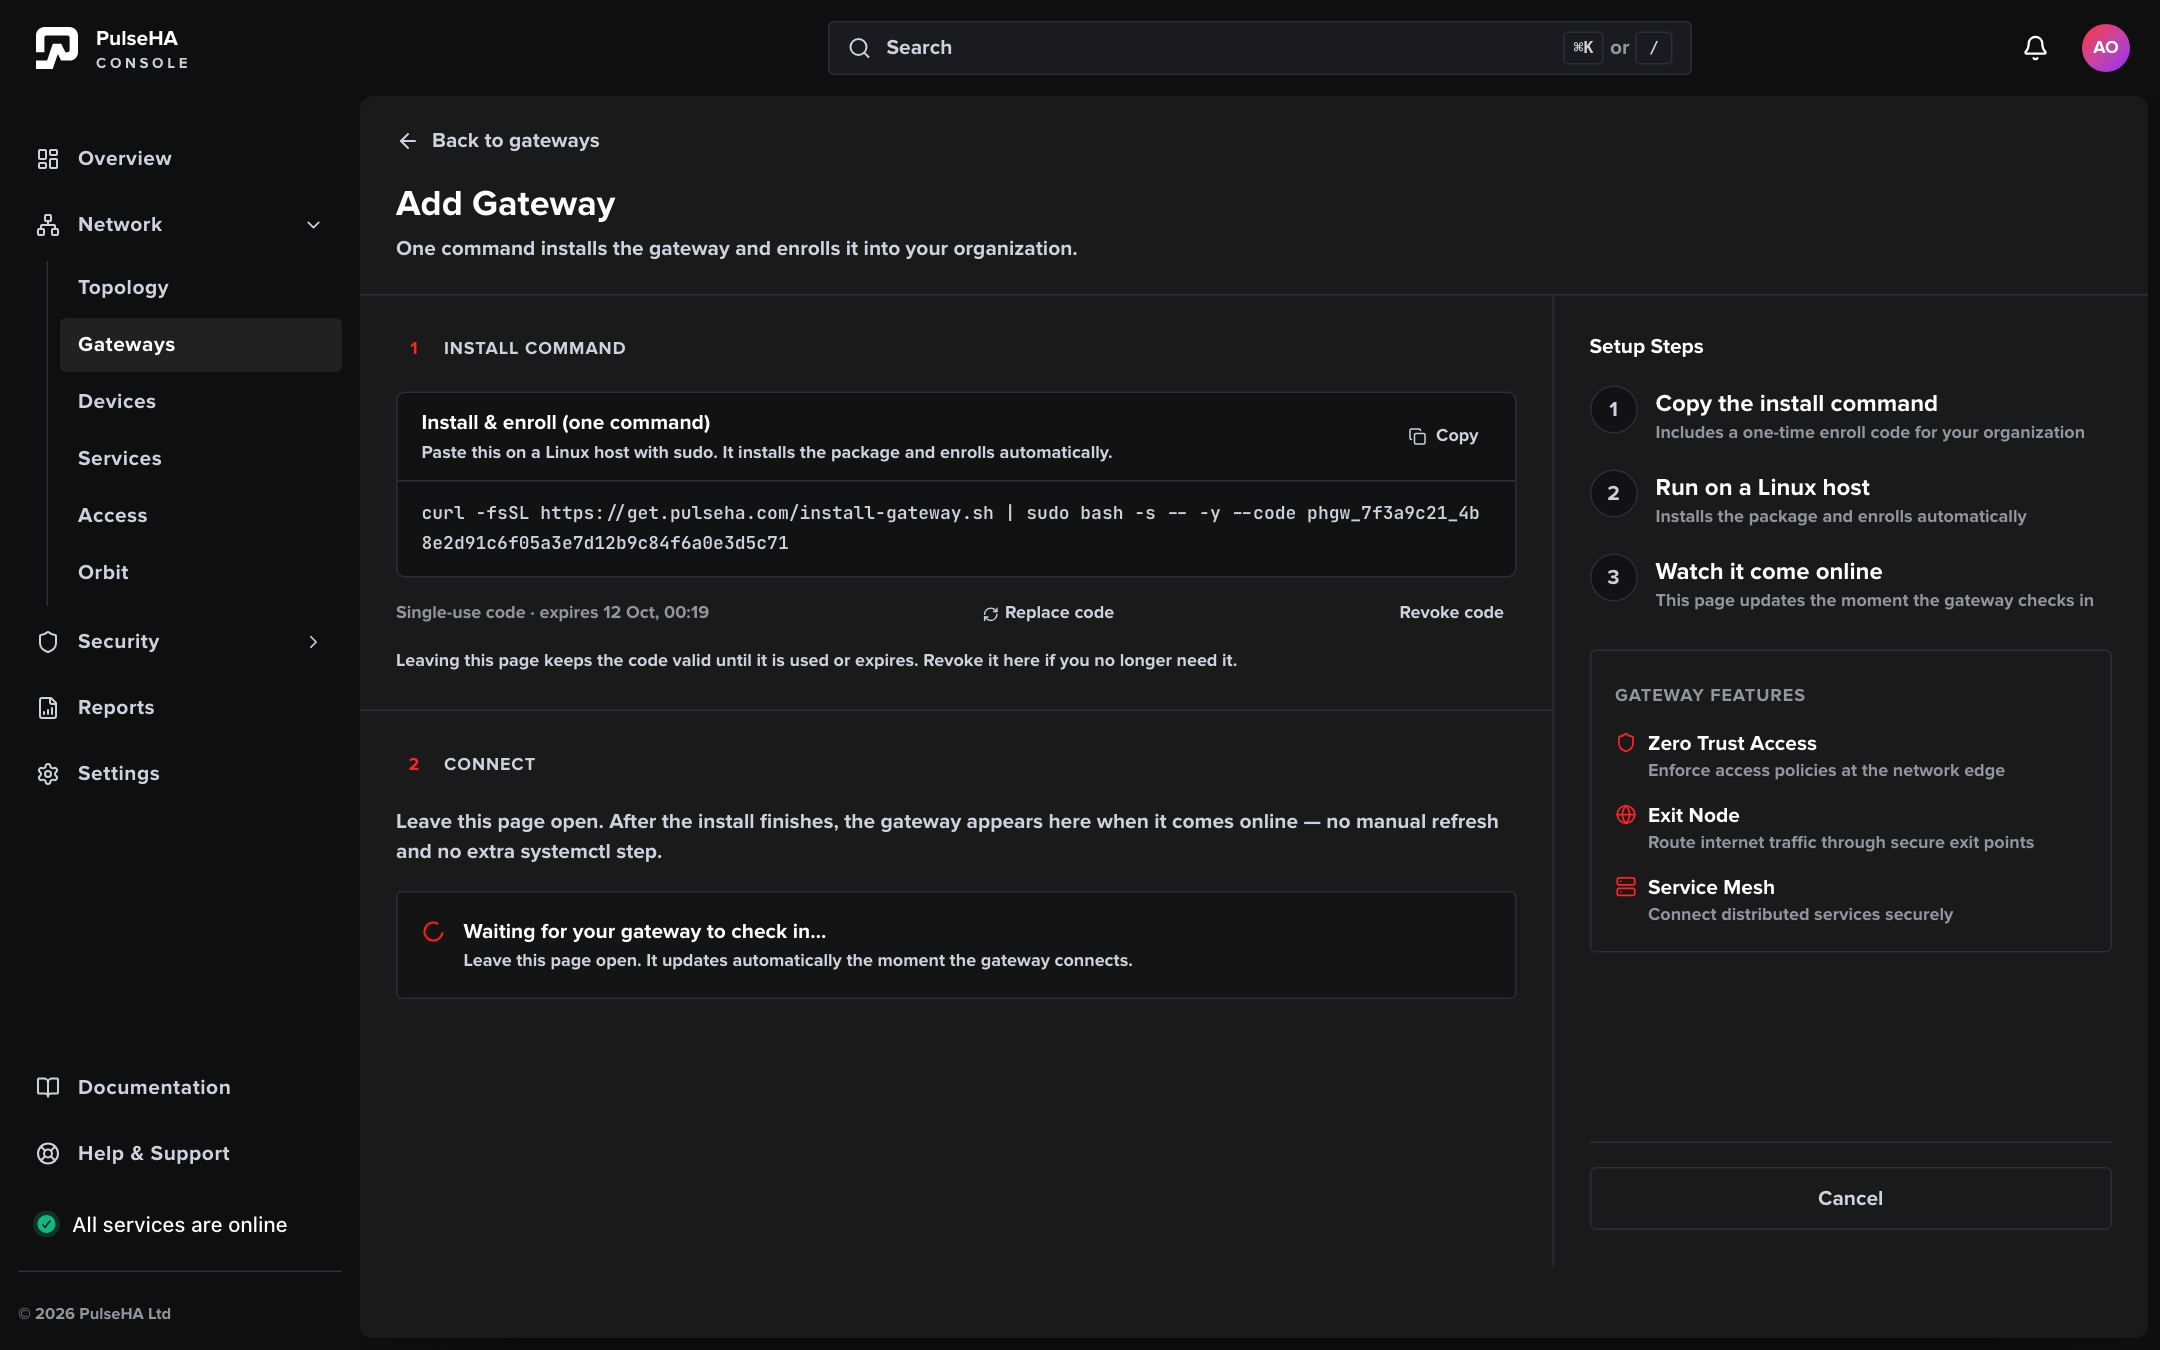
Add Gateway mints a single-use code into one command and then watches for the host to check in.
The gateway then appears in Network → Gateways with status Online. Full detail is in Enroll a gateway.
2. Enrol a device#
- Open Network → Devices → Add Device.
- Under Select Platform, pick Linux, Windows or macOS. Mobile is marked Soon and cannot be selected.
- Install the agent as shown under Install Agent. On Linux this is one command; on Windows and macOS it is a download.
- Authenticate. On Linux run
pulsectl loginand open the printed URL. On Windows and macOS open PulseHA and choose Continue in Browser. - In the browser, sign in and the Console’s Authorize Device page approves the code.
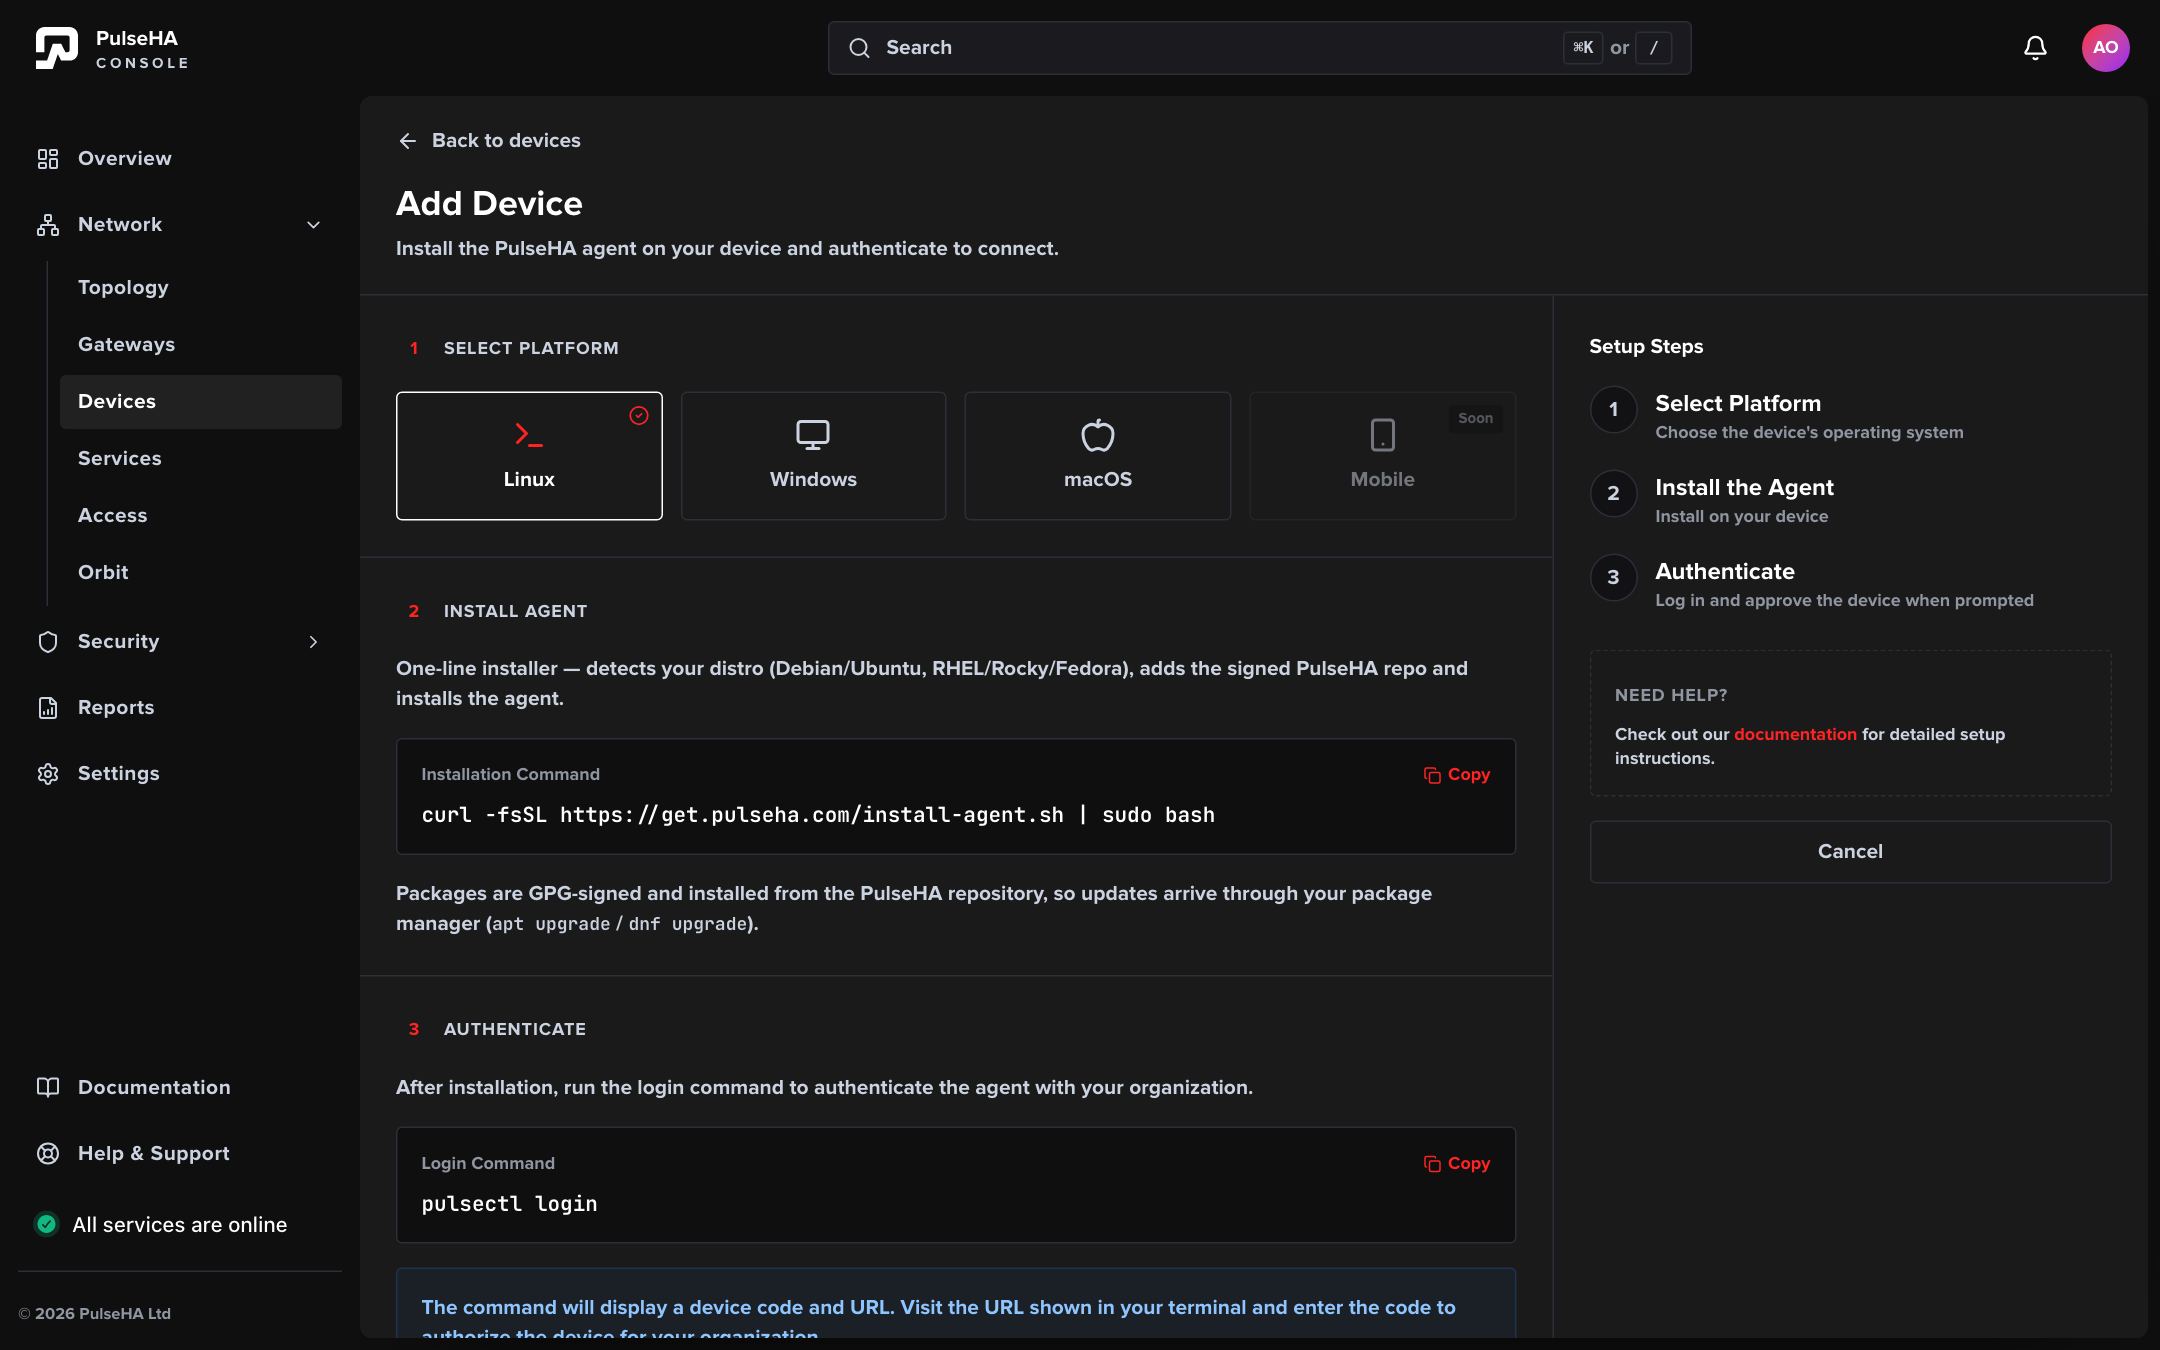
Add Device with Linux selected. The Install Agent and Authenticate sections change with the platform you pick.
The device appears in Network → Devices and moves from Pending to Online once the agent registers. See Install the agent and Authorize a device.
3. Publish a service#
- Open Network → Services and add a service.
- Enter a Service Name.
- Optionally pick an Application Type such as SSH, RDP or Web to fill in the usual protocol, ports and health check.
- Choose an address type: IP / CIDR (an IP address such as
10.0.0.5or a range such as10.0.0.0/24) or Gateway Host (something running on the gateway itself). Hostnames are not supported. - Enter the IP address or CIDR, then Ports (one port, a list such as
22, 80, 443, or a range such as8000-8100; empty means all ports) and Protocol. Gateway Host services support TCP only and take exactly one port. - Under Gateway Assignment, choose the gateway from step 1. Leaving it empty means all gateways.
See Services for health probes and DNS names.
4. Create an access policy#
- Open Network → Access → Add Policy.
- Name the policy and keep the effect on Allow.
- Under Who (Subjects), either tick All subjects or select at least one user, group or device.
- Under What (Resources), select the service from step 3. Either tick All tenant gateways or select the gateway from step 1.
- Leave When (Conditions) empty. Conditional policies cannot be saved yet.
- Choose Create Policy.
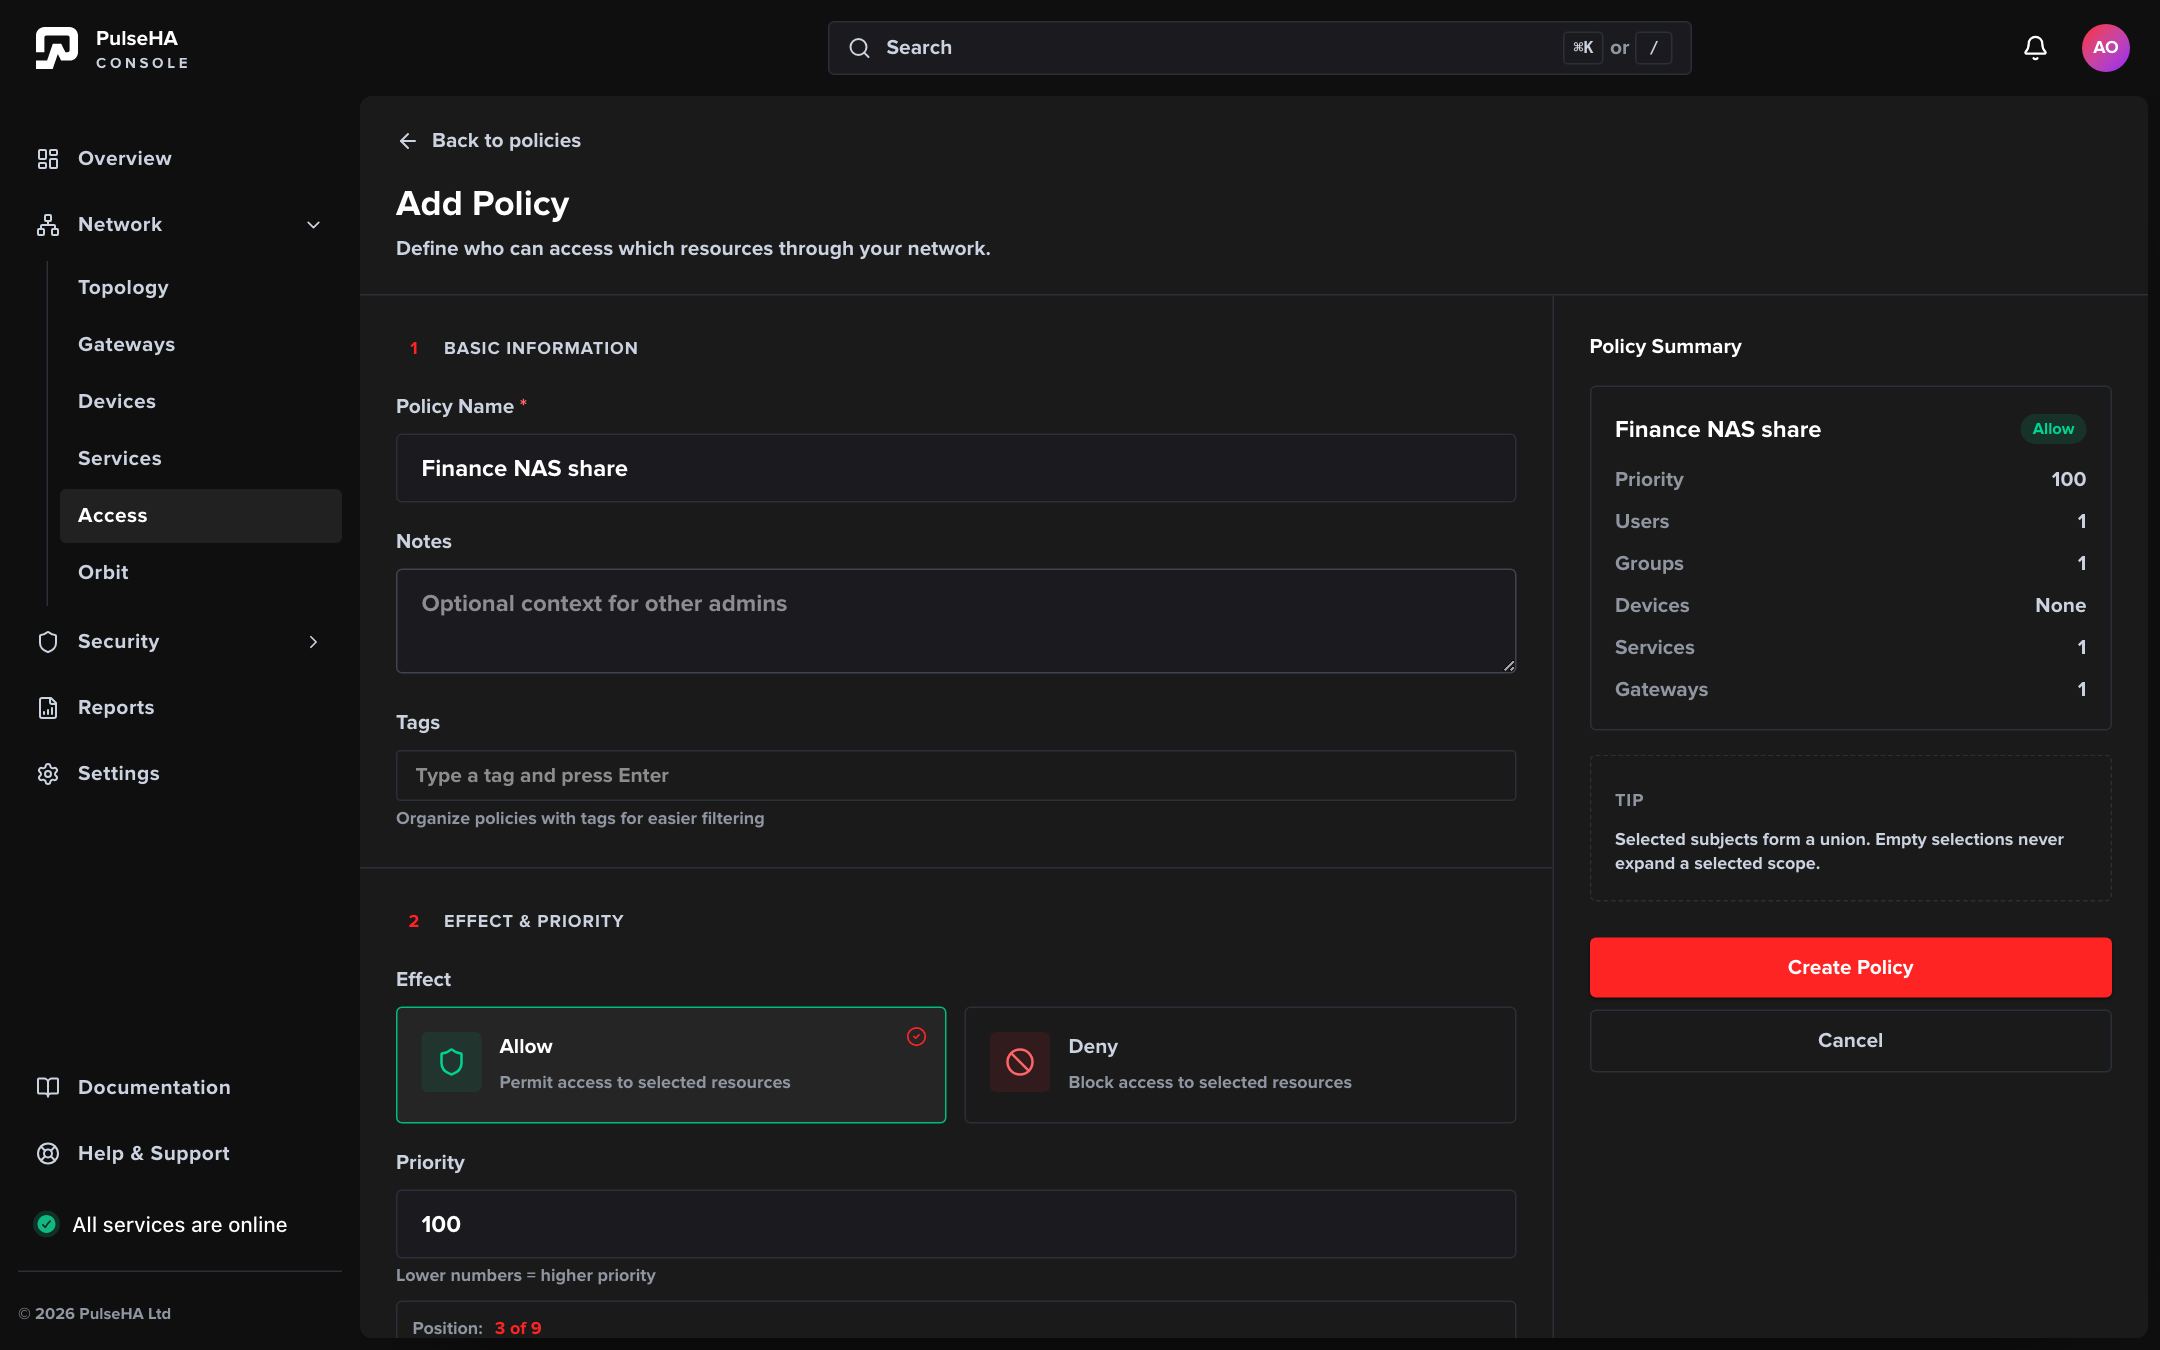
The policy form filled in for a Finance NAS share. The summary card on the right lists who gets what, through which gateway.
The step-by-step version with validation rules is Your first access policy.
5. Test from the device#
The control plane recomputes routes when policy changes and the agent picks them up on its next policy sync. On Linux you can force this with pulsectl refresh, and pulsectl status shows a Policy row with the time of the last sync. Then open the application from the enrolled device.
What you should see#
| Place | Expected state |
|---|---|
| Network → Gateways | Your gateway shows Online |
| Network → Devices | Your device shows Online under Connection |
| Network → Access | One Allow policy listed, filter Enabled |
| The device | The published service answers; unrelated private ranges do not |
If it does not work#
Check in this order:
- Device status. Anything other than Online under Connection means the agent has not registered or has stopped heartbeating. Tunnel down means the agent is alive but reports the tunnel as disconnected: run
pulsectl upon Linux or reconnect from the app. - Policy scope. A policy with Selected subjects and nothing selected matches nobody. A policy with no services is skipped entirely. Open the policy and compare its summary panel with what you expected.
- Gateway scope. If the policy uses selected gateways, the gateway serving the service must be among them.
- Posture. If a posture policy is set to enforce and the device is Non-compliant, its routes are stripped. See Device posture.
- Simulation and audit. Use Policy simulation to see which policy decides for a given user and service, then read Audit for the recorded decisions.