Secure Web
Filter web destinations on traffic routed through PulseHA.
Use Security → Secure Web to block or allow web destinations by category, domain or domain list, for traffic that resolves and routes through PulseHA gateways. It is separate from private DNS service discovery.
Before you start#
- Viewing needs
content_filtering:view. Creating or editing policies, lists, settings and exceptions needscontent_filtering:update(owner and admin by default). Overriding the security baseline needscontent_filtering:baseline_override(owner only by default). - Filtering is DNS-level by default. The page description reads “Control DNS-level web gateway policies for your organization.” HTTP and HTTPS inspection are separate switches in Settings.
- Enter hosts or domains, not URLs. A leading
*.wildcard is the only wildcard allowed. IP addresses are rejected. - Saving publishes a compiled policy to gateways. Saved, compiled and applied state are tracked separately.
Turn on filtering#
- Open Security → Secure Web and click Settings.
- Under DNS filtering, confirm Content filtering is on. Leave Security baseline on; it blocks malware, phishing, command and control, cryptomining and scam domains ahead of every policy.
- Under Bypass prevention, turn on Block DNS-over-HTTPS and Block DNS-over-TLS. Both are off by default. While either is off the page warns that filtering can be bypassed and offers a Block DoH and DoT button.
- Under Unmatched traffic, set Default action for unmatched traffic to Allow or Block.
- To filter by URL path or scan downloads, turn on Inspect web traffic under Web inspection, then choose an HTTPS inspection mode and optionally Malware scanning. Leave Developer tools trust on so the agent also sets up Node.js, Python, curl, git and Firefox to trust inspection; see Developer tools and HTTPS inspection.
Every control saves immediately. You should see “Settings saved” after each change.
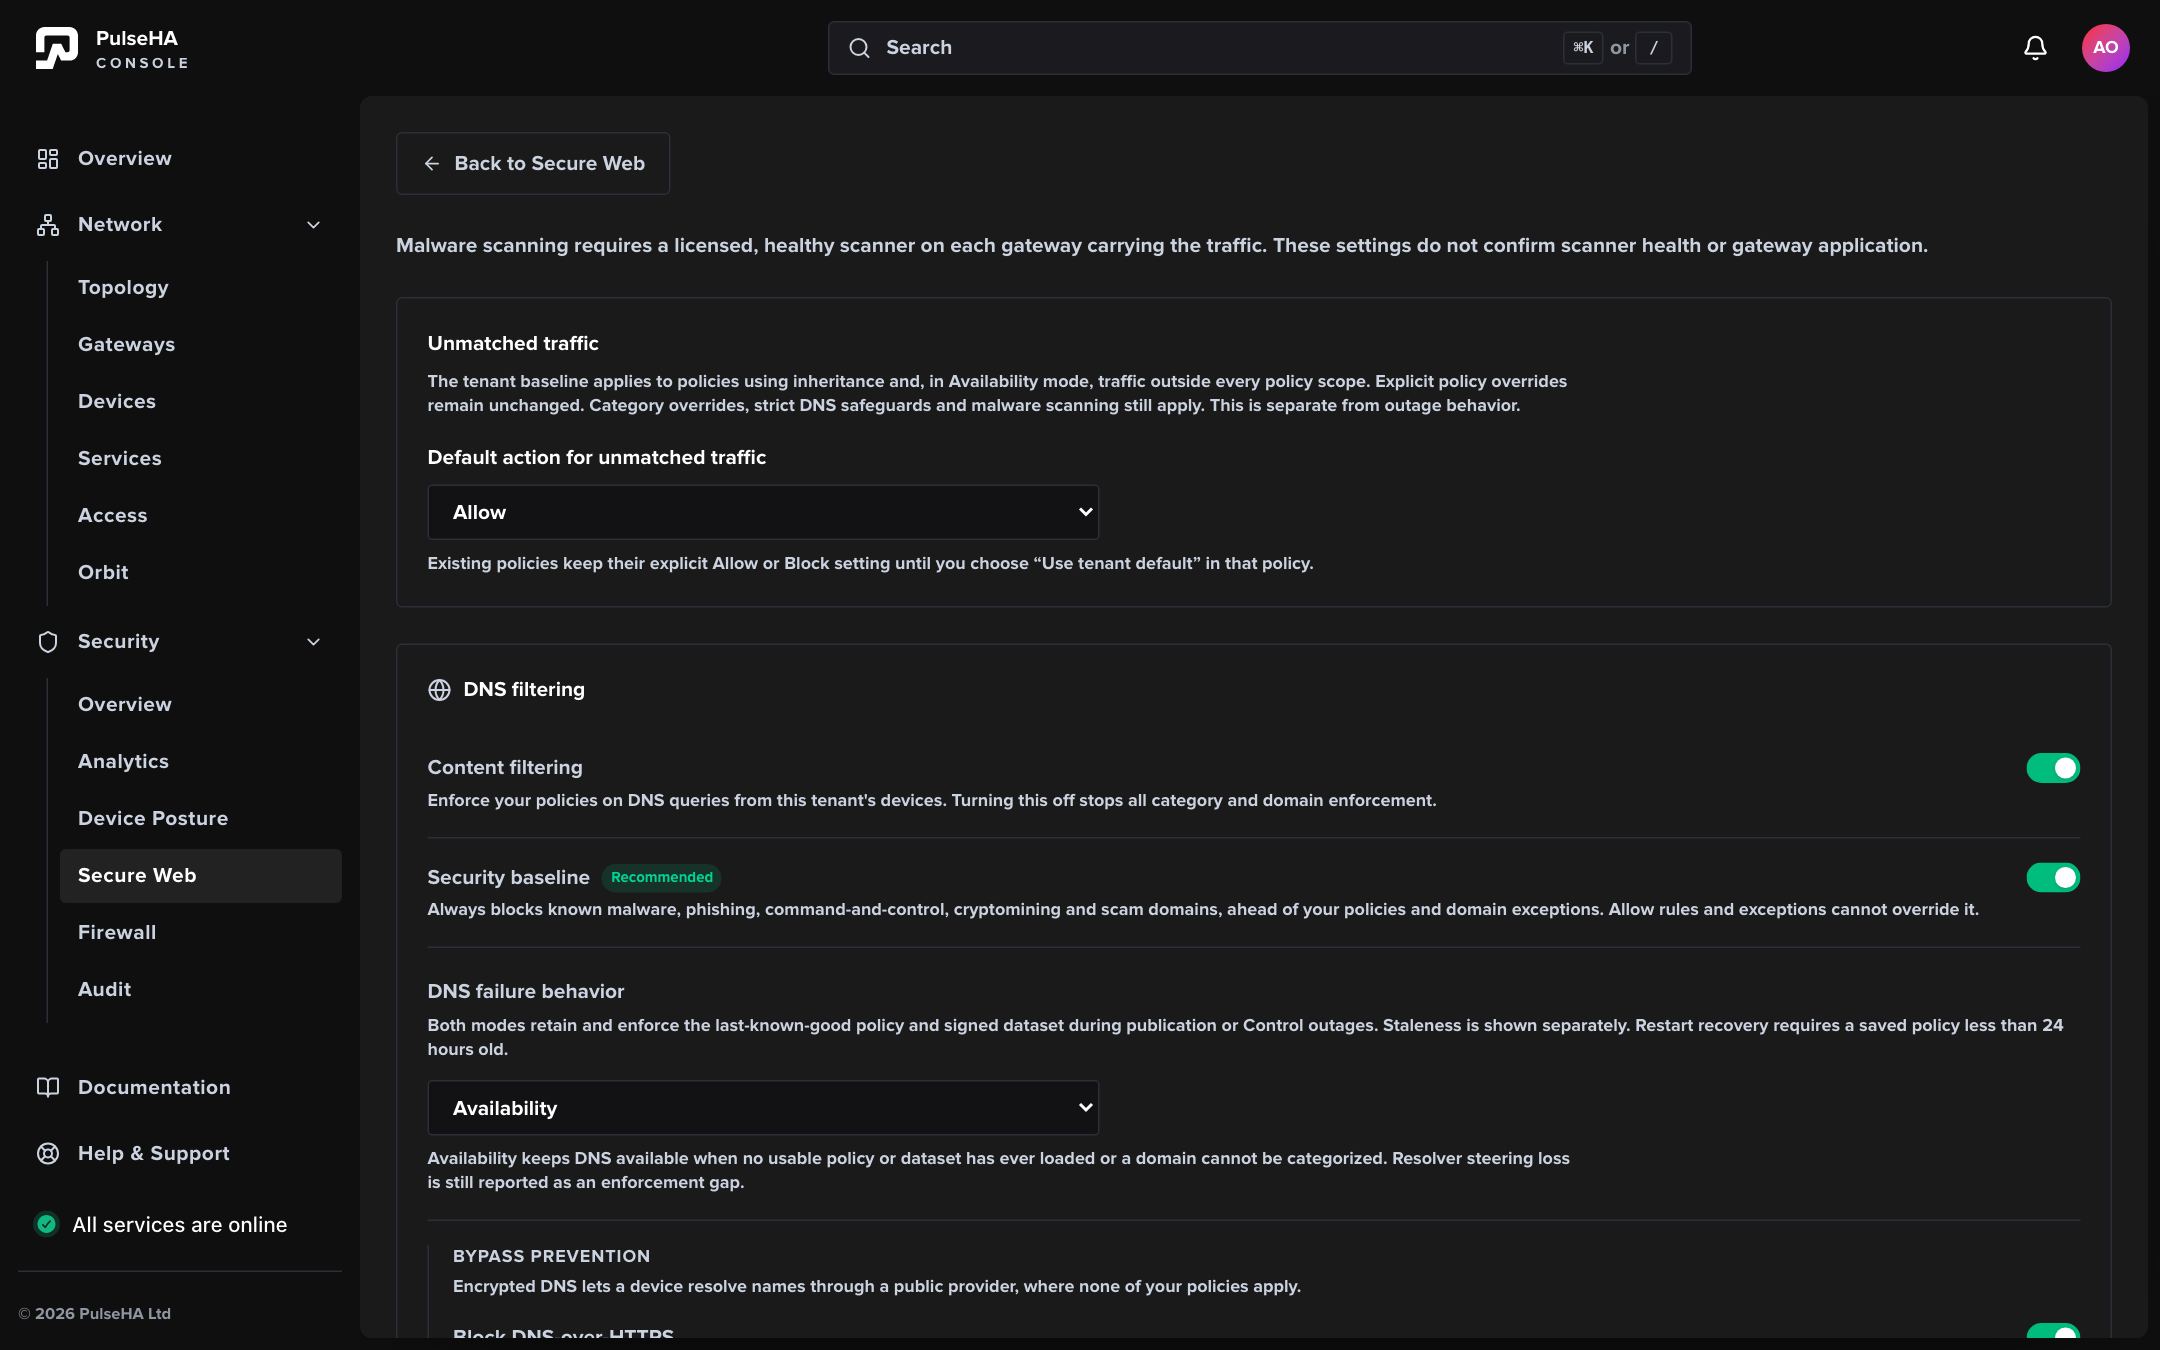
Settings is one long page: the unmatched traffic default at the top, then the DNS filtering switches, failure behaviour and the bypass prevention toggles below.
Create a domain list#
- Open the Domain Lists tab and click New Domain List.
- Choose a type: Deny List, Allow List or Bypass List.
- Enter List Name and add domains one at a time, or paste many into Bulk Import and click Import. The help text allows
*.example.comwildcards and up to 10,000 domains per list. - Save.
The list appears with columns Type, Name, Domains and Updated.
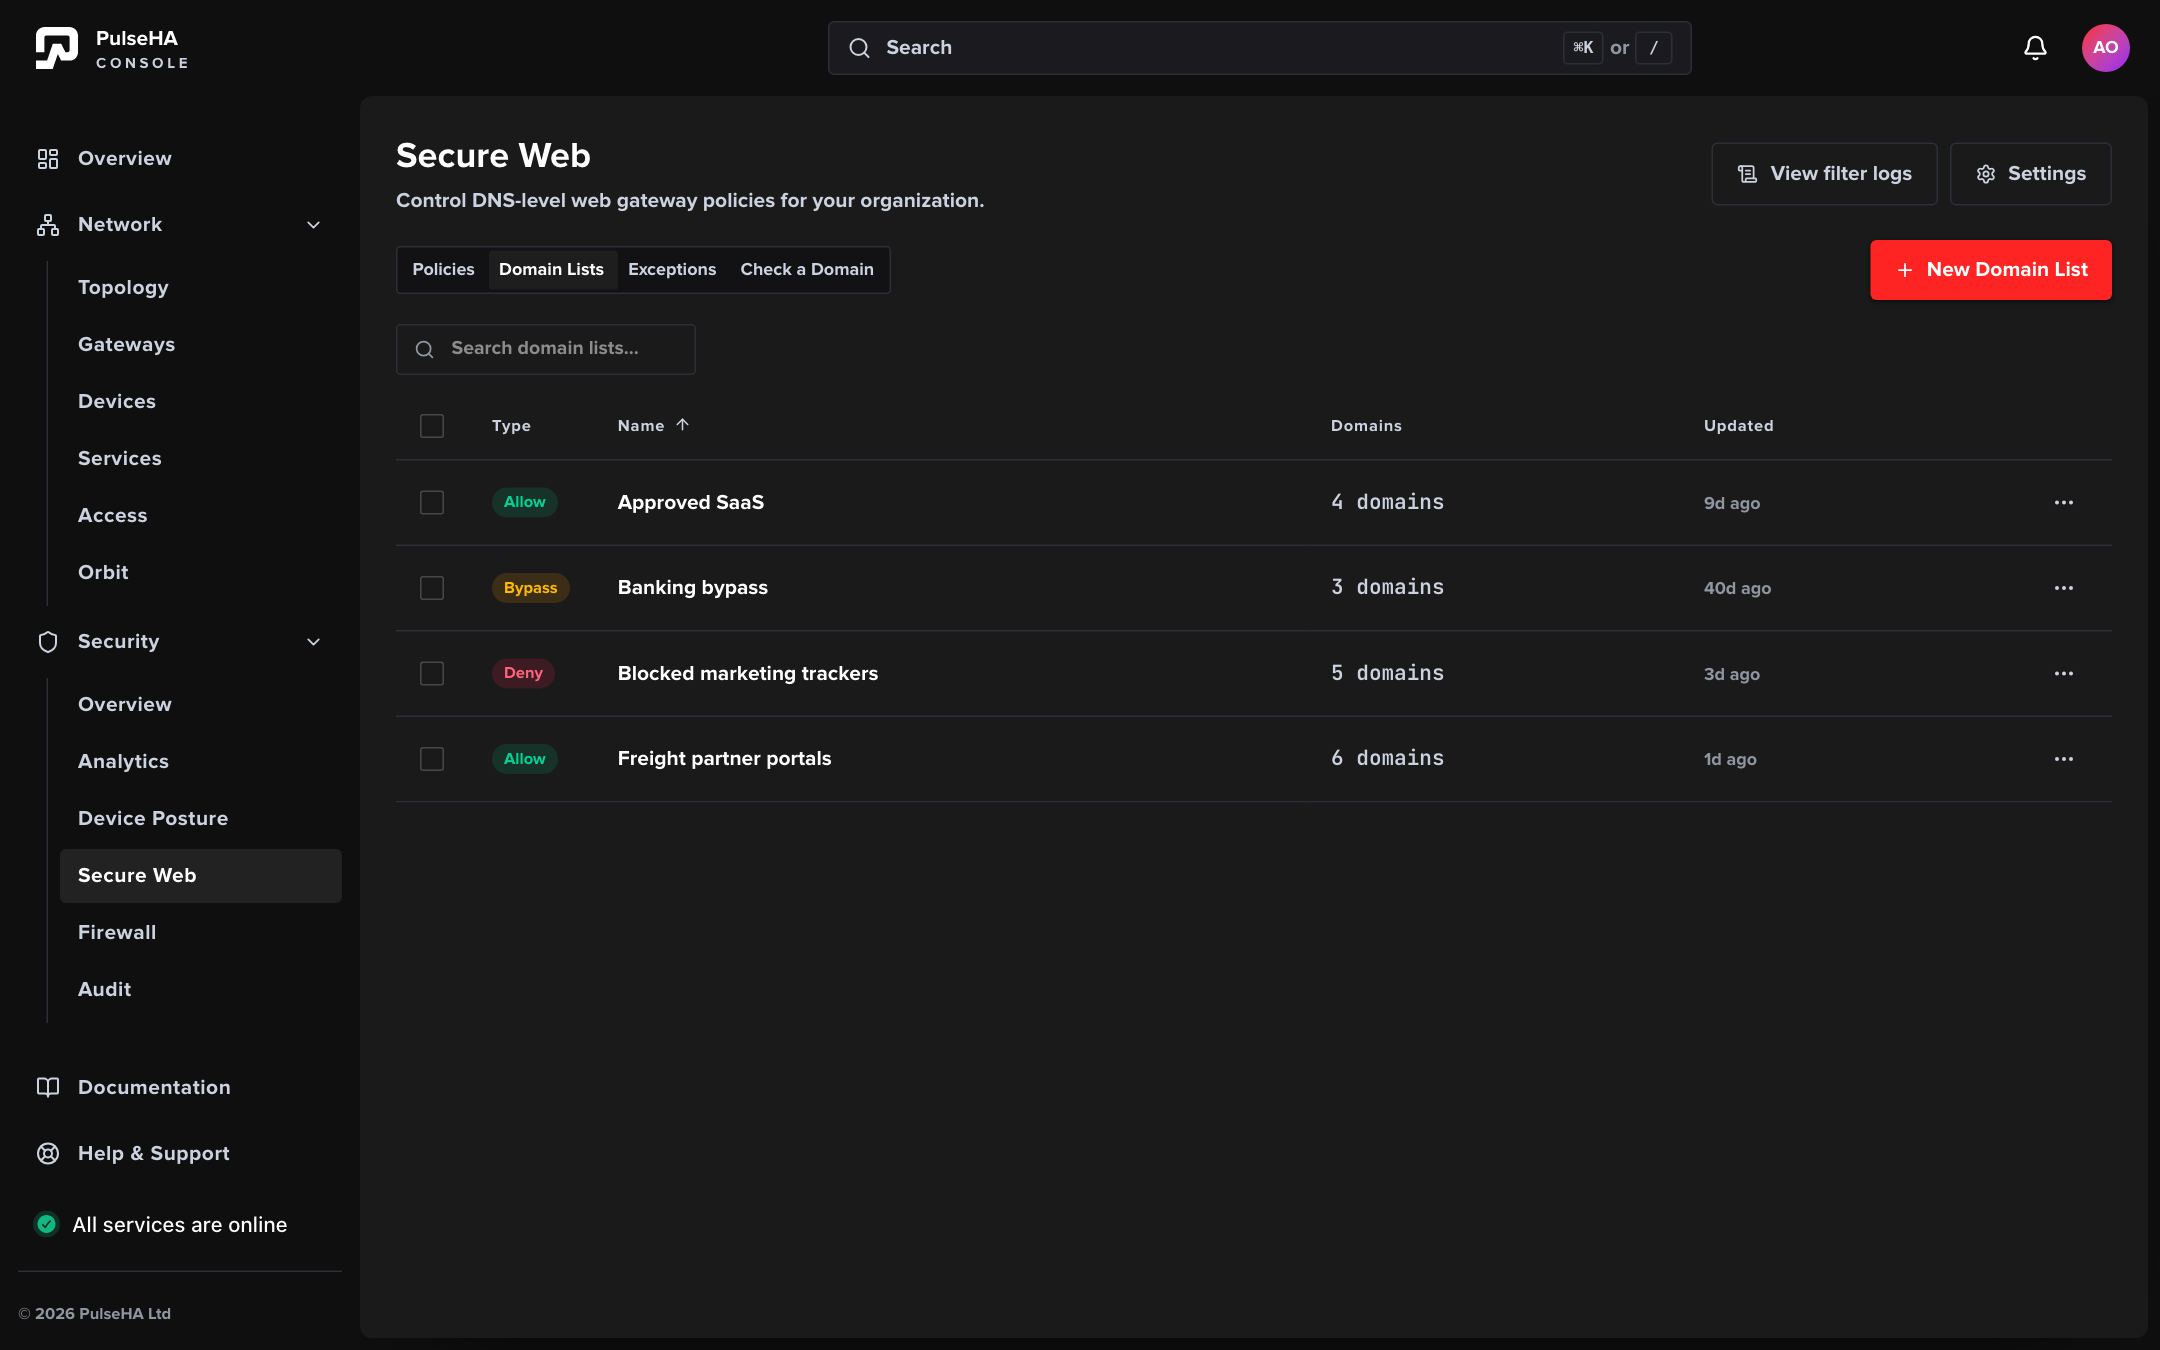
The Domain Lists tab shows each list with its type chip; the same list can be referenced by several policies.
Create a policy#
- Open the Policies tab and click New Policy.
- Enter Policy Name (at least 3 characters).
- Pick a preset: Minimal, Recommended or Strict. New policies start on Recommended.
- In the category matrix, set each category to Not set, Block or Allow. Use Block all, Allow all or Clear all per group. Categories marked “Always blocked by security baseline” cannot be allowed here.
- Under Exceptions, add Custom Domain List, URL Prefix or Application rules with Block or Allow. An Application rule covers every host a named application uses (for example Apple App Store or Microsoft Teams), as maintained by PulseHA. Exceptions are evaluated before category rules.
- Under Advanced options, choose what happens to unmatched traffic: Use tenant default, Allow or Block.
- Leave Enabled on and click Create Policy.
Drag rows in the Policies table to change evaluation order. The hint reads “Drag rows to change evaluation order”.
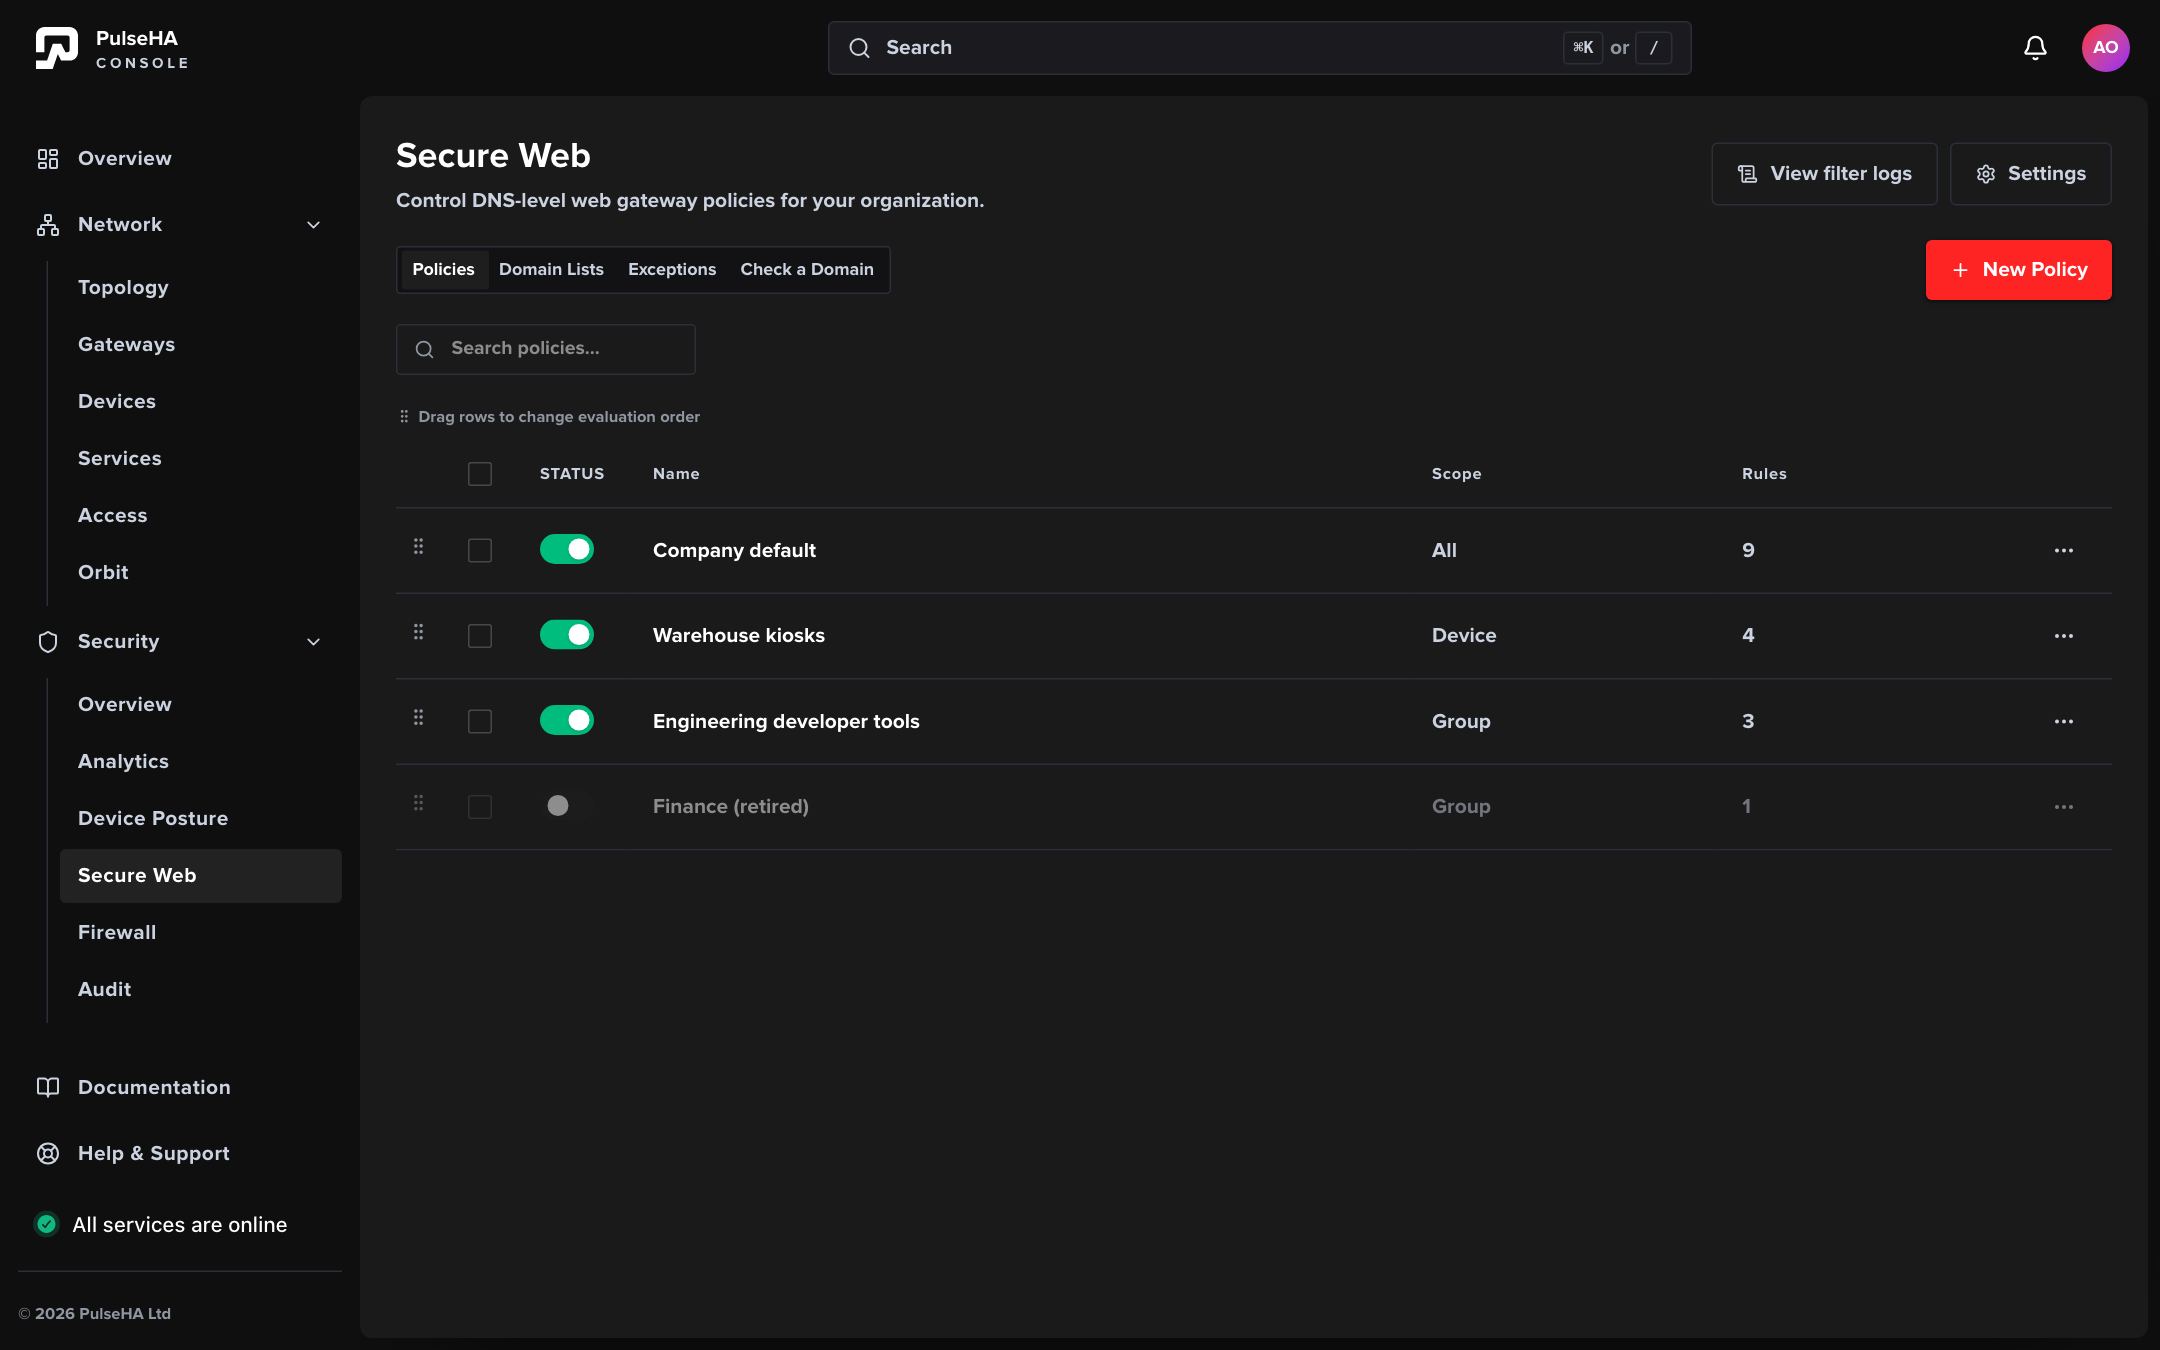
Policies are listed in evaluation order with a status toggle, scope and rule count; drag the handle on the left to move a policy up or down.
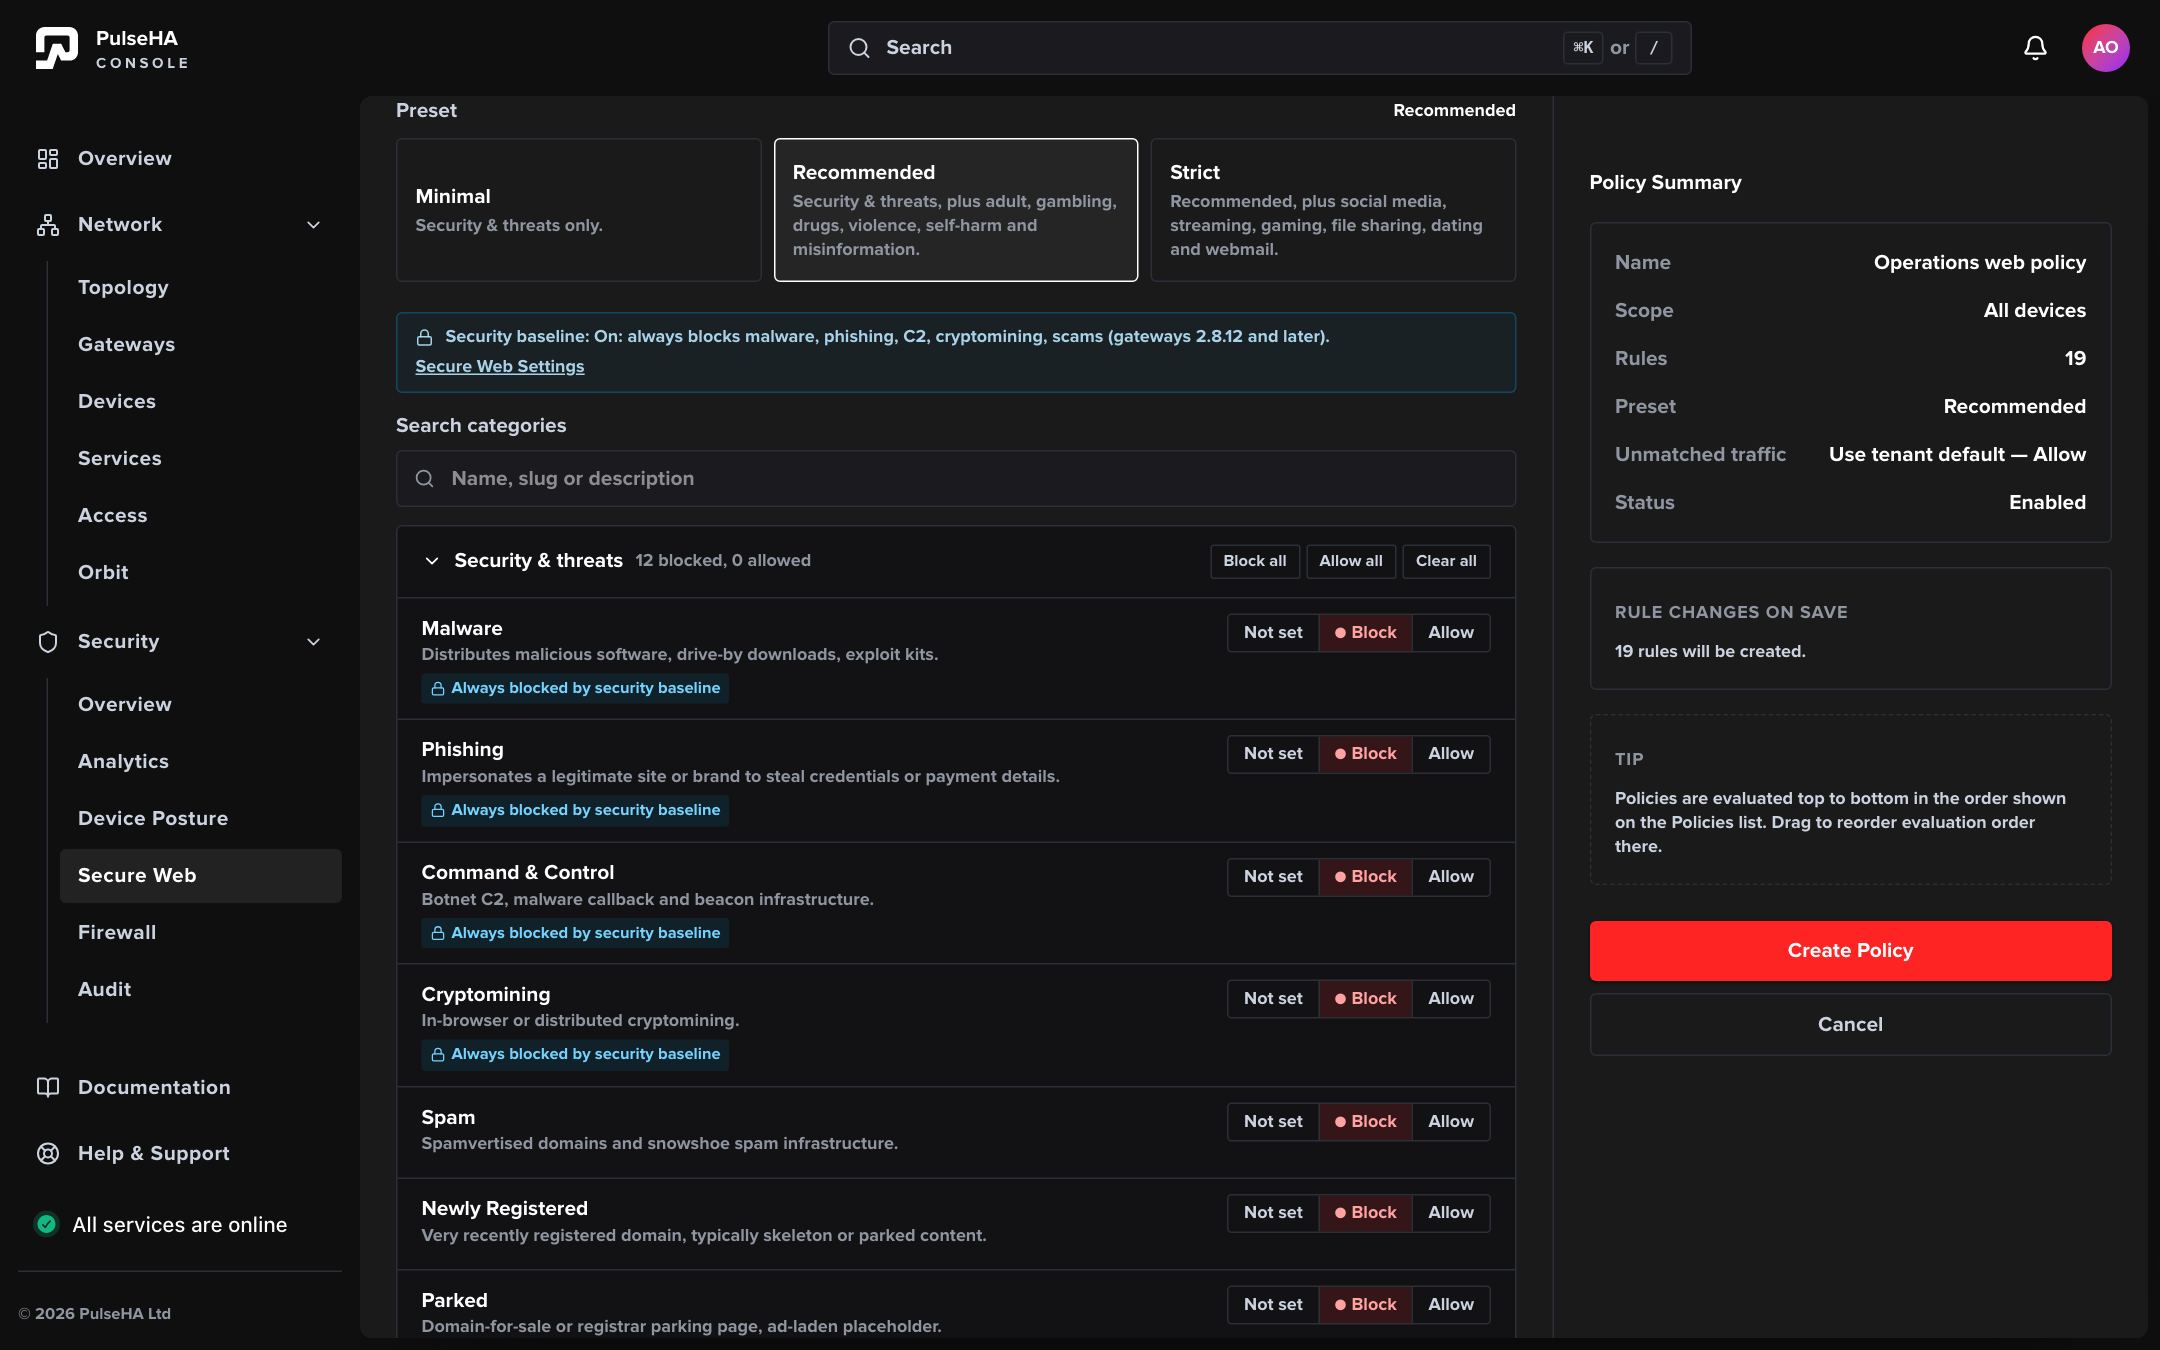
The category matrix after picking Recommended: baseline categories show Always blocked and cannot be allowed, and the Policy Summary counts the rules that will be created.
Add a tenant exception#
Use the Exceptions tab for a time-boxed override without editing a policy.
- Click New Exception.
- Enter the domain, choose Allow or Deny, and a match scope of Exact host or This host and subdomains.
- Enter a Reason (at least 3 characters). Tick Never expires or set Expires (UTC). The control plane rejects expiries more than 90 days away.
- Save. You should see “Tenant exception saved; gateway application may still be pending”.
An allow exception cannot override a protected security verdict. Baseline overrides are created from a blocked event in Audit and must expire within 7 days.
Check how a domain is categorised#
Use the Check a Domain tab to see what PulseHA thinks a name is before you write a rule or raise a support case.
- Enter a host, for example
amp-api.apps.apple.com, and click Check. - The result shows the categories, Decided by when a parent entry that covers its subdomains decided the category, Application when the name belongs to a recognised application, and Dataset (the dataset version carrying the verdict). A note appears when the verdict is newer than the dataset gateways have; they receive it with the next update.
- If the catalogue does not cover the name yet, PulseHA categorises it when you check, which can take up to 20 seconds. The new categorisation is available on gateways with the next dataset update. A category marked Proposed, awaiting review is not on gateways until a reviewer approves it.
- “No catalogue entry covers this name” means the name is still unknown: allowed under the default policy, blocked in strict mode. Check again later.
- If the category is wrong, click Report incorrect category, choose what It should be, explain Why and click Submit report. This opens a shared review, and an approved fix reaches every tenant with the next dataset update. Platform hosts (app stores, operating system updates, collaboration and identity services) are reviewed within one business day; other reports within three. For an immediate tenant-only override, add an Exception instead.
Reference#
How categories are decided#
Every name resolves to the most specific catalogue entry: an exact match beats a parent entry that covers subdomains. When more than one source describes the same name, the most trusted source wins.
| Source | What it is |
|---|---|
| Reviewed correction | A category approved through a report or support case. Always wins. |
| Applications catalogue | A named application and the hosts it uses, approved by a PulseHA reviewer. |
| Curated list | Threat intelligence and security lists. These back the security categories. |
| Classifier | PulseHA’s own classification of the name from its page, certificate, registration record and parent domain. |
Topical third-party lists (games, shopping, news and similar) are hints to the classifier, never a verdict on their own, so an app store is not “gaming” because a list says so. PulseHA re-examines the most used list-backed names every day and opens a review when its own classification disagrees.
Newly Seen is a 30-day marker, not a classification. A name PulseHA resolvers have not seen before, with no verdict yet, carries it until it is categorised or 30 days pass. No preset blocks it; add it to a policy if you want to hold back brand-new names.
Evaluation order#
- Bypass list domains skip web proxy filtering entirely. DNS filtering still applies.
- The security baseline blocks its categories on gateways 2.8.12 and later.
- Enabled policies are evaluated in table order. The first policy whose scope matches is used; later policies are not evaluated.
- Inside that policy, rules run in stored order and the first match wins. Exceptions run before category rules.
- If nothing matches, the policy’s unmatched-traffic action applies, or the tenant default when set to Use tenant default.
Domain list types#
| Type | Effect |
|---|---|
| Deny List | Block matching domains |
| Allow List | Allow matching domains through |
| Bypass List | Skip web filtering for matching domains |
Malware scanning#
With Malware scanning on, downloads on inspected traffic, over HTTP and decrypted HTTPS, are checked for malware by PulseHA’s malware scanning engine before any byte reaches the device. The check runs on the gateway already carrying the traffic, in an isolated process with no network access: files never leave that gateway, and nothing is kept once the check finishes. PulseHA records each file’s SHA-256 hash, the verdict and any threat name. The engine’s supplier receives nothing from your gateways. Downloads routed through Orbit locations are not scanned yet.
| Setting | Effect |
|---|---|
| If a file cannot be checked | Applies when a file cannot be fully checked: the scanner is unavailable, busy or still loading definitions, the check times out, or the file is corrupt, nested too deeply, a partial download, uses unsupported compression, or is larger than the gateway can hold under a limit you chose. Allow the download (fail open), the default, lets the file through and logs the reason it was not checked. Block the download (fail closed) shows the PulseHA block page with the reason; it also stops resumed or segmented downloads, which some download managers and update tools use. |
| Encrypted or password-protected archives | PulseHA’s malware scanning engine cannot look inside an archive that needs a password, so it cannot say whether the files in it are safe. Allow the download, the default, lets the archive through and logs it as encrypted. Block the download shows the PulseHA block page saying the file is password-protected or encrypted. |
| Maximum file size to scan (MB) | Files up to this size are checked. If your organisation has not chosen a size, PulseHA’s default limit applies, and the help text under the field states it. Each gateway can hold a file up to half of its scan memory, which is at most 256 MB, so the field shows “Your gateways can scan files up to N MiB” and will not save a larger value. A change through the API above that limit is refused with the same message. Large files reach the user only once they have downloaded fully and been checked. |
| Files over the size limit | Allow the download, the default, lets files larger than the limit through unscanned and logs them as too large to scan. Block the download shows the PulseHA block page saying the file is too large to scan. |
If you have not chosen a limit, each gateway uses PulseHA’s default limit or the most it can hold, whichever is smaller, and anything larger follows Files over the size limit. If you chose a limit and a gateway can no longer hold files that large, files between the two follow If a file cannot be checked on that gateway. The page warns when your saved limit is above what your gateways can hold.
Nothing changes for your organisation until you change a setting. If you had chosen Block the download for files that cannot be checked before these choices were separate, encrypted archives start on Block too, because they were already blocked; files over the size limit start on Allow, because they always passed.
Older gateway releases. Gateways on releases from before these choices keep their previous behaviour: if you have not chosen a limit they use a 25 MB default, they treat encrypted archives as files that cannot be checked, and they always allow files over the size limit. When you choose Block for files over the size limit or for encrypted archives and some gateways cannot enforce it, the page warns you before saving and says how many gateways are affected. Update those gateways from Gateways.
Blocked downloads are logged in Audit with the threat name and the file’s SHA-256 hash. Downloads that pass or are blocked without a scan are logged there too, under Content Filter with Event Class set to Malware, with the reason in words, the file name, host, size and gateway:
- Each block is logged as its own row, always.
- Unscanned downloads that are allowed are logged one row each, up to a rate per site (by default 10 a minute for each reason and site, and 600 a minute per gateway). Beyond that rate PulseHA counts them instead: one row marked with the number of similar downloads, so every download is still counted.
- HTTPS that is not decrypted cannot be scanned: a host on a never-decrypt list or in a compatibility bundle, a host that selective inspection does not decrypt, or HTTPS inspection turned off. It is logged as hourly totals per device, with the host, or the number of hosts and the busiest one.
- Files that are scanned and found clean are not logged here. Downloads from devices that do not send HTTPS through PulseHA never reach the gateway and are not seen; Managed HTTPS trust readiness on the Settings page shows which devices are ready.
Gateway scanning coverage#
Settings are the same for every gateway, but downloads are only checked on gateways that run PulseHA malware scanning, so Block the download applies where a gateway can scan. Gateways that cannot scan let downloads through until they can. Allow the download stays the default for files that cannot be checked until you choose Block. Gateway scanning coverage, under Malware protection on the Settings page, shows how many gateways scan (for example 2 of 5 scanning) and lists each gateway:
| Status | Meaning |
|---|---|
| Scanning | The gateway checks downloads. With Block chosen, it blocks files it cannot check. |
| Not scanning | The gateway cannot check downloads. Downloads through it pass unchecked, whichever option is chosen for files that cannot be checked. The exception is an Offline gateway: it keeps the settings it last received, Block included, until it reconnects. The reason is shown next to it, with a How to fix link to the matching section below: not installed, unsupported platform, offline or version too old. |
| Checking | The gateway is starting PulseHA malware scanning, or its scanner is briefly unavailable while it still holds recent definitions. It applies your settings as they are: with Allow, downloads pass; with Block, every download through it is blocked until it shows Scanning. While Block is chosen, the warning names these gateways. |
While malware scanning is on and any gateway is Not scanning, the panel shows a warning such as “Scanning on 2 of 5 gateways. On bri-gw-01 and rot-gw-01, downloads pass unchecked. ams-gw-01 is offline and keeps the settings it last received until it reconnects.” The warning goes once every gateway scans. If your role cannot view gateways, the panel shows the counts without gateway names.
Confirming a coverage gap. When you turn on Malware scanning, or choose Block the download while scanning is on, the page first checks coverage again. If any gateway cannot scan, it asks you to confirm and names those gateways. Cancel changes nothing. Confirming saves the setting: gateways that can scan apply it straight away, and the others start scanning on their own once they can, with no further change needed. Each confirmed save is recorded in Audit with who made it, which gateways could not scan and why. If coverage cannot be checked at that moment, the page still asks you to confirm, with a general warning. Gateways that are only Checking trigger the question when the result would be scanning on with Block, because they block every download until they finish starting; with Allow they do not. Turning scanning off, or choosing Allow, never asks.
Changes made through the API apply the same way, without the confirmation step, and are recorded in Audit the same way.
Scan: not installed#
The gateway’s package was installed without PulseHA malware scanning. Reinstall it with the current release package for Linux amd64, which includes malware scanning; see Gateways. The gateway reports its new state at its next check-in. The gateway moves to Checking while it loads definitions, then to Scanning.
Scan: unsupported platform#
PulseHA malware scanning runs on Linux amd64 (64-bit x86) gateways only. A gateway on arm64 or another platform keeps enforcing URL rules and every other Secure Web setting, but cannot check downloads. To scan downloads at that site, run its gateway on a Linux amd64 host; see Gateways.
Scan: offline#
The gateway has not checked in recently. It keeps applying the settings it last received until it reconnects, so a change you save now reaches it only then. Check the gateway’s network connection and service status in Gateways. Once it reconnects, it reports its scanning state again.
Scan: version too old#
The gateway runs a release without PulseHA malware scanning. When the panel names a version, update to at least that version; otherwise update to the latest release. Update the gateway from Gateways. After the update it moves to Checking and then to Scanning, with no change needed on this page.
Gateway applied-policy states#
The enforcement panel Fleet DNS enforcement shows each gateway as Applied, Previous policy, Policy differs, Apply failed, Not reported, Not reporting or Offline. A report older than five minutes is not evidence of current enforcement.
Troubleshooting#
- “Saved, but policy compilation failed: … Gateways may still enforce the previous ruleset.” The save stored your change but the compiler rejected it. Fix the detail named and save again.
- “Settings saved, but publication failed…” The setting is stored but gateways did not receive it. Check gateway connectivity and the enforcement panel.
- “Secure Web could not be loaded”. Reload before making changes. The forbidden variant, “Secure Web access unavailable”, means your account lacks
content_filtering:view. - “This policy changed since you opened it. Reload before saving.” Someone else saved the policy. Reload to avoid overwriting their change.
- “domain list is referenced by N rule(s); remove those rules first”. Remove the list from policies before deleting it.
- A download got through although Block is chosen. Open the download’s row in Audit: the reason says which choice applied. Files over the size limit and encrypted archives follow their own choices, not the choice for files that cannot be checked. Then check Gateway scanning coverage: Block applies only on gateways that show Scanning, and gateways on older releases do not enforce Block for files over the size limit or encrypted archives. Follow the How to fix link next to the gateway that carried the download.
- “Your gateways can scan files up to N MiB. Choose N MiB or less.” The size you entered is larger than at least one scanning gateway can hold. Choose that size or less, or give the gateway more memory.
- Every download through one gateway is blocked. If that gateway shows Checking and Block the download is chosen, it blocks every file it cannot check until it shows Scanning. Wait for it to finish starting, or choose Allow the download in the meantime.
- Users still reach blocked sites. Check Block DNS-over-HTTPS and Block DNS-over-TLS are on, and check the gateway shows Applied in the enforcement panel.
- Developer tools fail with certificate errors while browsers work. Tools such as npm, pip,
azand git keep their own certificate list. Runpulsectl doctoron the device and check Inspection compatibility on the Settings page. See Developer tools and HTTPS inspection. - Path-based URL prefix rules do not match. Path matching needs HTTP or inspected HTTPS. Uninspected HTTPS matches by host only.
- A domain has the wrong category. Open Check a Domain to see which entry decided, then Report incorrect category. An approved fix reaches gateways with the next dataset update; use an Exception for an immediate tenant-only override.
Related tasks#
- Developer tools and HTTPS inspection to keep npm, pip, git and other tools working under inspection.
- Audit to review decisions under the Content Filter category.
- Analytics for Secure Web block trends.
- DNS for names assigned to private services.
- Exit nodes to route internet traffic through a gateway.
- Gateways to check gateway versions.