Using the Console
Navigate current Network, Security, Reports, and Settings workflows.
The console at console.pulseha.com is where you configure a tenant and watch it run. It has one side menu, one landing page, one search box and a consistent vocabulary for status. This page walks through each so you know where to look and how to read what you see.
The side menu#
The menu has five top-level entries. Network and Security are collapsible groups; Network starts open and Security starts closed, and the console remembers your choice.
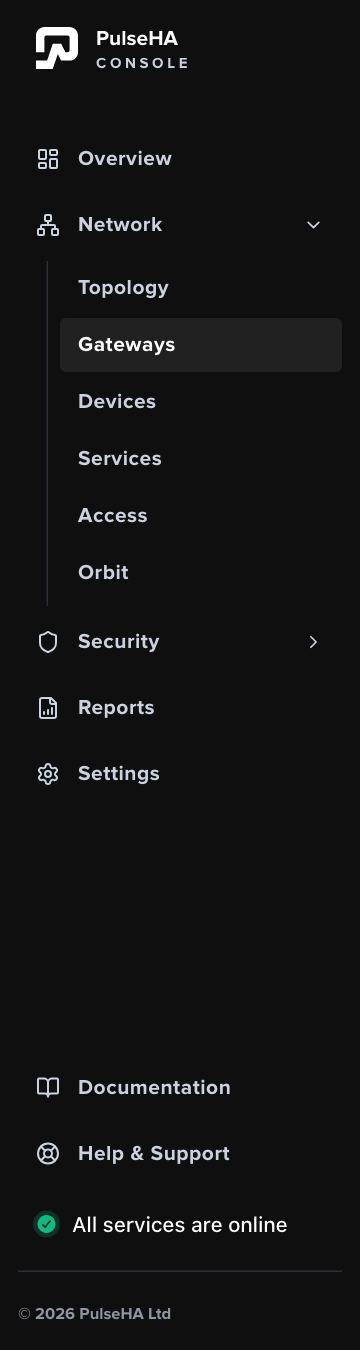
The side menu with Network open and Security collapsed. Gateways is the current page; Documentation, Help & Support and the service status badge sit at the bottom.
| Entry | Pages | Needs |
|---|---|---|
| Overview | Network Overview | nothing |
| Network | Topology, Gateways, Devices, Services, Access, Orbit | gateways:view, devices:view, services:view, policies:view as appropriate; Topology is ungated |
| Security | Overview, Analytics, Device Posture, Secure Web, Firewall, Audit | audit:view, policies:view, content_filtering:view, firewall:view as appropriate |
| Reports | Reports | any one view permission |
| Settings | opens a submenu | varies by page |
Items you lack permission for are hidden, and a group with nothing visible disappears. The same permissions are enforced on the server, so a bookmarked URL you cannot see also returns a permission error.
Settings replaces the menu with a submenu in three sections: Preferences (Profile, Appearance, Notifications), Security (Security, Authentication) and Administration (General, Domains, DNS, Users, RBAC, Plan & usage, About). A back link at the top returns you to Network or Security.
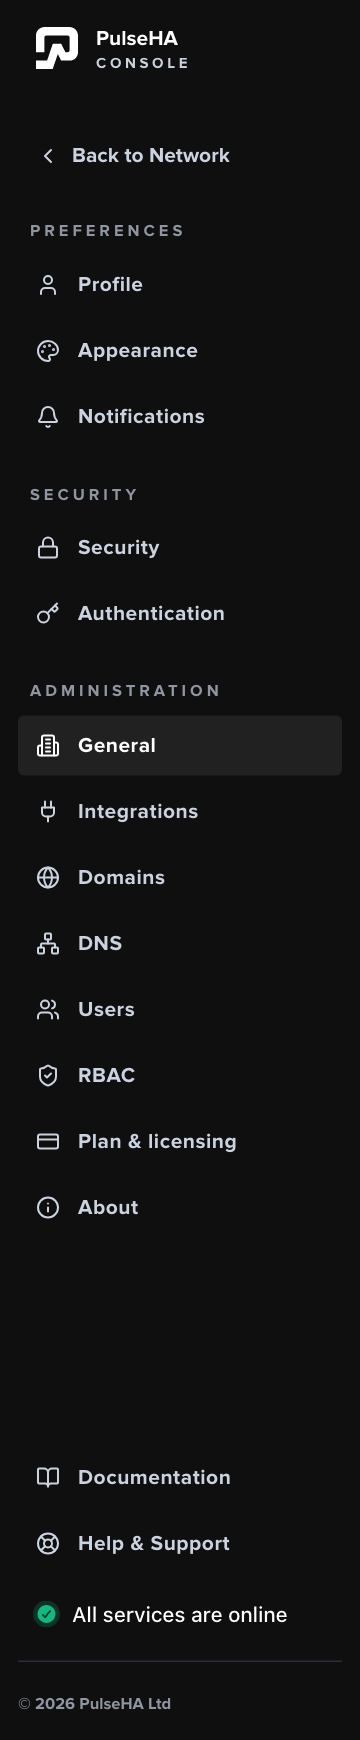
The Settings submenu. The back link at the top returns to whichever product you came from.
At the bottom of the menu, Documentation opens the in-console docs hub and Help & Support opens the contact page on pulseha.com. A Service Status badge from status.pulseha.com sits beneath them.
Network Overview#
The landing page is Network Overview. It pulls from five sources: gateways, services, devices, access decision statistics and the Zero Trust score. Each is fetched independently with an 8 second budget, so one slow source does not blank the page.
What you see, top to bottom:
- A Zero Trust Score badge linking to Security Overview.
- Quick actions: Add Device, Add Gateway, Create Policy.
- Four stat cards: Gateways (of N online), Devices (of N connected), Active device owners (check-in within 24h) and Services (of N healthy).
- Gateway locations, a map with a text list beneath it. Only gateways with usable location data appear.
- Action Center, which lists offline or degraded gateways, gateways with unknown status, service health issues, inactive devices, elevated access denials (above 30% with at least 50 decisions) and “No access policies”.
- Recent device check-ins and a Protected Services table showing the six services most in need of attention.
The page refreshes every 30 seconds while visible and again when the window regains focus. A line under the heading reads “Data fetched HH:MM:SS UTC” so you can tell how old the numbers are.
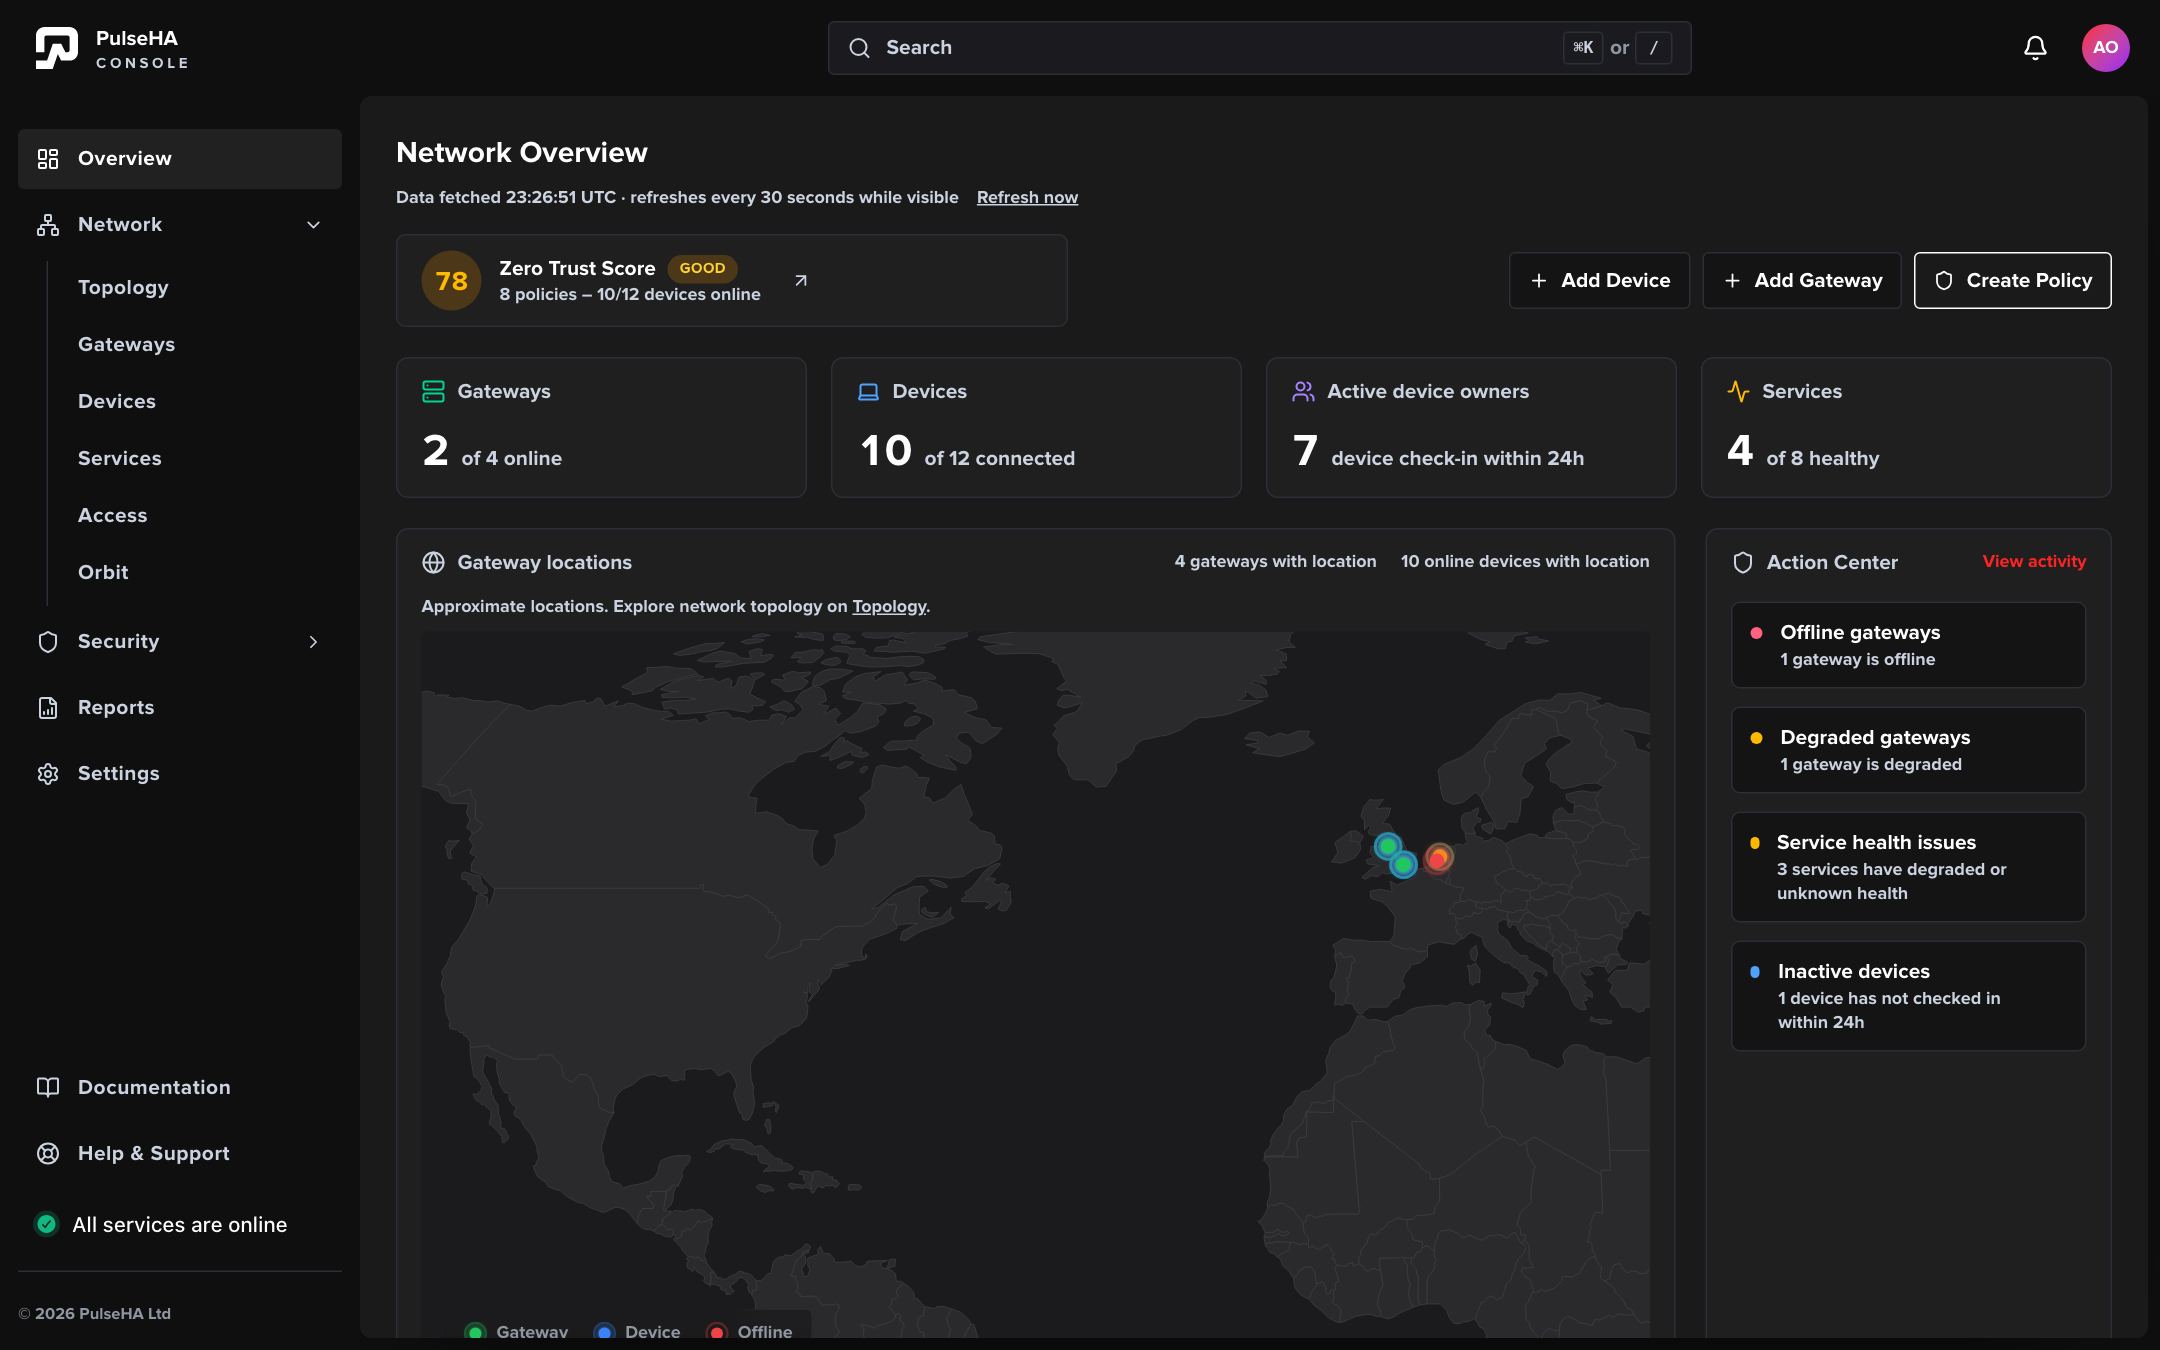
Network Overview with every source loaded. The four stat cards read “of N” against the full inventory, and the Action Center lists the offline and degraded gateways.
Reading “Unavailable” and partial data#
The console separates “we loaded nothing”, “we could not load” and “we loaded part of it”. Learn the three forms:
- Temporarily unavailable on a card means that source failed. The number is replaced by a dash. Nothing else on the page is affected.
- Partial data, view inventory means the source returned more than the overview reads (the gateway list caps at 200). Open the full page.
- Access restricted means your role cannot read that source.
When a source fails, an amber banner appears with a Retry button and a message naming the failed dataset. The Action Center then adds “Assessment incomplete” rather than reporting no issues. A detail drawer that fails to refresh keeps its last data and says “Showing previously loaded data” with the time of the last success.
Treat these states literally. An unavailable card is not a zero, a stale health sample is not a current one, and an Action Center with partial inputs has not cleared the gateways it could not see.
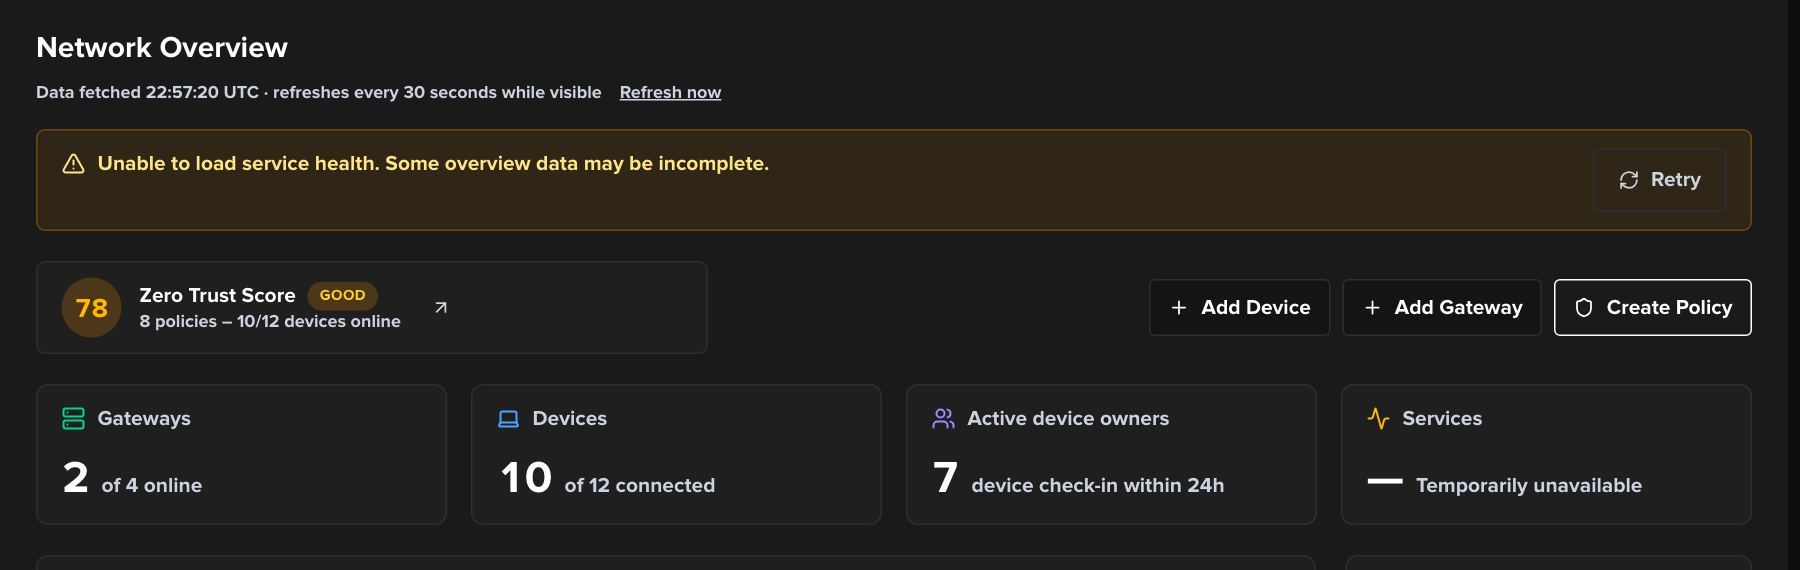
The Services source failed on this load. Its card shows a dash and “Temporarily unavailable” while the other three cards keep their numbers.
Search#
Press Ctrl+K (or Cmd+K on a Mac), or / when the cursor is not in a text field, to open the global search. It covers two things:
- Pages: every menu entry you can see, plus tools that are not in the menu, such as Policy Simulation.
- Workspace resources, once you type at least two characters: gateways, devices, services, users, groups, access policies, exit policies, routing rules, device policies, posture policies, Secure Web policies, domain lists, firewall rules, groups and IP lists, roles and support cases. Each type is filtered by your permissions.
Arrow keys move, Enter opens, Esc closes.
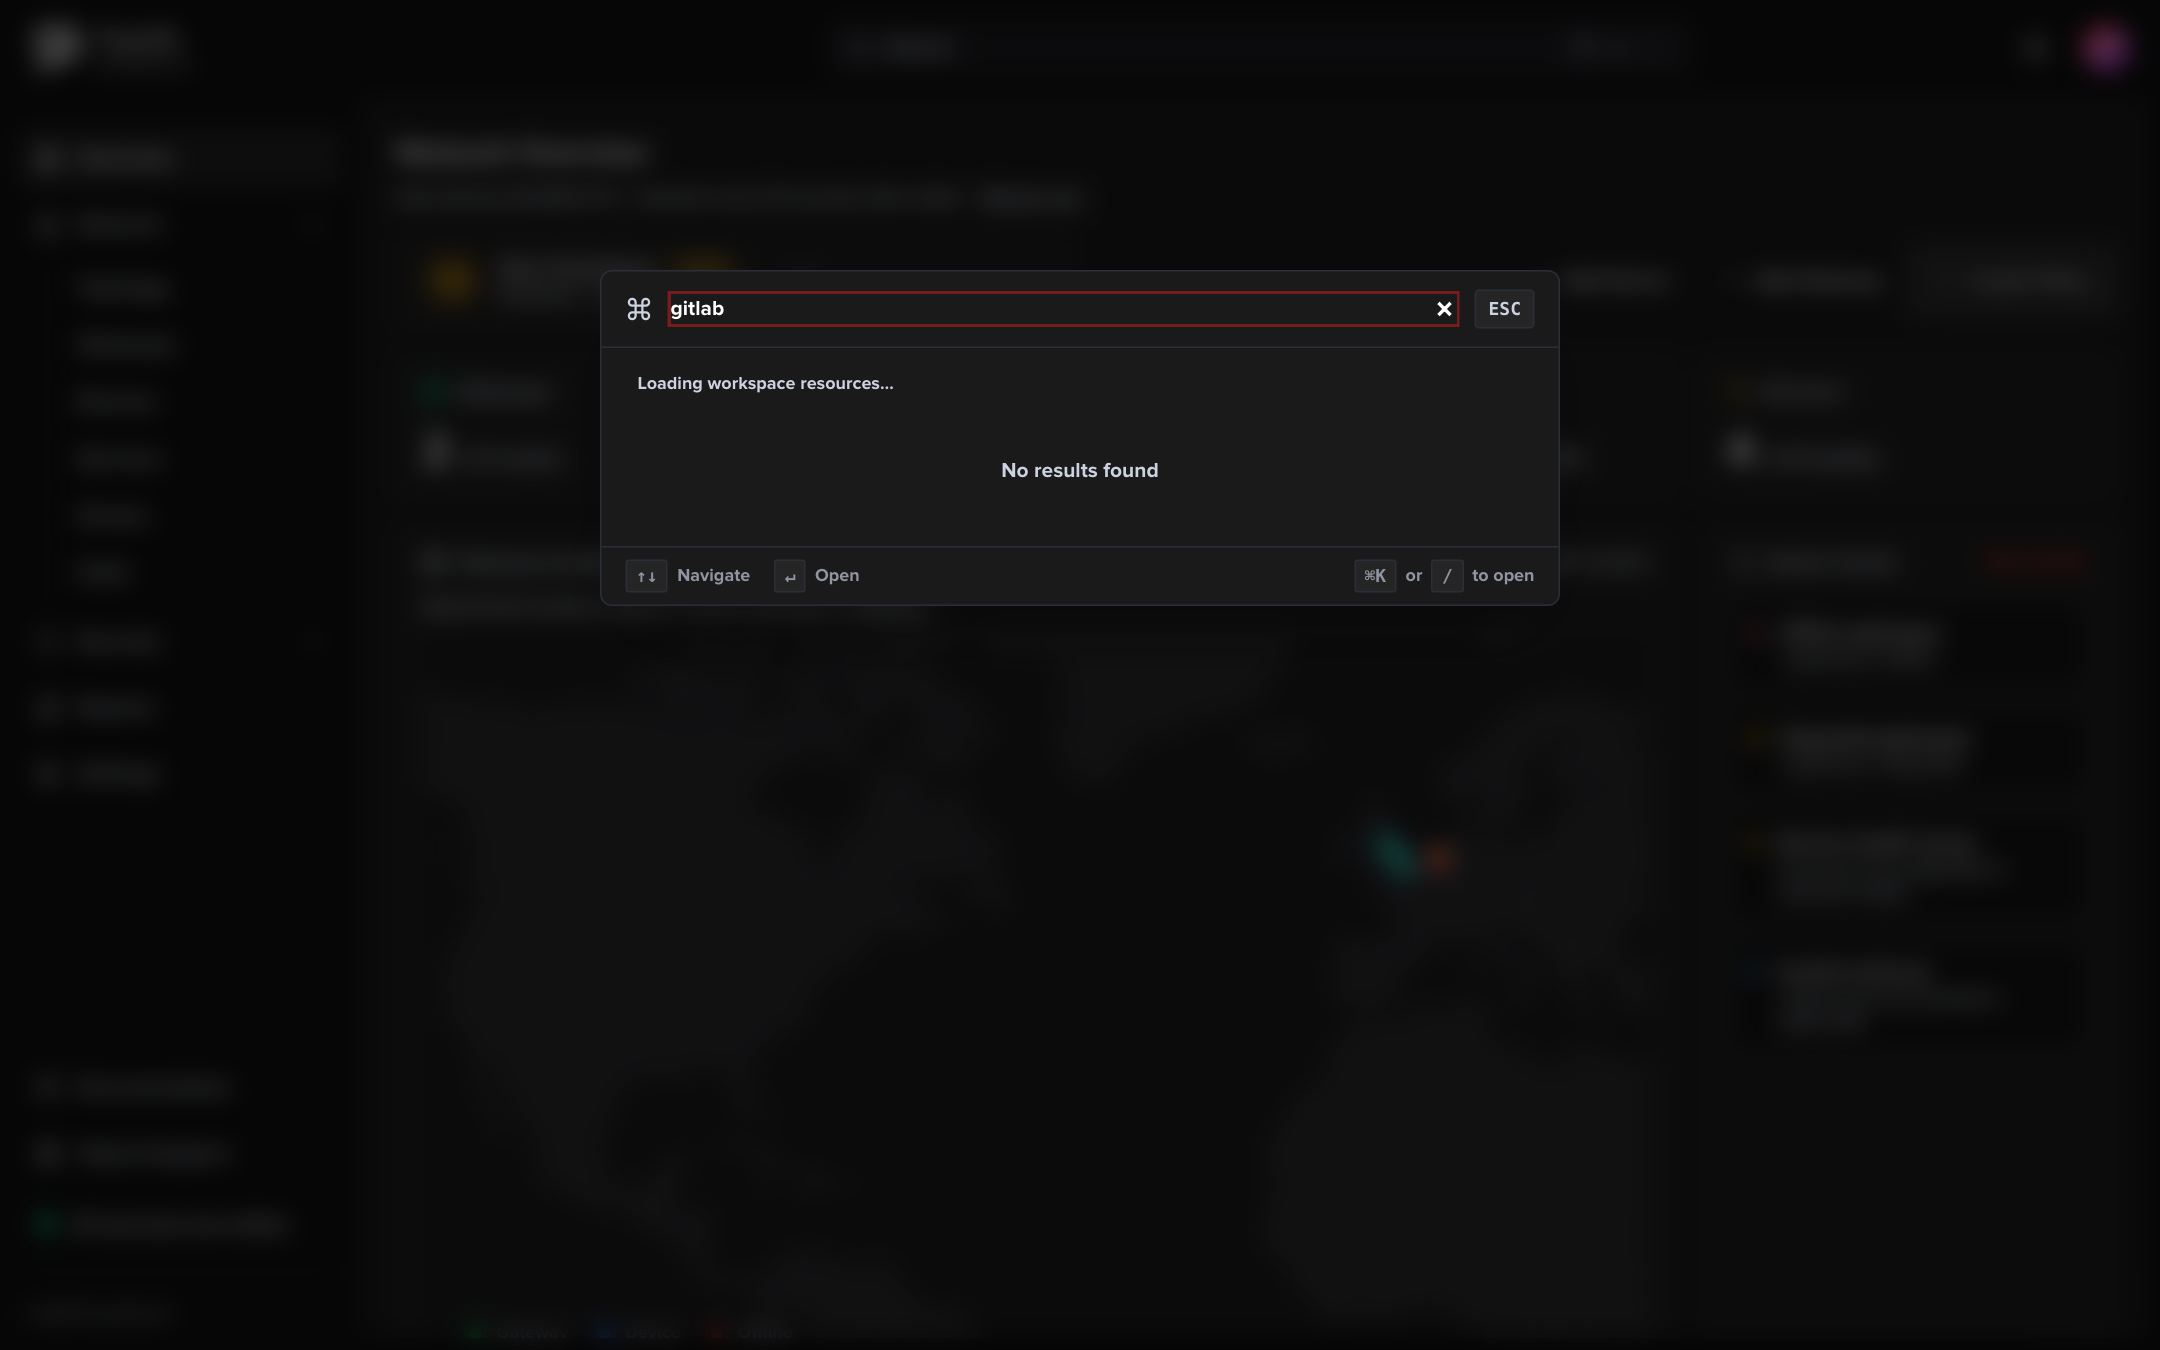
Global search after typing “gitlab”. Each result shows its type on the right: here two services and the access policy that grants them.
Status vocabulary#
The same words mean the same thing on every page.
| Area | Labels | Meaning |
|---|---|---|
| Device connection | Online, Recently seen, Tunnel down, Offline, Never connected | Online is a heartbeat within 4 minutes; Recently seen within 10 |
| Device lifecycle | Pending, Blocked, Archived, Revoked | Pending has not completed authorization; Revoked is permanent |
| Device posture | Compliant, Non-compliant, Stale, Unknown | Stale is a check older than 10 minutes; neither Stale nor Unknown counts as compliant |
| Gateway status | Online, Degraded, Offline, Unknown, Revoked | Revoked is sticky and shown in the detail drawer |
| Gateway version | Up to date, Update available, Upgrade required | Upgrade required means control refuses config until the package is updated |
| Gateway exit | Active, Capable | Capable means exit is possible but not enabled |
| Service health | HEALTHY, DEGRADED, DOWN, STALE, UNKNOWN, NOT MONITORED | Stale is no sample within 5 minutes; Not monitored is no probe configured |
| Policies | Enabled, Disabled; effect Allow, Deny | Enabled is desired state, not proof of application |
| Device policy settings | Enforced On, Enforced Off, User Choice | User Choice leaves the toggle to the user |
Tenants#
The console shows one tenant per sign-in. Your tenant’s name appears at the top of the user menu (the avatar at the top right) under a Tenant caption. There is no switcher; a user who works in several tenants signs in to each. Lab tenants carry an NFR badge there, and some Orbit configuration is read-only for them.
Common mistakes#
- Reading Online as access. Online is a heartbeat over HTTPS. Access needs a service, a policy, a handshake and a gateway rule.
- Trusting a stale count. If the freshness line is old or a card says unavailable, press Refresh now before acting.
- Looking for Policy Simulation in the menu. It is reached from Simulate on the Access page, from a policy’s row menu, or from search.