Device policies
Apply fleet-wide agent connectivity and security settings.
Device policies push agent settings to your fleet: whether the agent connects on start, whether users can disconnect, kill switch, trusted networks, DNS overrides and more. They live under Network → Devices → Device Policies. They configure agent behaviour; they do not check device health. For health checks and enforcement use Device posture.
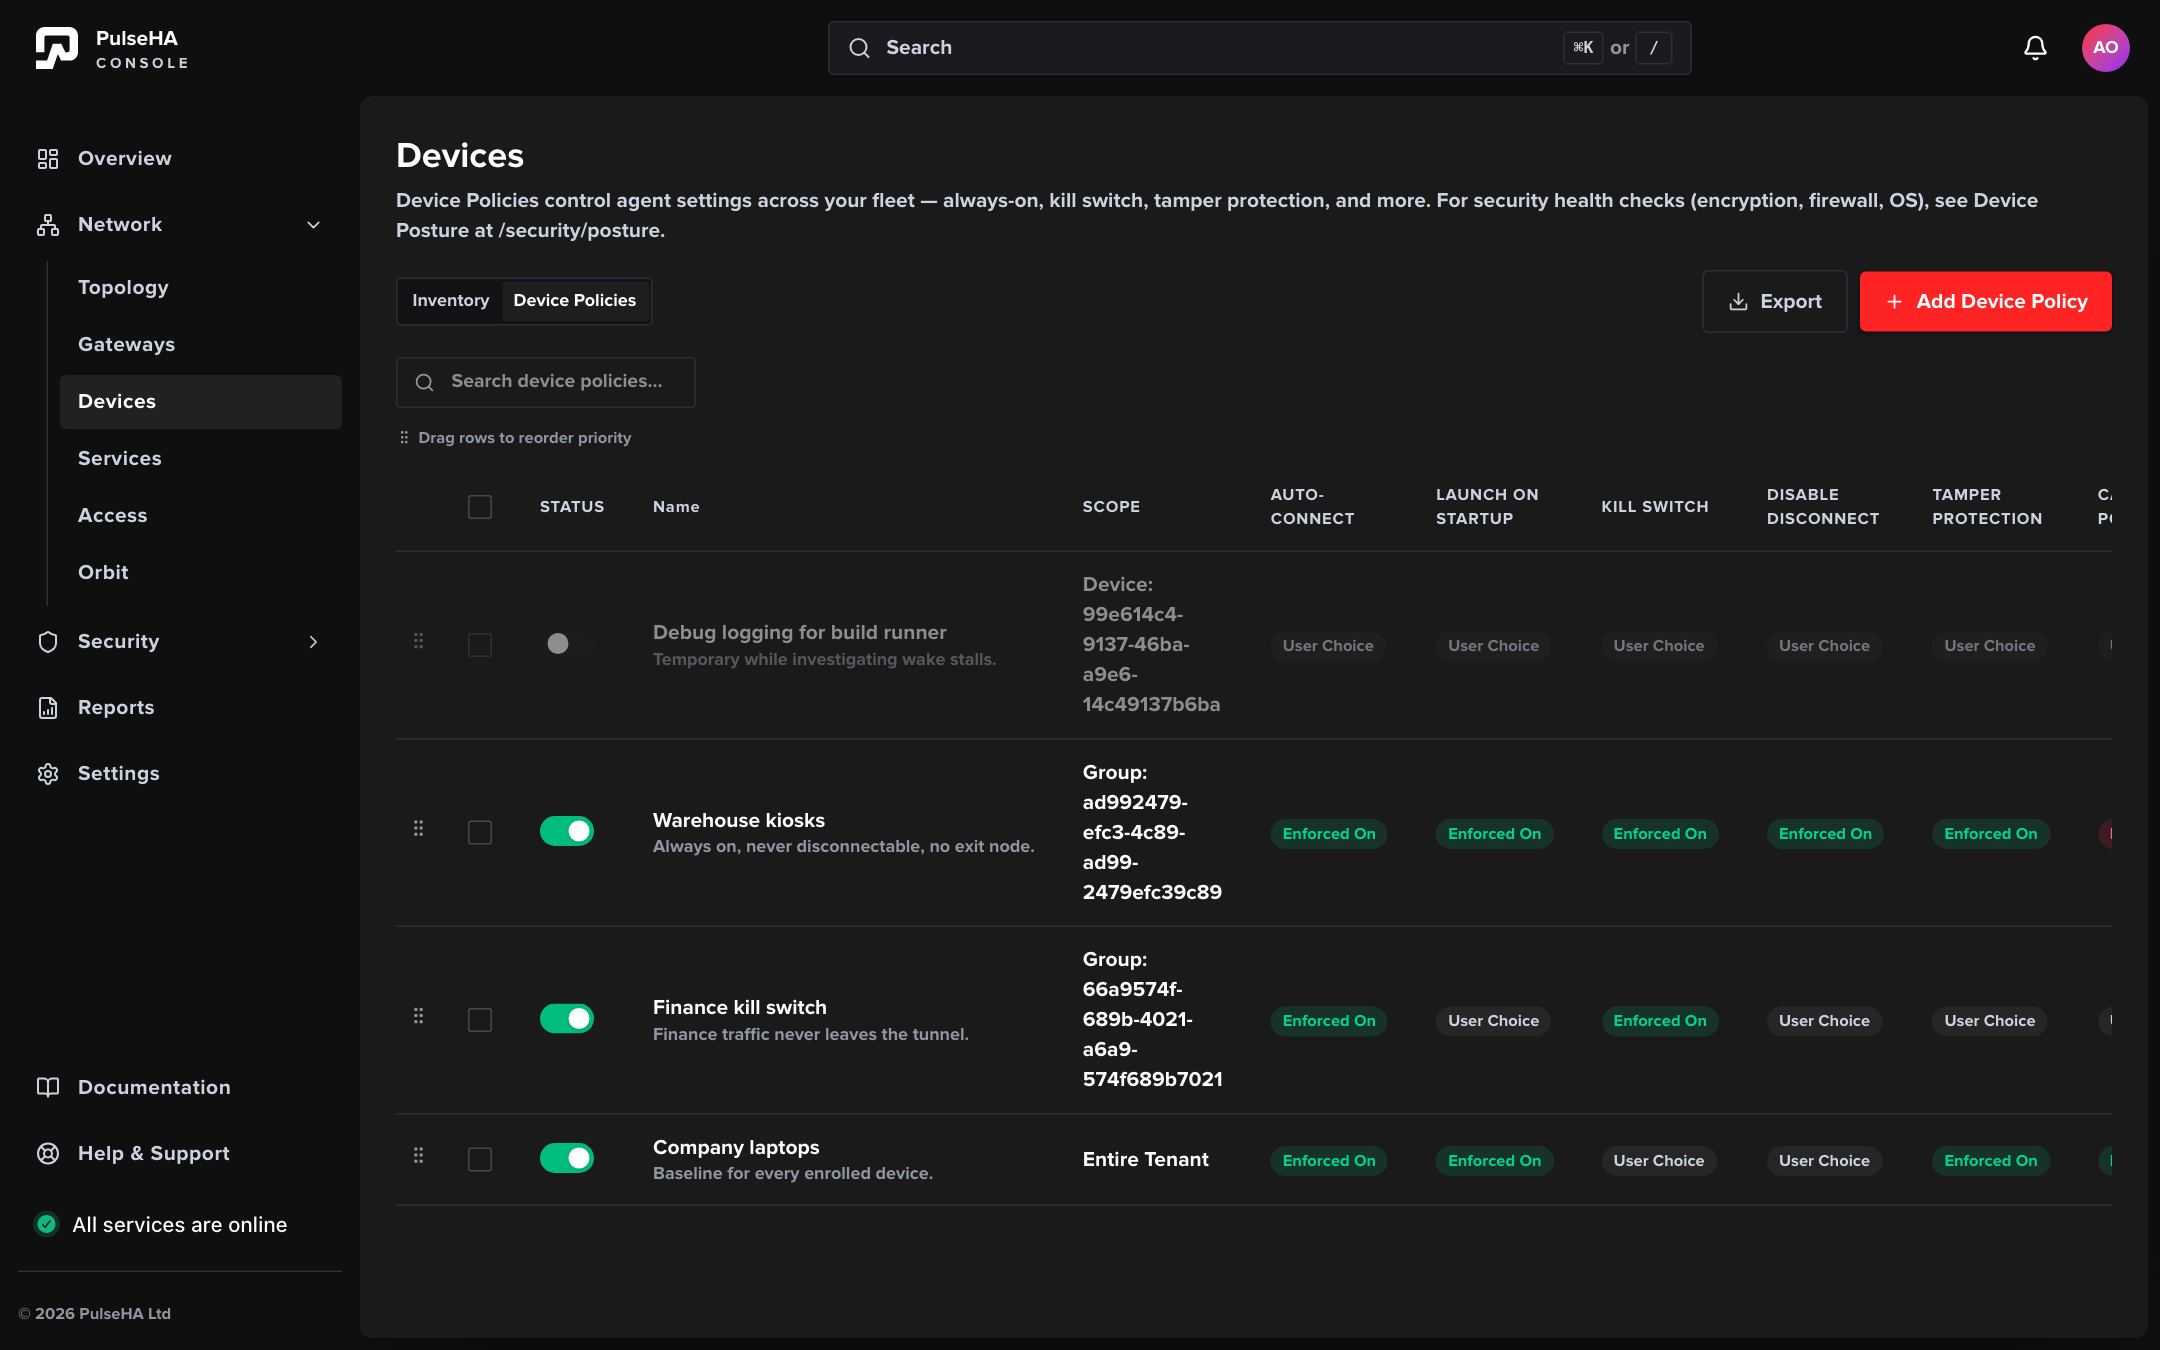
Each column is one agent setting; the chips read Enforced On, Enforced Off or User Choice so you can see the cascade at a glance.
Before you start#
- Viewing the tab needs
policies:view. Add Device Policy needspolicies:create(owners, admins and users). Editing, toggling and reordering needpolicies:update; deleting needspolicies:delete(owners and admins). - Decide the scope first. A policy targets the Entire Tenant, a Role, a Group or a single Device. One policy exists per subject; saving again for the same subject replaces it.
- Every setting has three states: Enforce On, Enforce Off and User Choice. User Choice leaves the decision to the next policy in the cascade, and finally to the user.
Create a policy#
- Open Network → Devices, switch to Device Policies and click Add Device Policy.
- Enter a Policy Name (required) and an optional Description.
- Under Scope & Targeting choose Entire Tenant, Role, Group or Device. For a role enter the Role ID; for a group or device pick one from Select Group or Select Device. Saving without a target shows Please select or enter a target for the selected scope.
- Under Connectivity set Auto-Connect (connect when the agent starts), Launch on Startup (start the agent at login) and Session Timeout in hours (
0disables forced re-authentication). - Under Security set Kill Switch (block all traffic while disconnected), Disable Disconnect (users cannot disconnect manually) and Tamper Protection (users cannot stop or uninstall the agent).
- Under Network set Captive Portal Detection, Trusted Networks (comma-separated SSIDs or subnets where the agent disconnects) and DNS Servers (comma-separated IPs used while connected).
- Under Management set Minimum Agent Version (older agents are prompted to update), Log Level Override (Debug, Info, Warn, Error or Default) and Priority (default
100; lower numbers win when policies overlap). - Click Create Policy. You return to the Device Policies tab.
The Policy Summary on the right previews each setting as Enforced On, Enforced Off or User Choice while you edit.
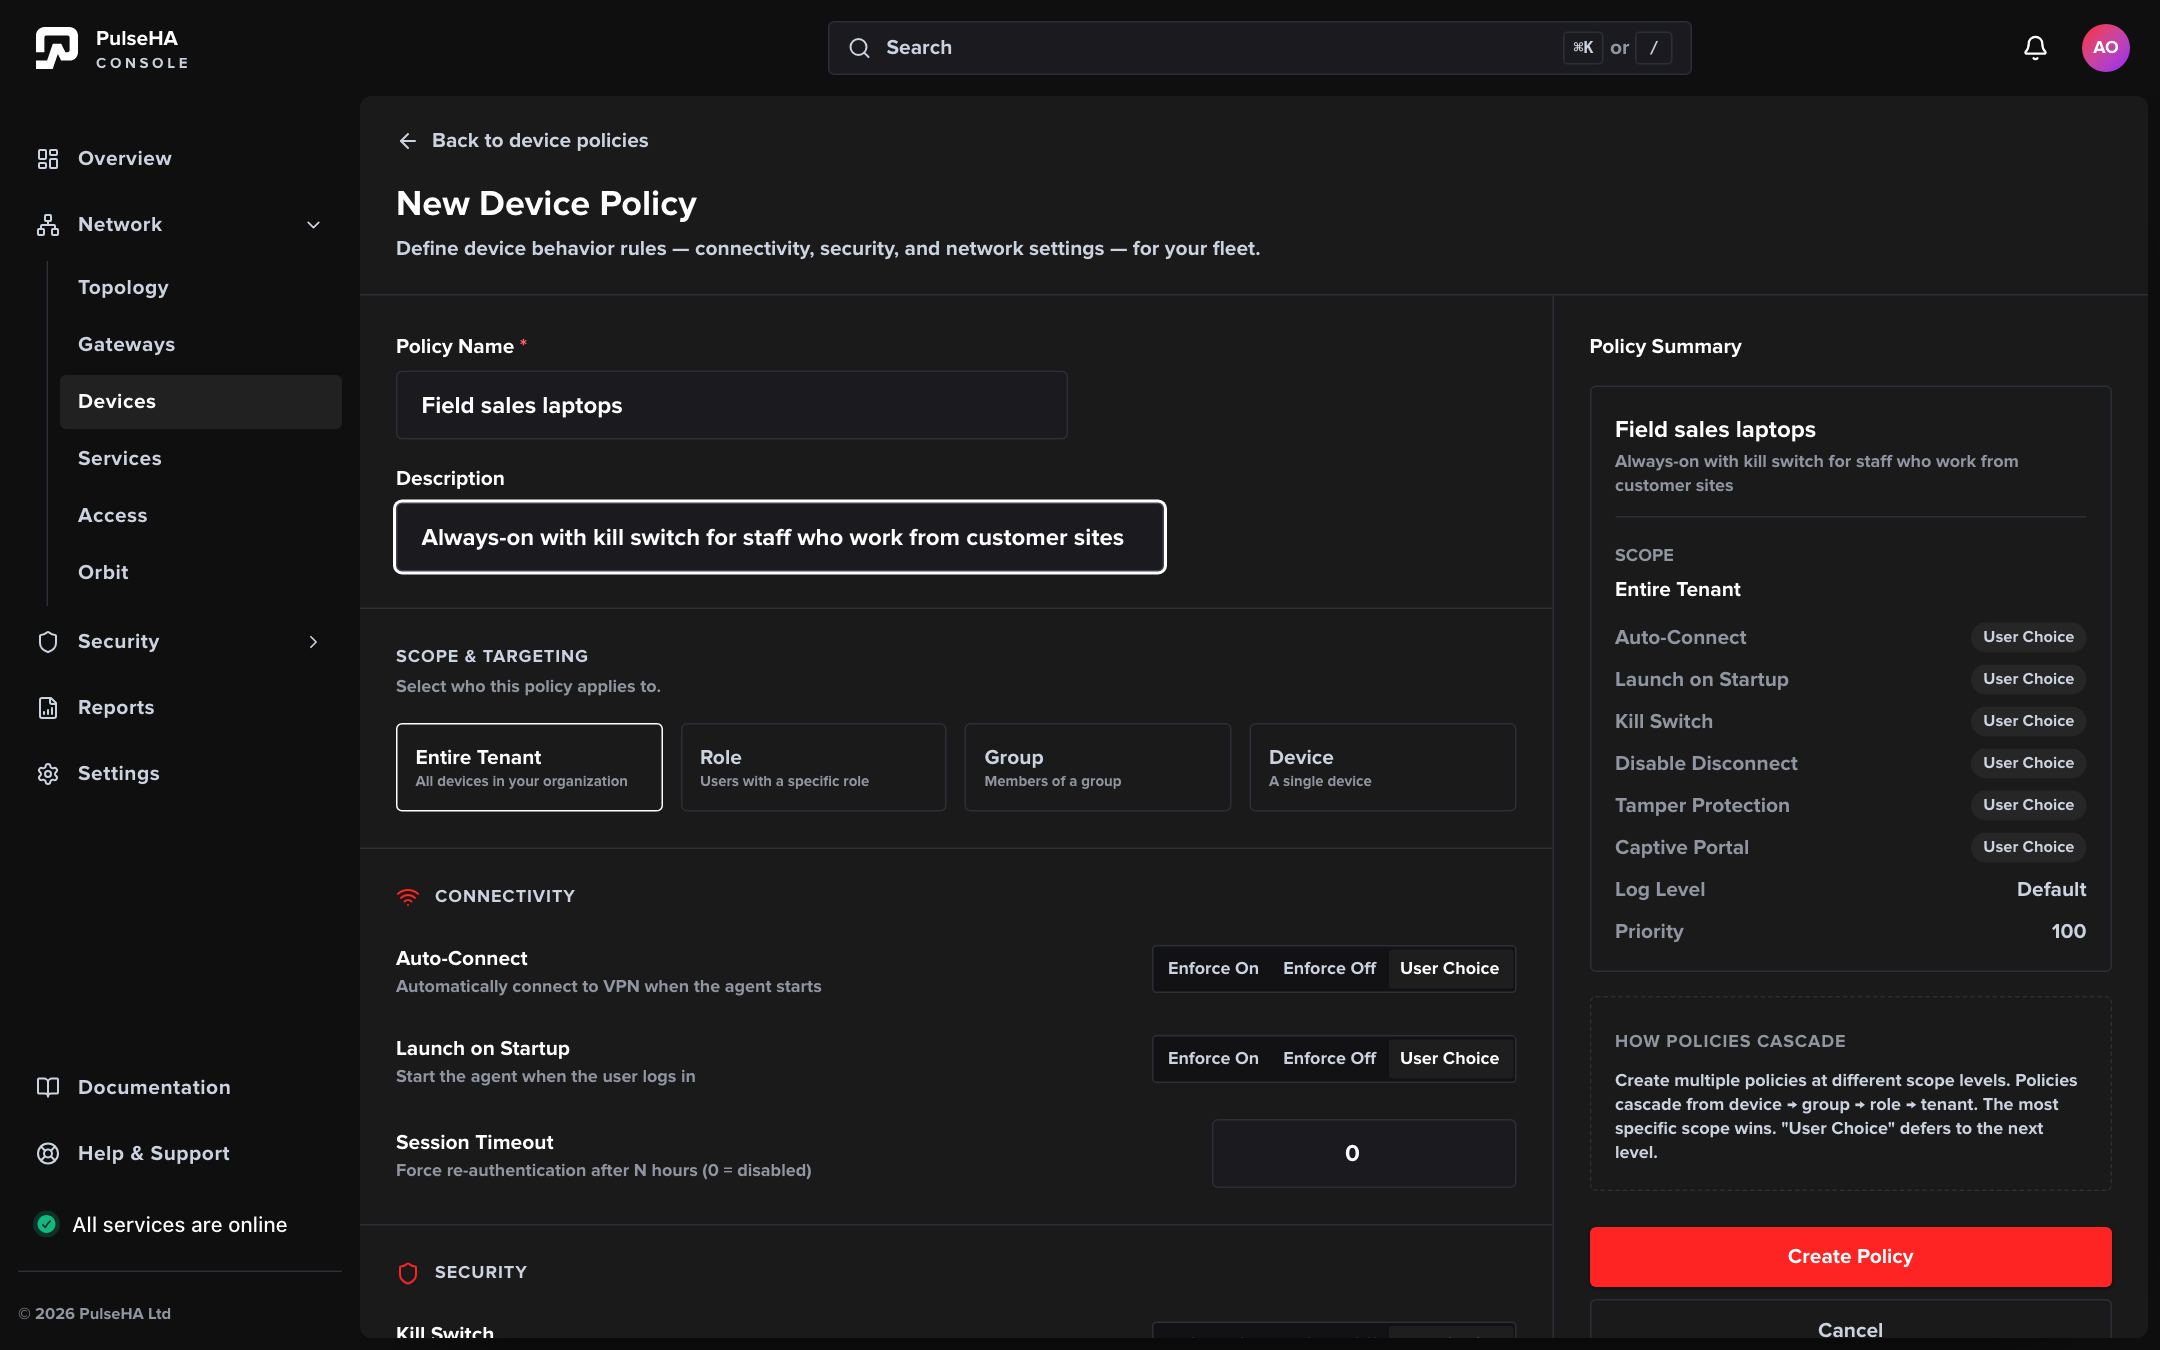
The form groups settings by area; the summary on the right updates as you change each one.
Read the table#
| Column | Meaning |
|---|---|
| Status | Switch (or Enabled / Disabled chip without update rights). Disabled policies are skipped |
| Name | Policy name, or the scope label when unnamed |
| Scope | Entire Tenant, or Role: <id>, Group: <id>, Device: <id> |
| Auto-Connect, Launch on Startup, Kill Switch, Disable Disconnect, Tamper Protection, Captive Portal | The enforcement state for that setting |
| Log Level | The override, or Default |
The row menu offers Edit policy and Delete policy. When the table is sorted by priority and no search is active, drag rows to reorder; the console rewrites priorities in steps of 10 and shows Policy order updated. Deleting asks Delete this device policy? Users will regain control of these settings. Export downloads the policies as JSON.
How the effective policy is resolved#
When an agent fetches its configuration, the control plane walks the policies that apply to it in this order: the device policy, then each group the device’s user belongs to, then each role, then the tenant policy. Disabled policies are skipped.
For every setting, the first policy that enforces a value sets it. A later policy in the walk replaces that value only if its Priority number is lower than every policy already seen. With equal priorities the most specific scope wins, which is what the form’s How Policies Cascade note describes. Settings left at User Choice in every policy are not sent, and the agent keeps its local default.
The policy simulator shows a Device Policy stage. It lists the device policies that apply and fails the stage when the agent’s version is below a Minimum Agent Version.
Troubleshooting#
- A setting is not applied on the device. Check that the policy is Enabled, that its scope matches the device (device ID, the user’s group or role, or tenant), and that no other policy with a lower priority number enforces a different value. Then check the agent is connecting and fetching configuration.
- Two policies disagree. Compare their Priority values. The lower number wins across scopes; equal numbers resolve to the more specific scope.
- “Failed to toggle device policy” or “Failed to update N policies” after a drag.** The save did not reach the control plane. Refresh and retry.
- A role-scoped policy never matches. The Role ID field takes the role’s identifier, not its name. Copy it from Settings → Roles.
- Posture checks are not affected. Correct: device policies never evaluate disk encryption, firewall, OS version, screen lock or EDR. Those belong to Device posture. Who can reach an application belongs to Access policies.