Device trust
Control how endpoints prove organization membership.
Device enrollment decides how a person proves who they are when a new device joins your organization. The settings live on the Device enrollment tab of Settings → Authentication. The older Settings → Device Trust URL redirects there.
Before you start#
- The tab needs
sso.readto view. Setting up, editing and removing the Microsoft Entra ID option needssso.create,sso.updateandsso.delete. Under the built-in roles that is Owner. - Browser sign-in is always available and needs no configuration.
- Microsoft Entra ID device login applies to Windows devices with the PulseHA agent. You need an Entra administrator to create the app registration.
- Device health requirements and resource access are separate controls. See Device posture and Access policies.
Enroll a device with browser sign-in#
The tab’s Browser sign-in card is marked Available. Expand How browser enrollment works to see the flow:
- The user runs
pulsectl loginon the device. - The agent displays a URL and a code.
- The user opens the URL in a browser and enters the code.
- After approval, the agent connects automatically.
Confirm the device under Network → Devices (the tab links there as View enrolled devices).
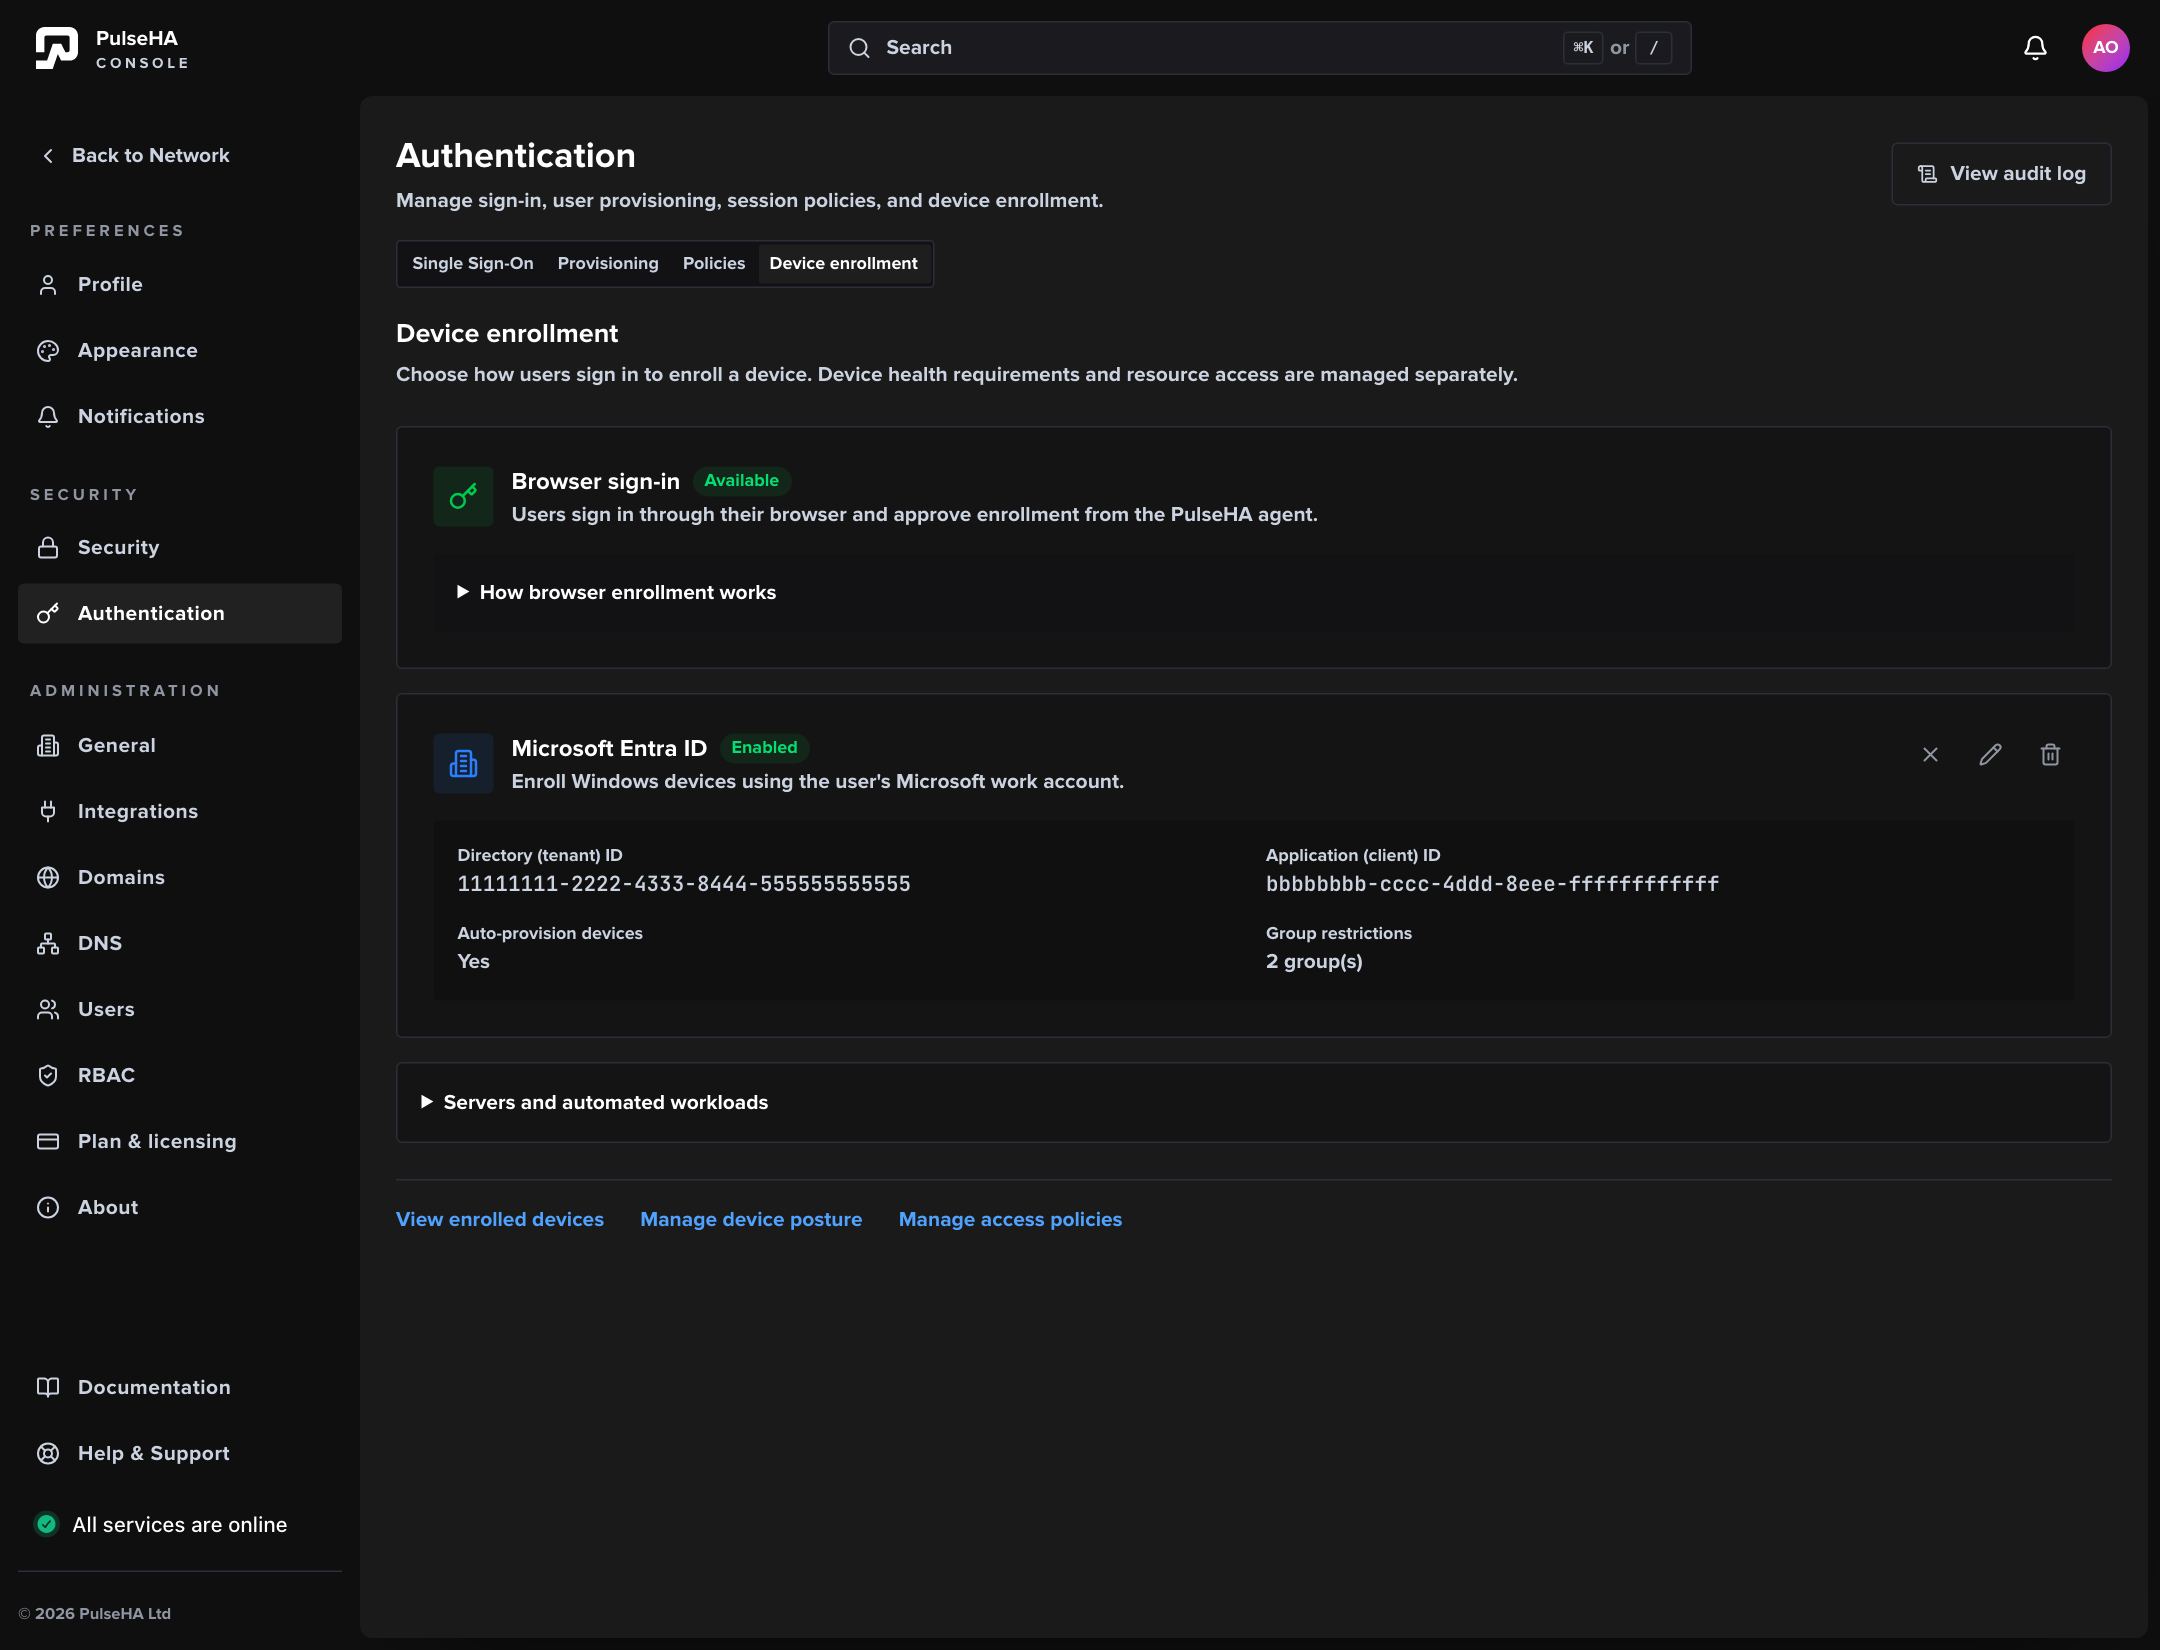
The Device enrollment tab: Browser sign-in is always Available, and the Microsoft Entra ID card shows both IDs, auto-provisioning and group restrictions.
Set up Microsoft Entra ID device login#
- Open Settings → Authentication → Device enrollment and choose Set up Microsoft Entra ID.
- Azure Setup: follow the five steps in the Entra admin center. They cover creating the app registration, the broker redirect URI, copying the two IDs, setting the Application ID URI (shown as
api://<application-client-id>with a copy button) and allowing public client flows. Choose Next. - Credentials: paste the Directory (tenant) ID and Application (client) ID. Both must be GUIDs. Optionally add group object IDs under Restrict to Entra groups (optional) and tick or clear Auto-provision devices on first sign-in. Choose Save & Continue.
- Verify: choose Run verification. It checks Directory (tenant) ID format, Application (client) ID format and Entra tenant exists. You can only move on when the result is Configuration looks good.
- Deploy: copy the two-line
agent.yamlsnippet and push it to your Windows devices. The default path isC:\ProgramData\PulseHA\agent.yaml. Choose Finish Setup.
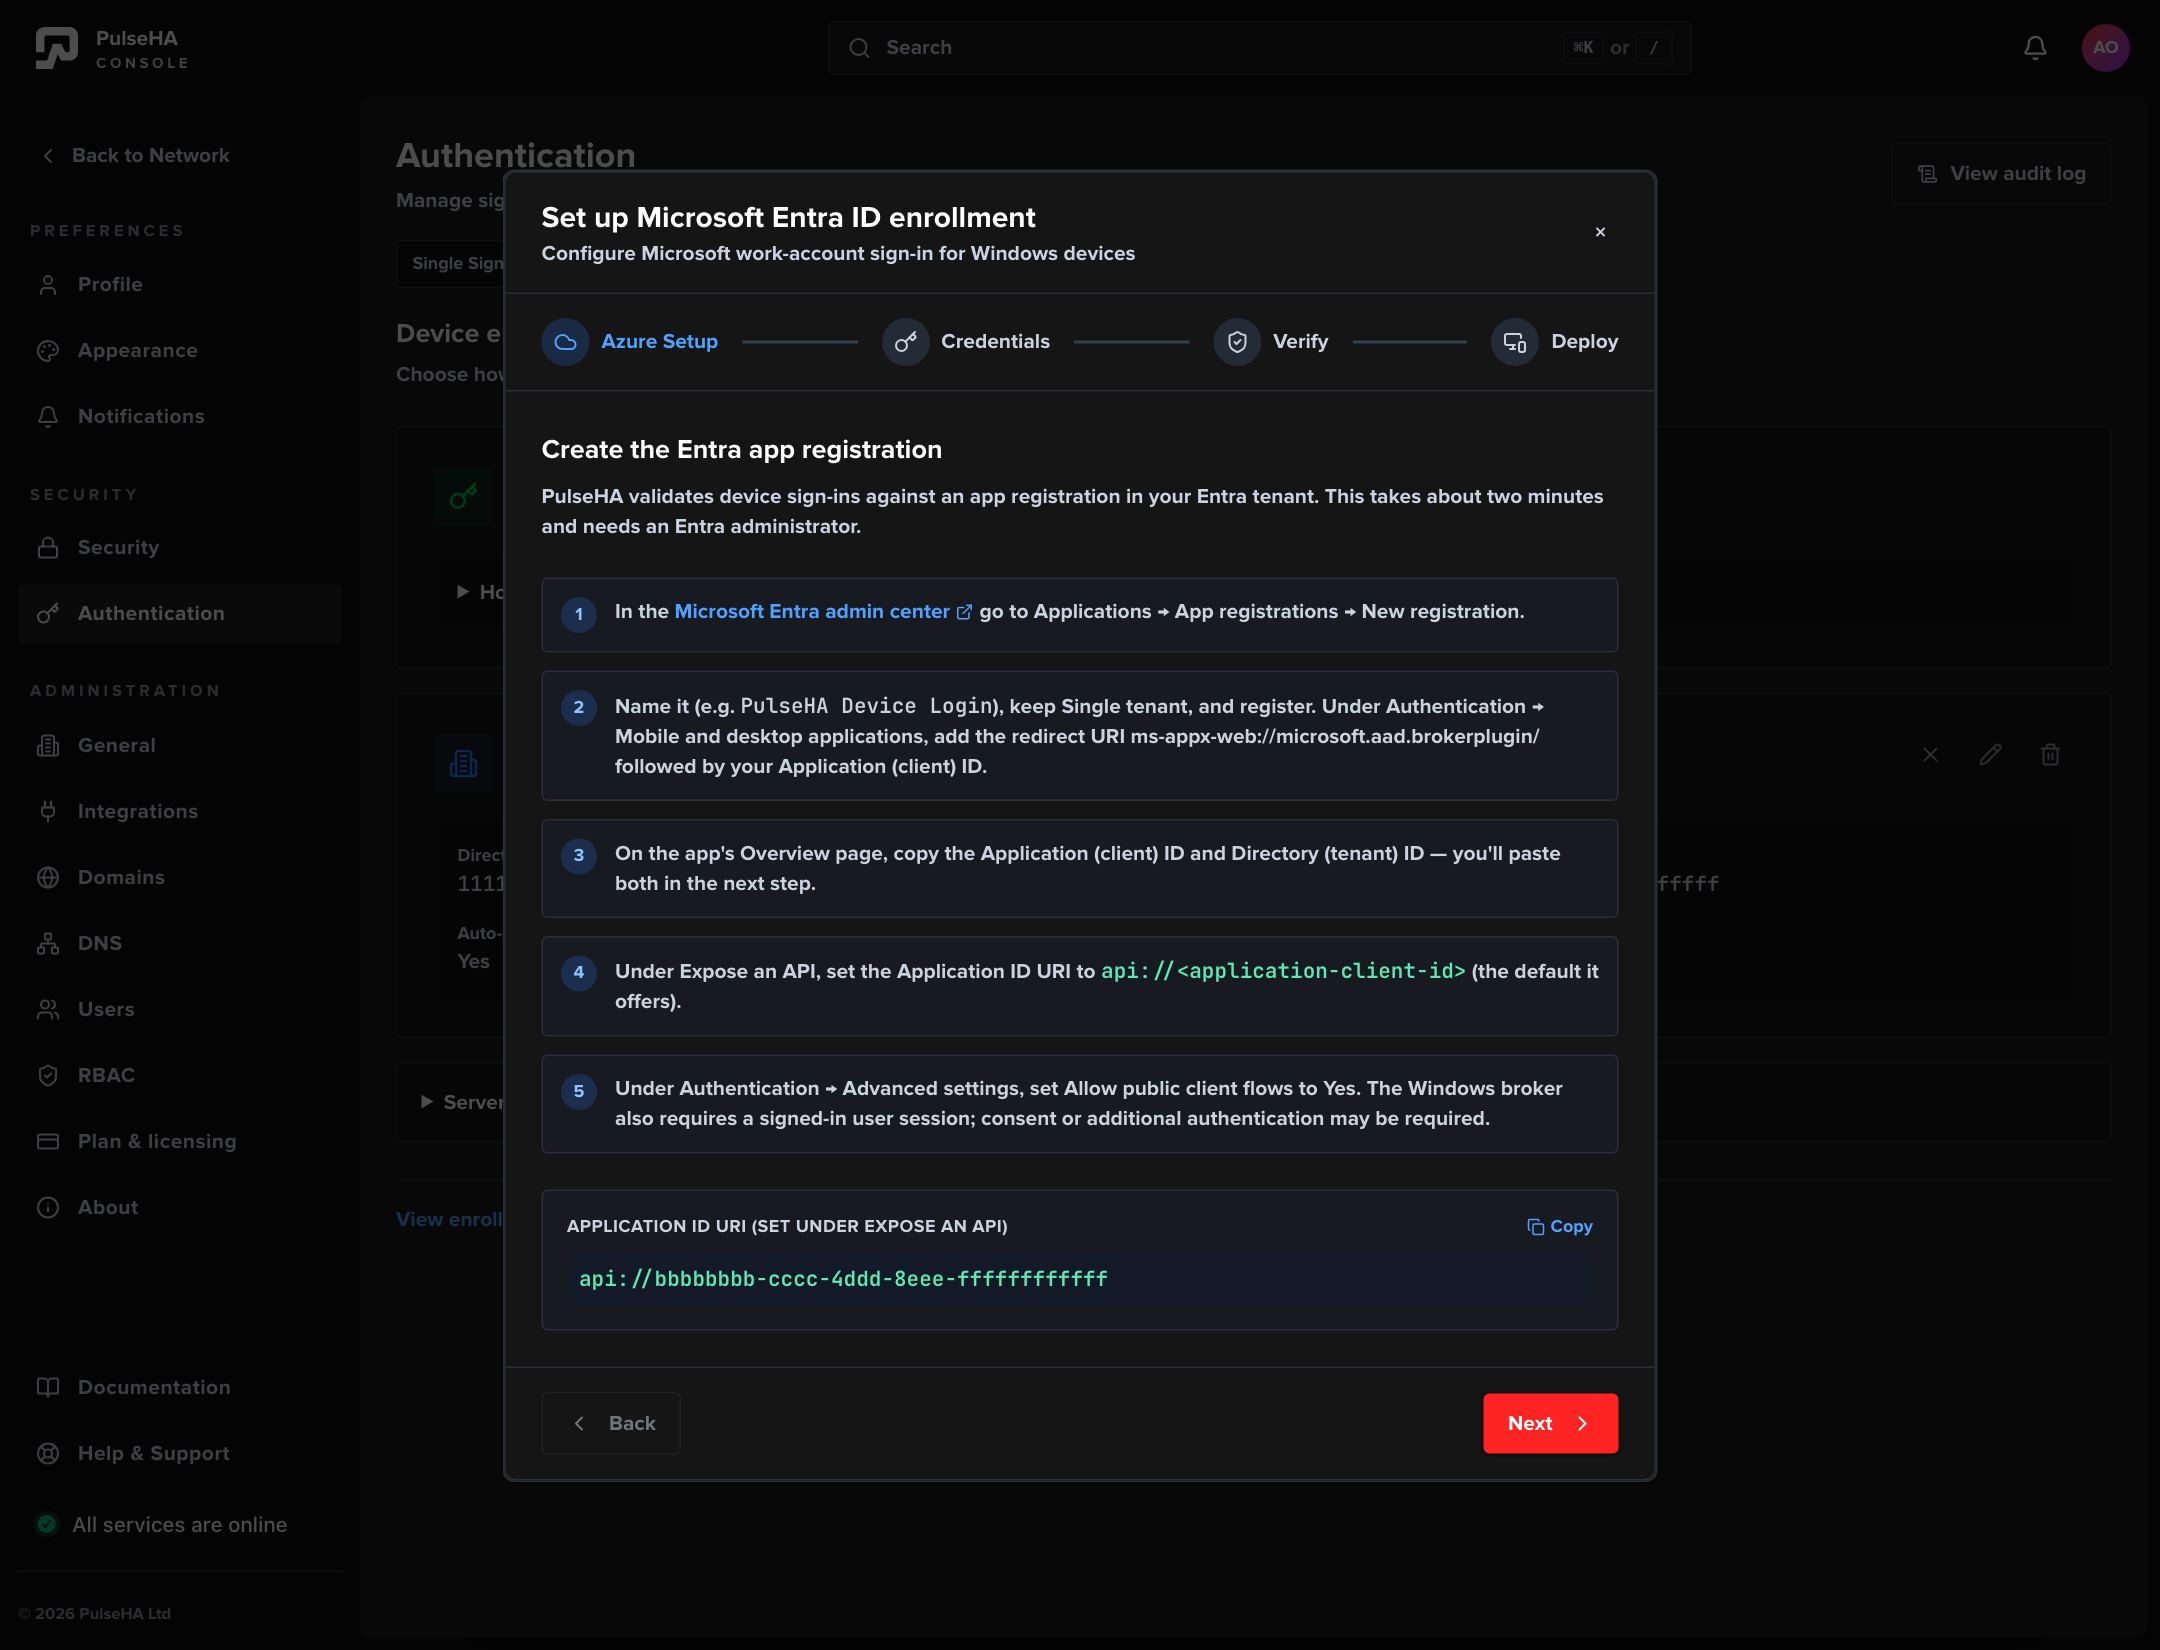
The Azure Setup step of the Entra ID wizard, with the five app registration steps and the progress bar across the top.
The configuration is saved disabled. When a controlled Windows sign-in test is ready, use the tick icon on the Microsoft Entra ID card to enable it. The card shows Enabled or Disabled, both IDs, Auto-provision devices and Group restrictions.
Edit, disable or remove Entra ID login#
- Use the pencil icon to reopen the wizard. Changing either ID disables the configuration again until you re-enable it.
- Use the cross icon to disable without deleting.
- Use the bin icon and confirm Remove. Devices then fall back to the browser device flow. Already enrolled devices keep working.
Reference#
| Method | Where configured | Notes |
|---|---|---|
| Browser sign-in | Always on | pulsectl login, URL and code, approve in browser. |
| Microsoft Entra ID | This tab | Windows devices, Entra joined or hybrid joined, user signed in with their Entra account. |
| Enrollment tokens | Enrollment API | Unattended installs for servers. Not managed in the console. |
| Workload identity | Enrollment API | OIDC federation for CI/CD. Not managed in the console. |
Agent snippet written by the wizard:
auth:
  entra_auto_login: true
  entra_client_id: "<application-client-id>"
Device requirements shown on the Deploy step: Windows 10 1903 or later with the PulseHA agent (the MSI includes the Entra helper), Entra ID joined or hybrid joined (check with dsregcmd /status), and the user signed in to Windows with their Entra account.
Troubleshooting#
- “Must be a valid GUID”. Copy the IDs from the app registration’s Overview page. Do not use the display name or the Application ID URI.
- Entra tenant exists fails with “Microsoft returned … for this tenant”. The Directory (tenant) ID is wrong. Re-check it.
- “Could not reach login.microsoftonline.com”. The control plane could not reach Microsoft. Retry later.
- “entra config already exists for this tenant”. Only one Entra configuration is allowed. Edit the existing card instead of creating another.
- The card flipped to Disabled after an edit. You changed a tenant or client ID. Re-run verification and enable it again deliberately.
- Enrollment fails with an audience mismatch. The Application (client) ID in the console does not match the app registration the agent uses. Compare both.
- “You do not have permission to view device enrollment settings.” Your role lacks
sso.read. - A device stays pending after browser sign-in. Restart
pulsectl loginand complete the approval again. Revoked devices must be enrolled again.