Authentication
Configure SSO, SCIM provisioning, and session policy.
Settings → Authentication is where you connect an identity provider, issue SCIM tokens, decide whether SSO is optional or required, and choose how devices enroll. Use it when you first roll out single sign-on or when you rotate credentials.
Before you start#
- The Authentication link appears for users with
sso:manage. The page itself needssso.read; adding, changing and removing providers needsso.create,sso.updateandsso.delete. Under the built-in roles Owner holds all of these. - SCIM token actions need
scim.read,scim.createandscim.revoke. - You need admin access to your identity provider to register an application and copy its values.
- Keep a password-capable owner account available until SSO is proven. Required for all disables password login.
Connect an identity provider#
- Open Settings → Authentication. The Single Sign-On tab is selected.
- Pick a provider card: Microsoft Entra ID, Okta, Google Workspace, Custom OIDC or Custom SAML. If providers already exist, choose Add provider first.
- Basics: set a Display name and add Email domains. Users with these email domains are routed to this provider. Choose Start setup.
- IdP Setup: follow the numbered guide for your provider. Copy the Redirect URI (add to your IdP) for OIDC. For SAML, copy SP Entity ID (Audience), ACS URL (Reply URL) and SP Metadata URL. If your IdP needs a signing certificate, choose Generate SP Certificate. Choose Next.
- Connect: for OIDC enter the vendor value (Directory (tenant) ID for Entra, Okta org URL for Okta, Discovery URL for custom), the Client ID, an Authentication method (Client secret or Federated credential) and Scopes. For SAML paste a Metadata URL or Paste Metadata XML. Choose Save & Continue.
- Domains: for each domain choose Verify Domain, publish the TXT record shown, then Check DNS.
- Test & Enable: choose Test configuration. When it reports Configuration valid, choose Enable, then Finish.
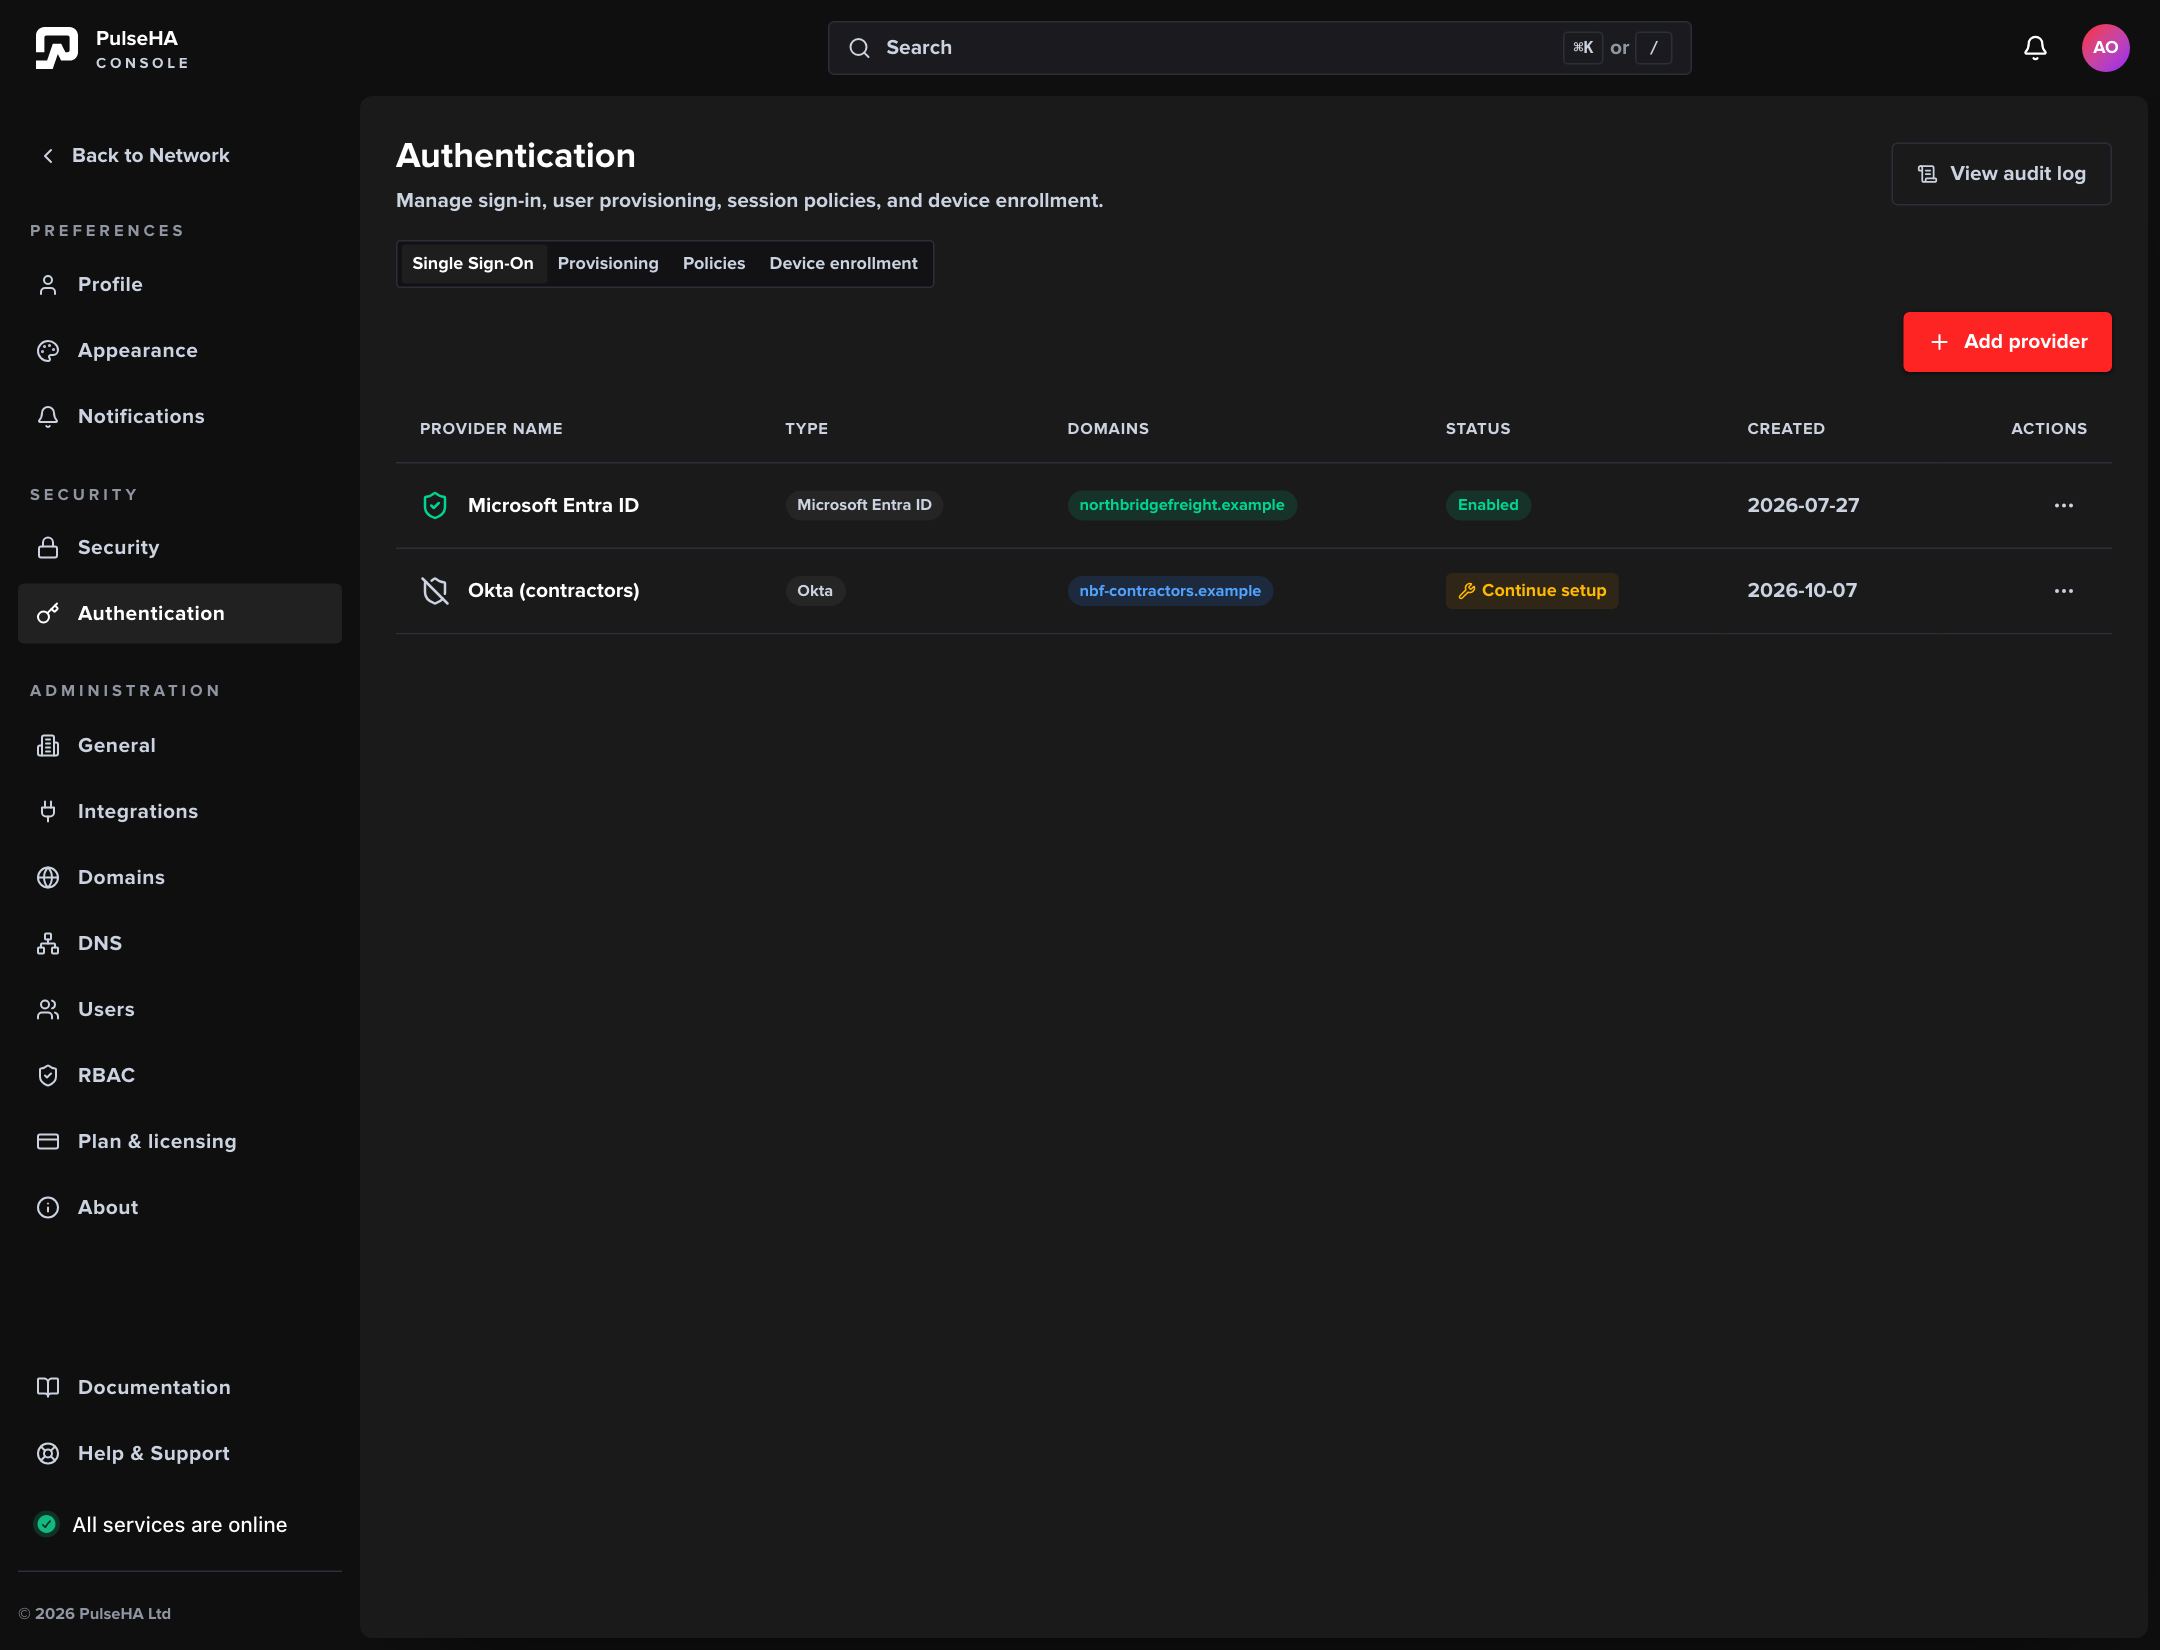
The Single Sign-On tab with an enabled Microsoft Entra ID provider and an Okta provider still showing Continue setup.
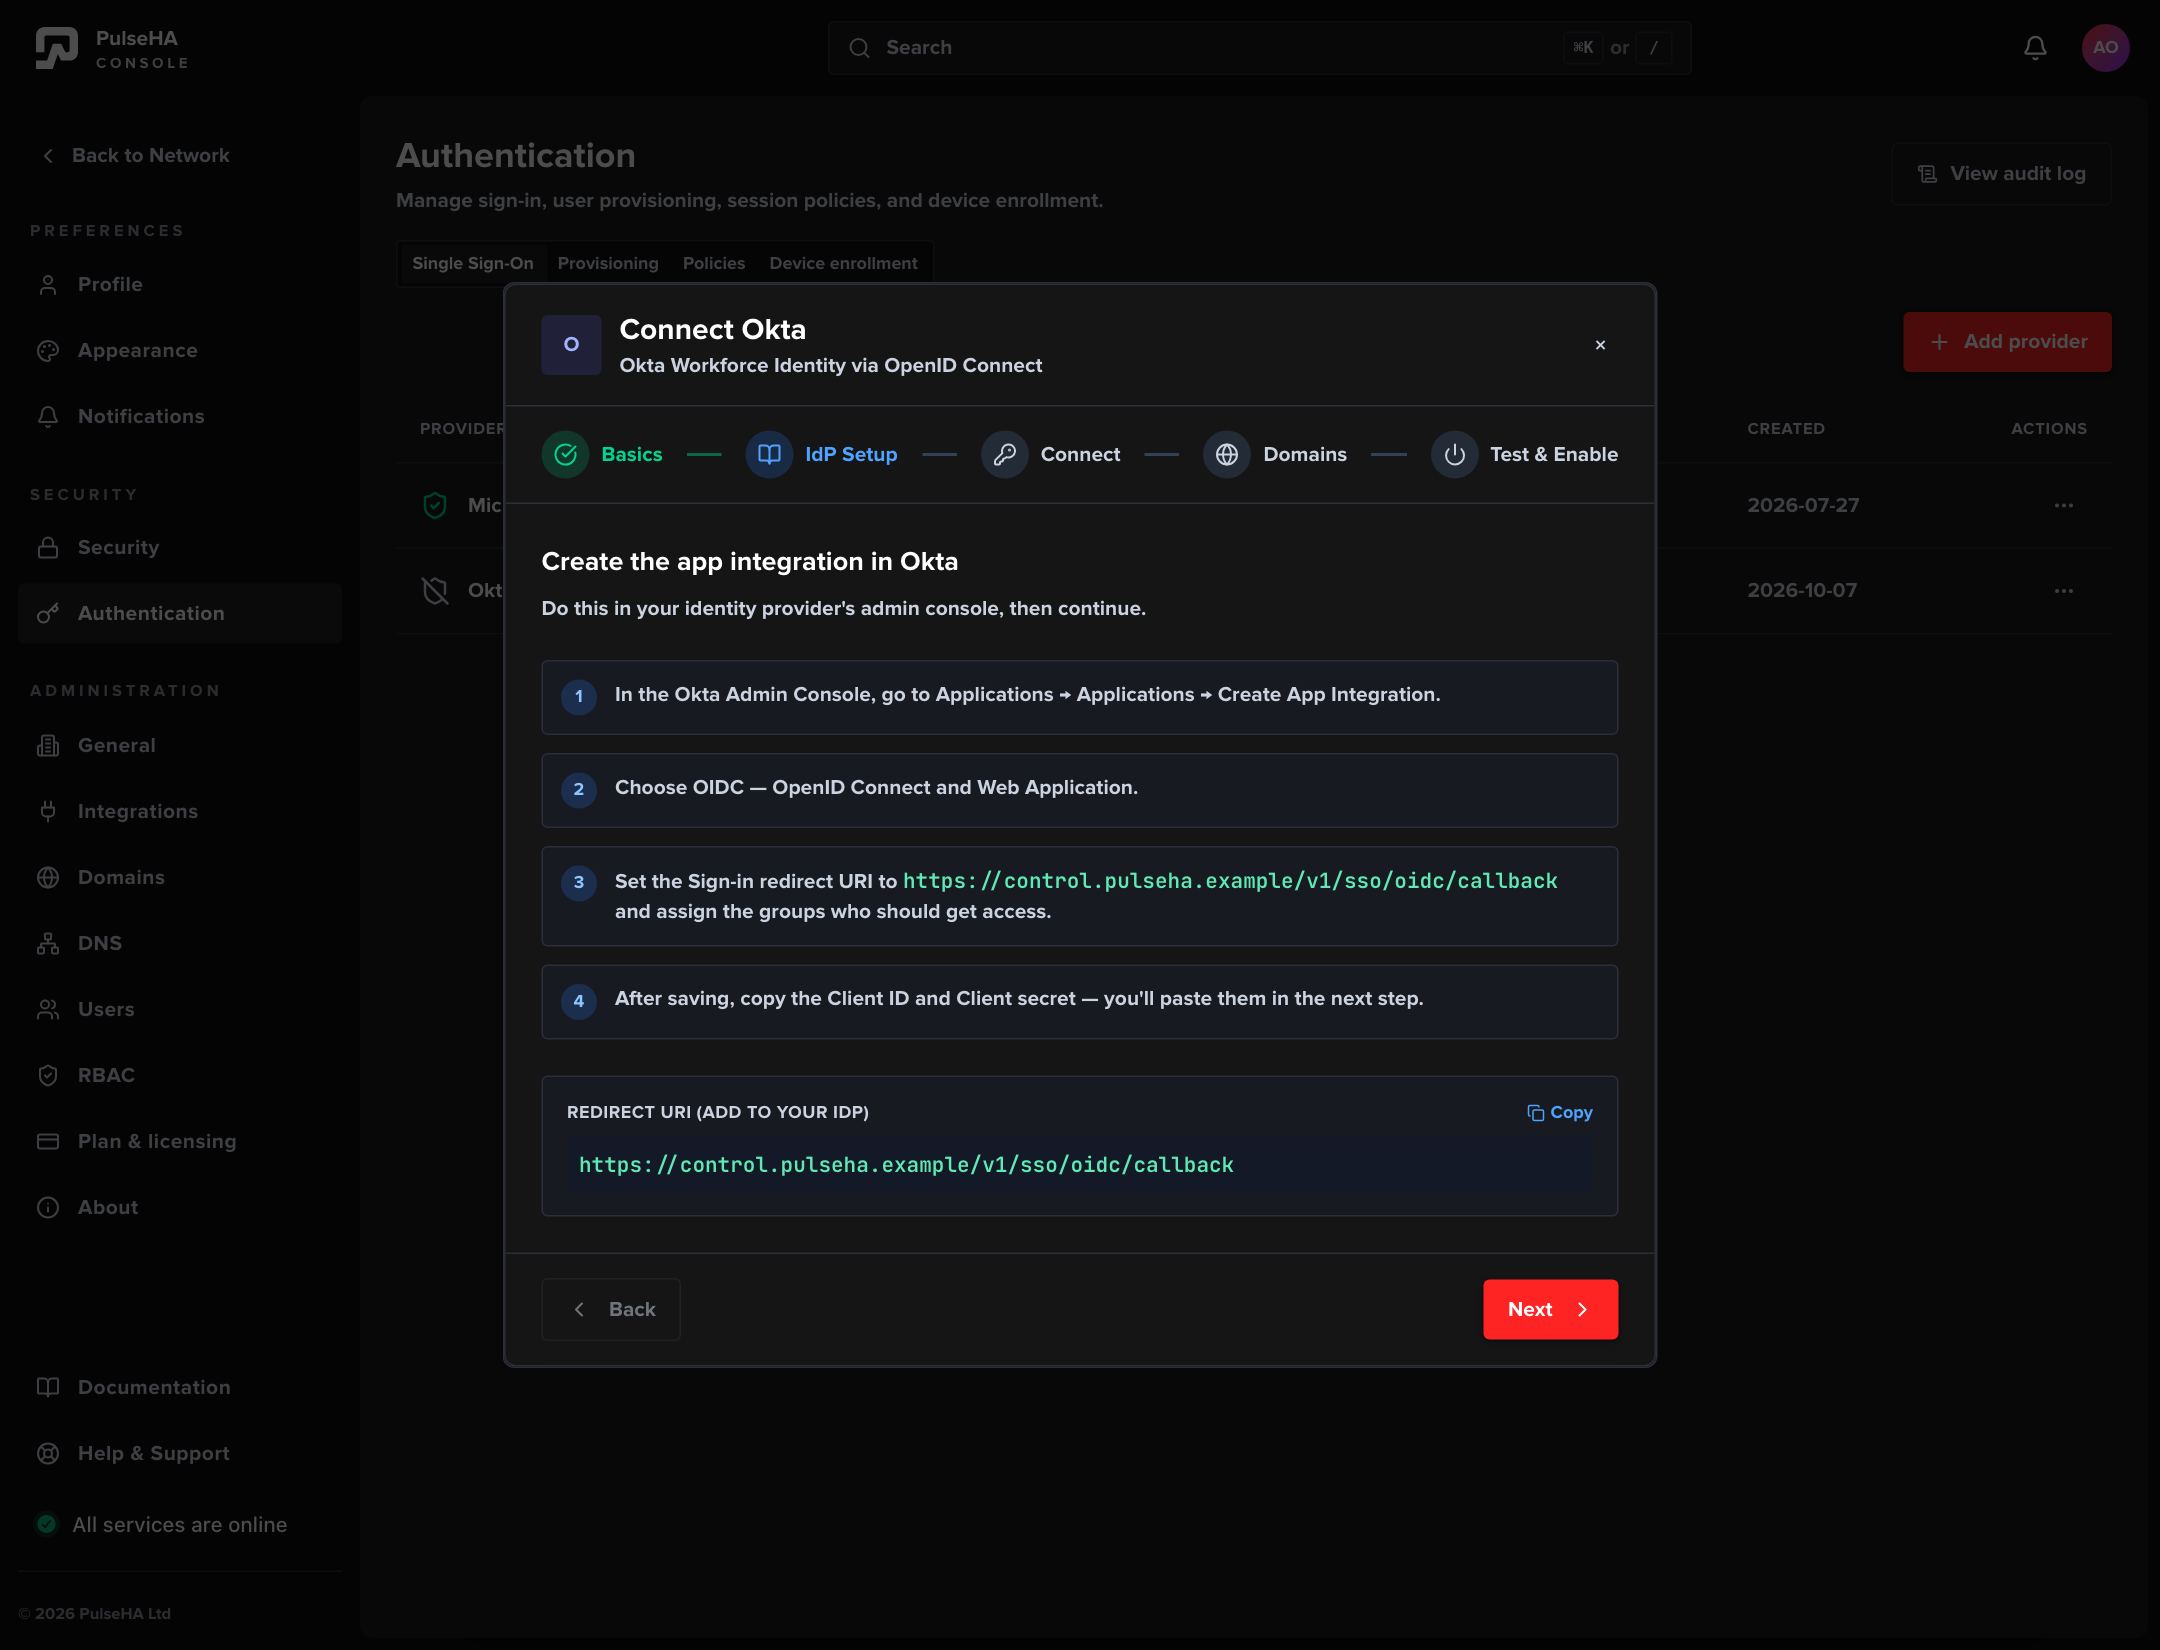
The IdP Setup step of the guided flow: numbered instructions for the provider admin console and the Redirect URI to copy.
The provider is created disabled and stays that way until step 7. Nothing changes for your users before then. After a real SSO login the status moves from Login verification required to Enabled.
Issue a SCIM token#
- Open the Provisioning tab.
- Copy the SCIM Base URL into your IdP’s provisioning settings. It points at the control plane, not the console.
- Choose Create Token. Enter a Token Name, tick the Scopes you need (Read Users, Write Users, Read Groups, Write Groups) and pick an Expiration.
- Choose Create Token, copy the value, then Done.
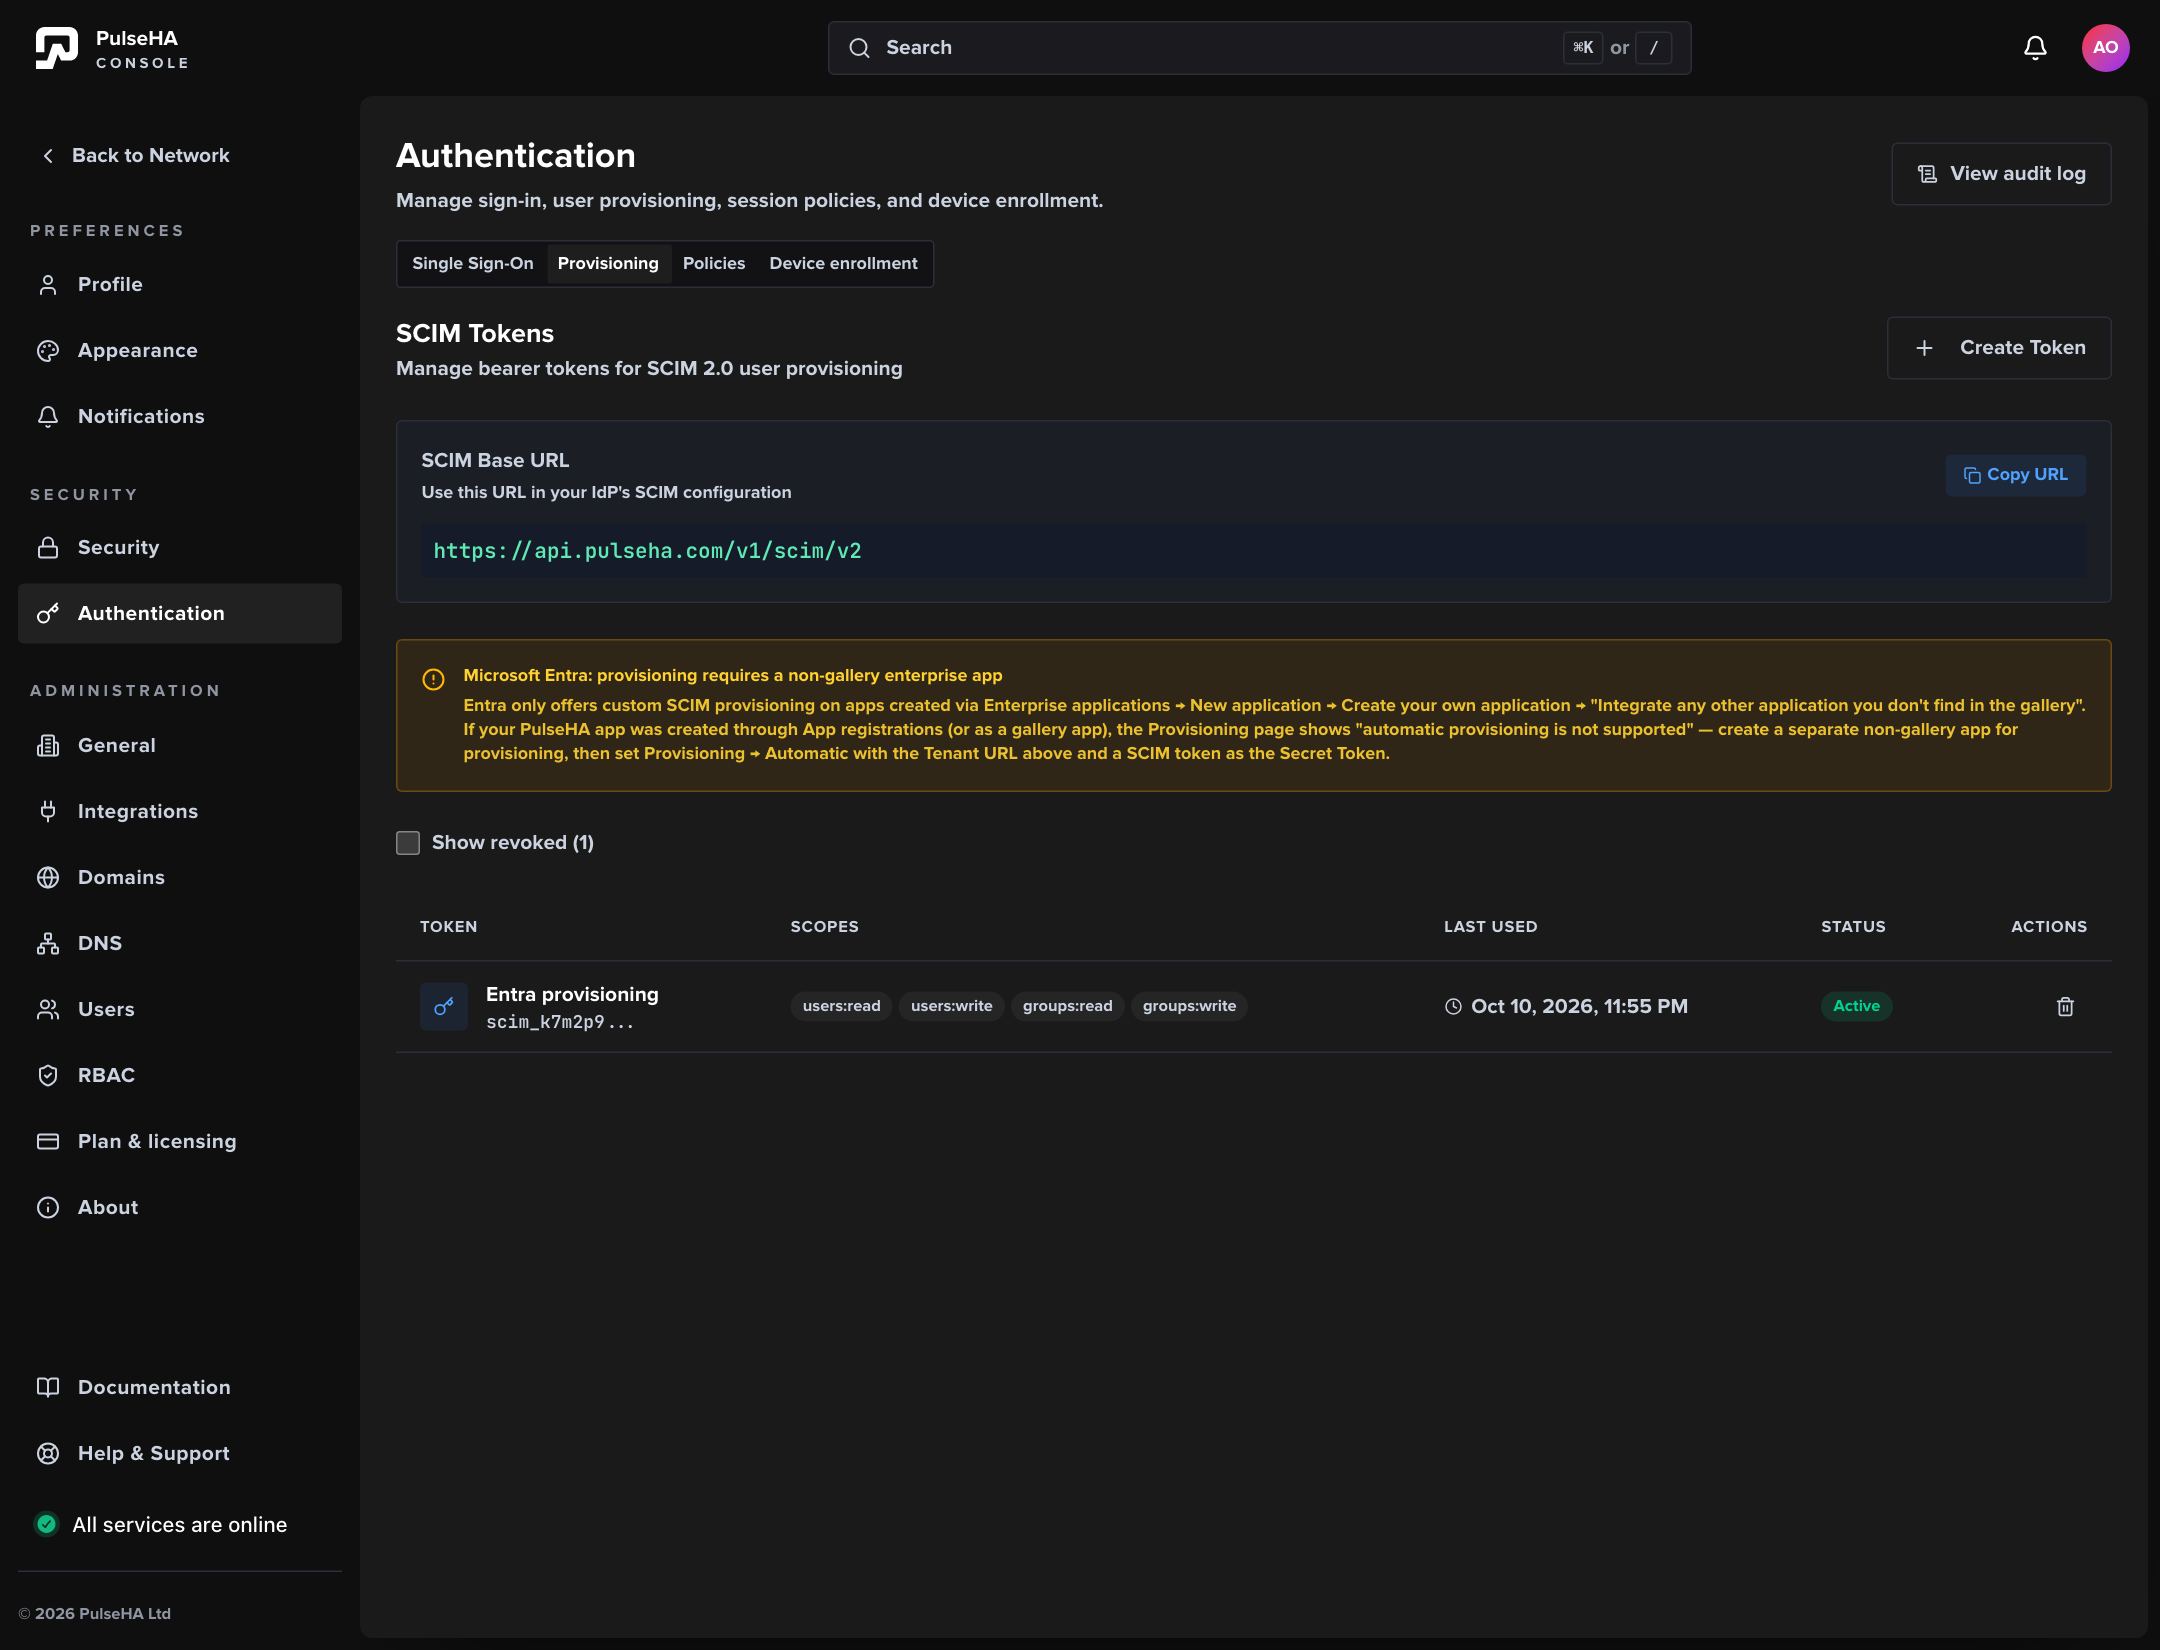
The Provisioning tab: the SCIM Base URL to paste into your IdP, the Entra note, and an active token with its scopes and last use.
The token is shown once. The table then lists it with status Active, Expired or Revoked. Use the revoke icon to withdraw it. For Microsoft Entra, provisioning only works on a non-gallery enterprise application; the tab shows the exact path.
What provisioning does#
Once your IdP’s provisioning job is on, it pushes the users and groups assigned to the PulseHA app and keeps them in sync. Entra runs an initial cycle shortly after you turn it on, then every 40 minutes. Okta pushes changes as they happen.
Before you start:
- Verify your email domain under Settings → Domains. PulseHA only provisions users whose email is on a domain your tenant has verified. Guests from other domains are refused and the IdP keeps retrying them until you unassign them or verify their domain.
- Assign a group, not everyone. Assigning “All users” sends every account in your directory, including shared mailboxes and separate admin accounts, and each becomes its own PulseHA user. Assign a group that holds the people who should have access, or add a scoping filter in the IdP.
Users. The IdP first looks each user up by email. If a user with that email already exists in your tenant, the IdP links to it instead of creating a duplicate. New users get the User role and sign in through your IdP; no invite email is sent. You can change their role in the console. Their name, email and status belong to the IdP.
Suspended and deleted users. Disabling or unassigning a user in the IdP suspends them in PulseHA. A suspended user loses console and API access on their next request and their devices leave the gateway configuration within a few seconds, but stay enrolled. Re-enabling the user in the IdP restores both without re-enrolling. Deleting the user in the IdP revokes their devices for good; a re-created user enrolls again.
Groups. Each assigned group becomes an access group with the same name and membership, so you can write access policies against your IdP groups instead of maintaining membership by hand. Synced groups are read-only in the console. A SCIM role mapping on the Provisioning tab gives every member of a named group a console role.
Check that provisioning is working#
- The Provisioning status card on the Provisioning tab shows how many users and groups the IdP manages and when it last synced.
- The token’s Last used column updates on every sync. Never used after the first cycle means the IdP is not reaching PulseHA: check the Base URL and that the full token was pasted as the secret.
- Users shows a SCIM source chip on each managed user and their status (Active, Suspended or Deprovisioned). Managed users cannot be removed or renamed in the console; make those changes in the IdP.
- Logs records every provisioning change under the SCIM category: user provisioned, suspended, reactivated and deprovisioned, and group synced.
Set SSO enforcement and JIT provisioning#
- Open the Policies tab.
- Under SSO Enforcement pick No enforcement, Optional (prompt) or Required for all.
- Optionally turn on Just-in-Time Provisioning, pick a Default Role for JIT Users and tick Auto-activate accounts if you want to skip manual approval.
- Choose Save Settings.
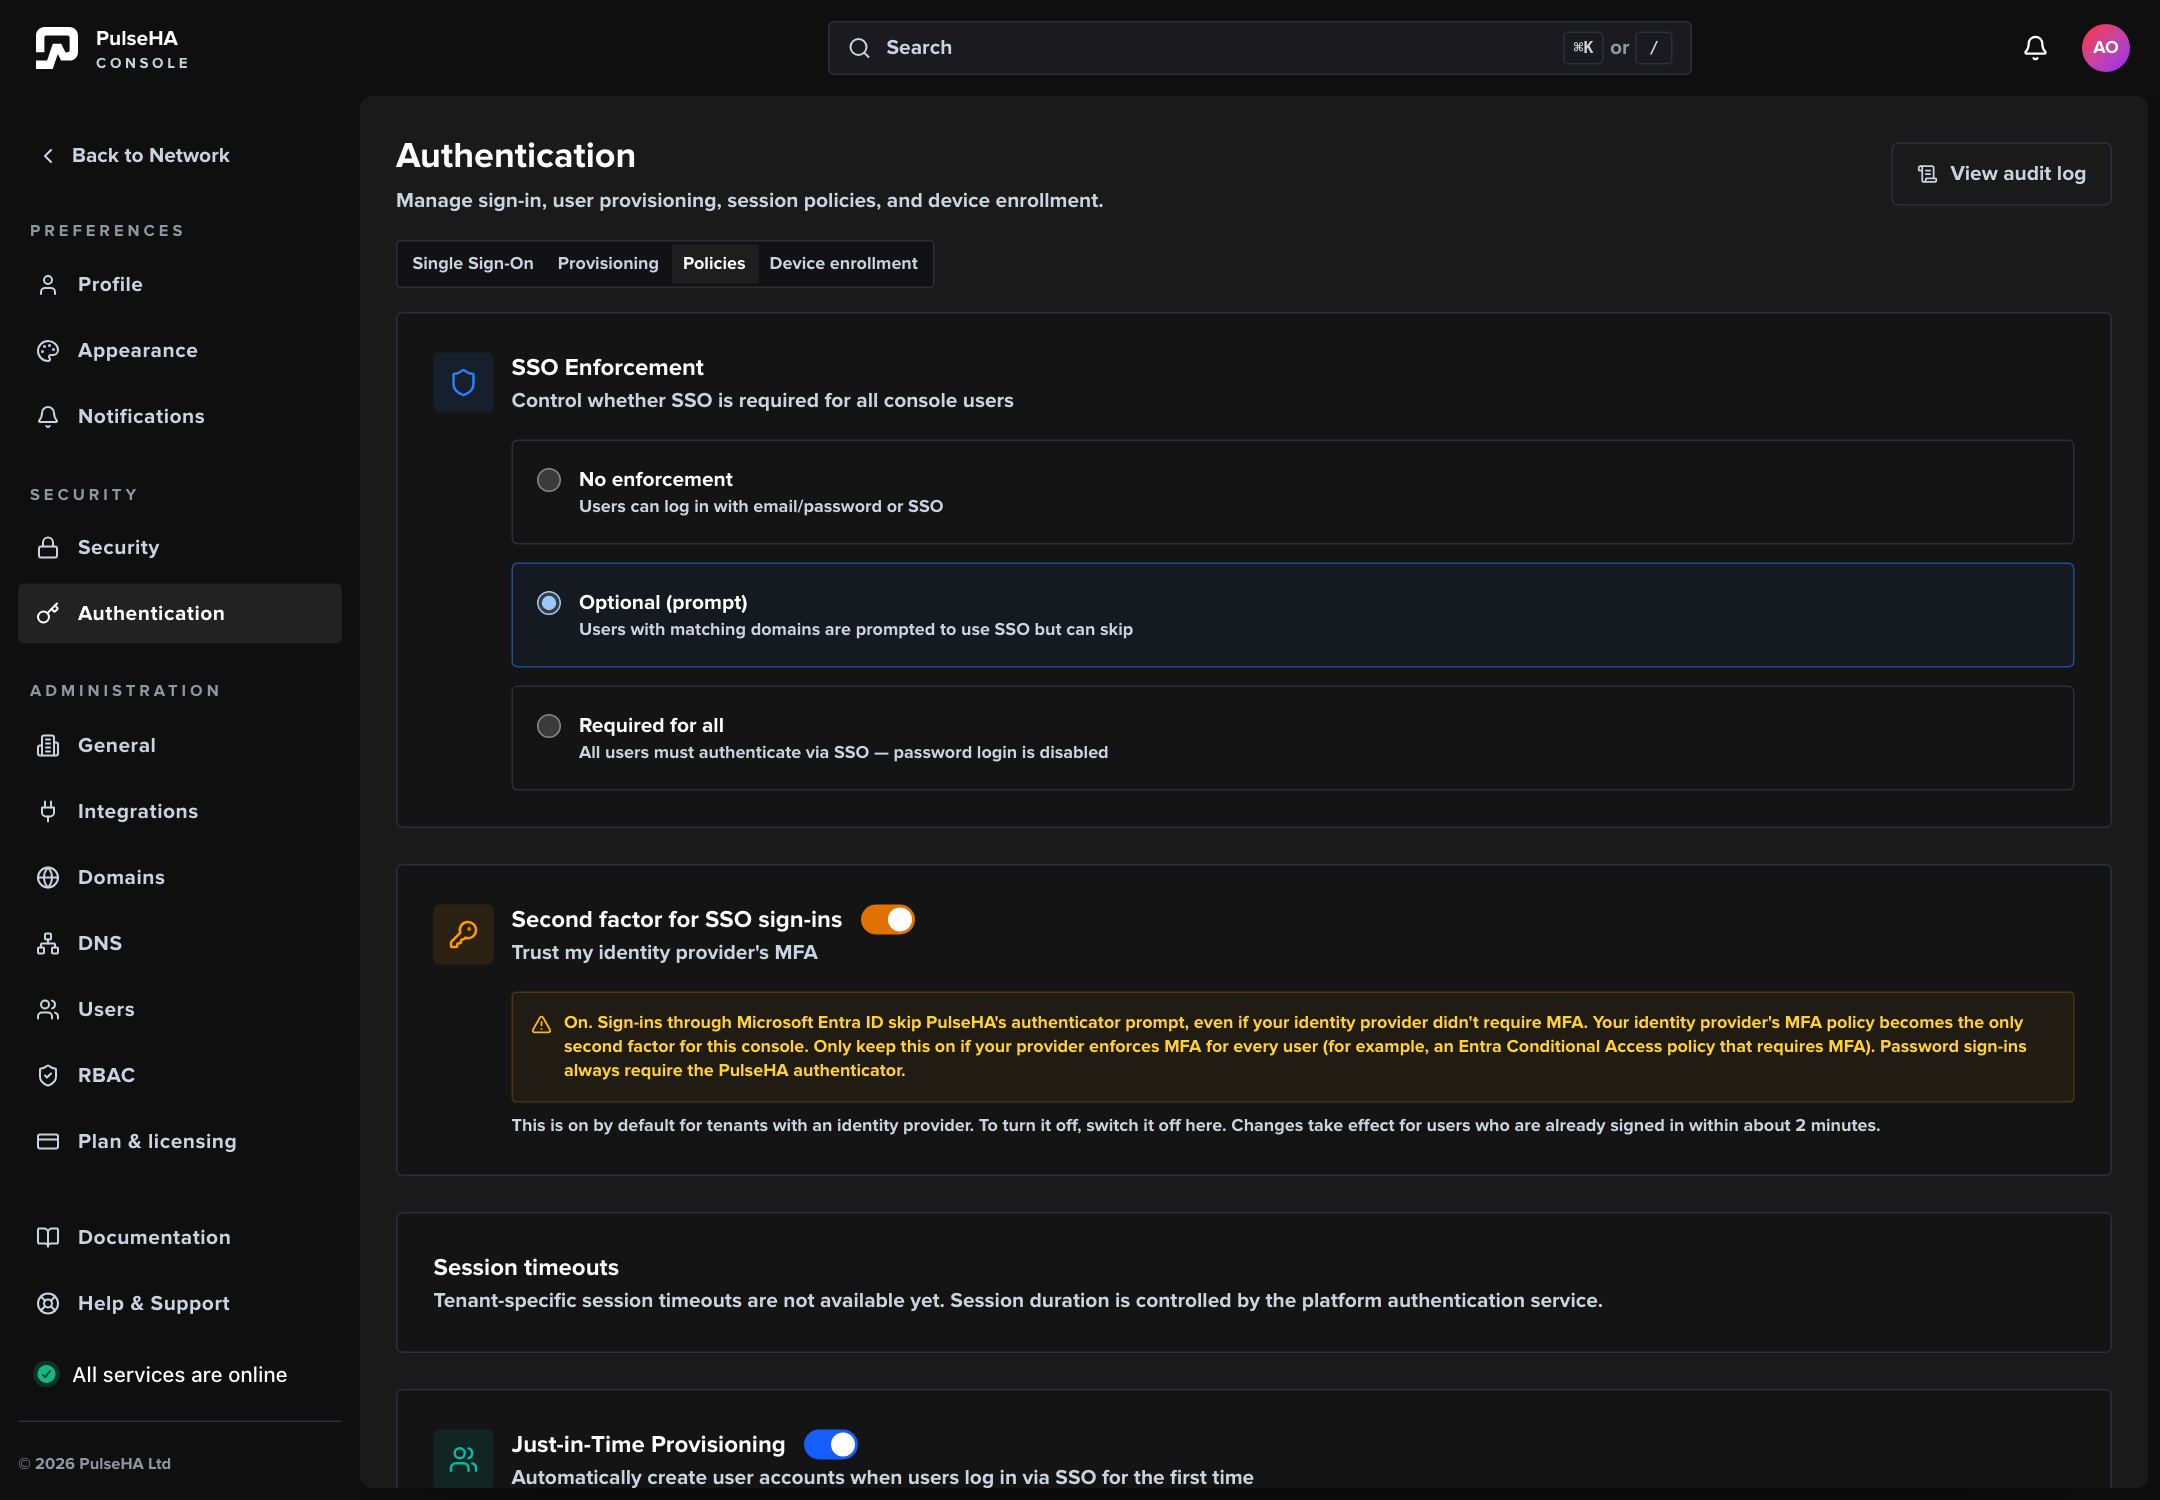
The Policies tab: the three SSO Enforcement options, the second factor trust toggle, and Just-in-Time Provisioning.
Required for all is only selectable when a provider is enabled, configured, login-verified and has a verified domain. The control plane also requires that you yourself signed in through SSO in this session. Otherwise it answers “Sign in through SSO before requiring it for everyone”. Owner and Admin cannot be chosen as the JIT role. Tenant session timeouts are not available; the tab says so.
Reference#
Provider statuses:
| Status | Meaning |
|---|---|
| Continue setup / Incomplete | Protocol configuration missing. Opens the guided flow. |
| Login verification required | Enabled, but no successful SSO login since the last configuration change. |
| Enabled | Configured, enabled and verified. |
| Ready (disabled) | Configured but switched off. |
| Unavailable | Configuration state could not be loaded. |
Row actions: Configure SAML or Configure OIDC, Verify Domains, Enable or Disable, Remove.
Enforcement options:
| Option | Effect |
|---|---|
| No enforcement | Email/password or SSO. |
| Optional (prompt) | Users with matching domains are prompted to use SSO but can skip. |
| Required for all | Password login is disabled for everyone. |
SCIM token Expiration choices: Never expires, 30 days, 90 days, 6 months, 1 year.
Troubleshooting#
- Required for all is greyed out. The note reads “Requires a configured provider, verified domain and successful SSO login after the latest configuration change.” Complete the setup flow and sign in through SSO once.
- “Reload settings before saving” or “Settings changed or the safety checks rejected this update.” Another session saved first. Refresh the tab and reapply your change.
- “An enabled, configured provider with a verified domain is required”. At least one provider must pass all three checks before enforcement can be required.
- Test reports Issues found. Each line names the failing check. For OIDC, confirm the discovery URL, client ID and secret or federated credential. For SAML, re-import metadata.
- “failed to reach OIDC discovery endpoint”. The control plane could not fetch the discovery document. Check the URL and that it is publicly reachable.
- Users with the right domain still see password login. The domain is unverified or the provider is disabled. Open Verify Domains on the provider row.
- “Identity providers could not be loaded.” Choose Retry providers.
- Entra shows “automatic provisioning is not supported”. The app was created under App registrations. Create a non-gallery enterprise app for provisioning.