Device posture
Evaluate endpoint health and enforce failures deliberately.
Use Security → Device Posture to define the checks a device must pass and what happens when it fails. Device posture checks health evidence reported by the agent. Device policies configure agent behaviour; access policies grant services.
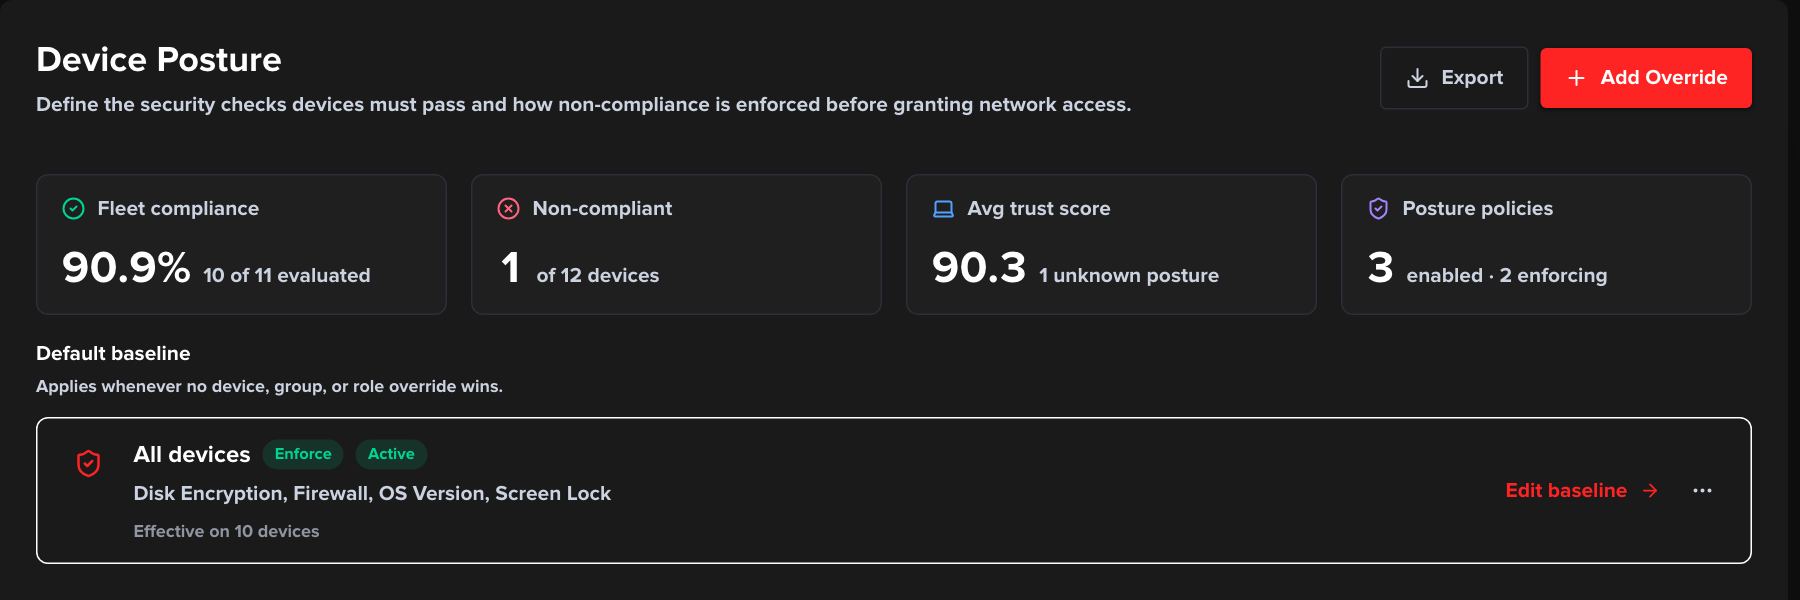
The four overview cards summarise the fleet; here 10 of 11 evaluated devices are compliant, one device is unknown, and the baseline enforces four checks.
Before you start#
- Viewing needs
policies:view. Creating a policy needspolicies:create. Editing, enabling or disabling needspolicies:update. Deleting needspolicies:delete. On tenants without a permission list, owners and admins hold all four; the user role can view and create; readonly can only view. - Agents must be enrolled and reporting. The page states that compliance metrics appear “after agents connect and report posture on heartbeat.”
- A default baseline must exist before you can add scoped overrides. The control plane rejects an override otherwise with “create the tenant baseline before adding overrides”.
- Scope cannot be changed after a policy is created.
Create the baseline#
- Open Security → Device Posture and click Create Baseline. (Once a baseline exists the button reads Add Override.)
- Under Quick Start, pick a preset or skip it: Essential, Standard or High Security. Essential starts in monitor mode with disk encryption and firewall; High Security enforces all six checks.
- Under Scope & Targeting, choose Entire Tenant. The other scopes are Role, Group and Device.
- Under Enforcement Mode, choose Monitor, Warn or Enforce. Start with Monitor.
- Under Required Security Checks, select at least one check. The counter reads “N of 6 selected”.
- If you chose Enforce, pick an Enforcement Action: Block Access, Quarantine or Warn User.
- Optionally open Advanced Options to set Min Trust Score (0 to 100), Grace Period (min) and Priority.
- Wait for the Impact Preview. It reads “{f} of {e} evaluated devices would fail this policy right now.” The Create Policy button stays disabled until the preview succeeds.
- If the preview shows devices that will lose access, tick “I understand {n} devices will lose network access when this policy is saved.”
- Click Create Policy.
You should see the policy in the Default baseline card with “Effective on N devices · N would fail”.
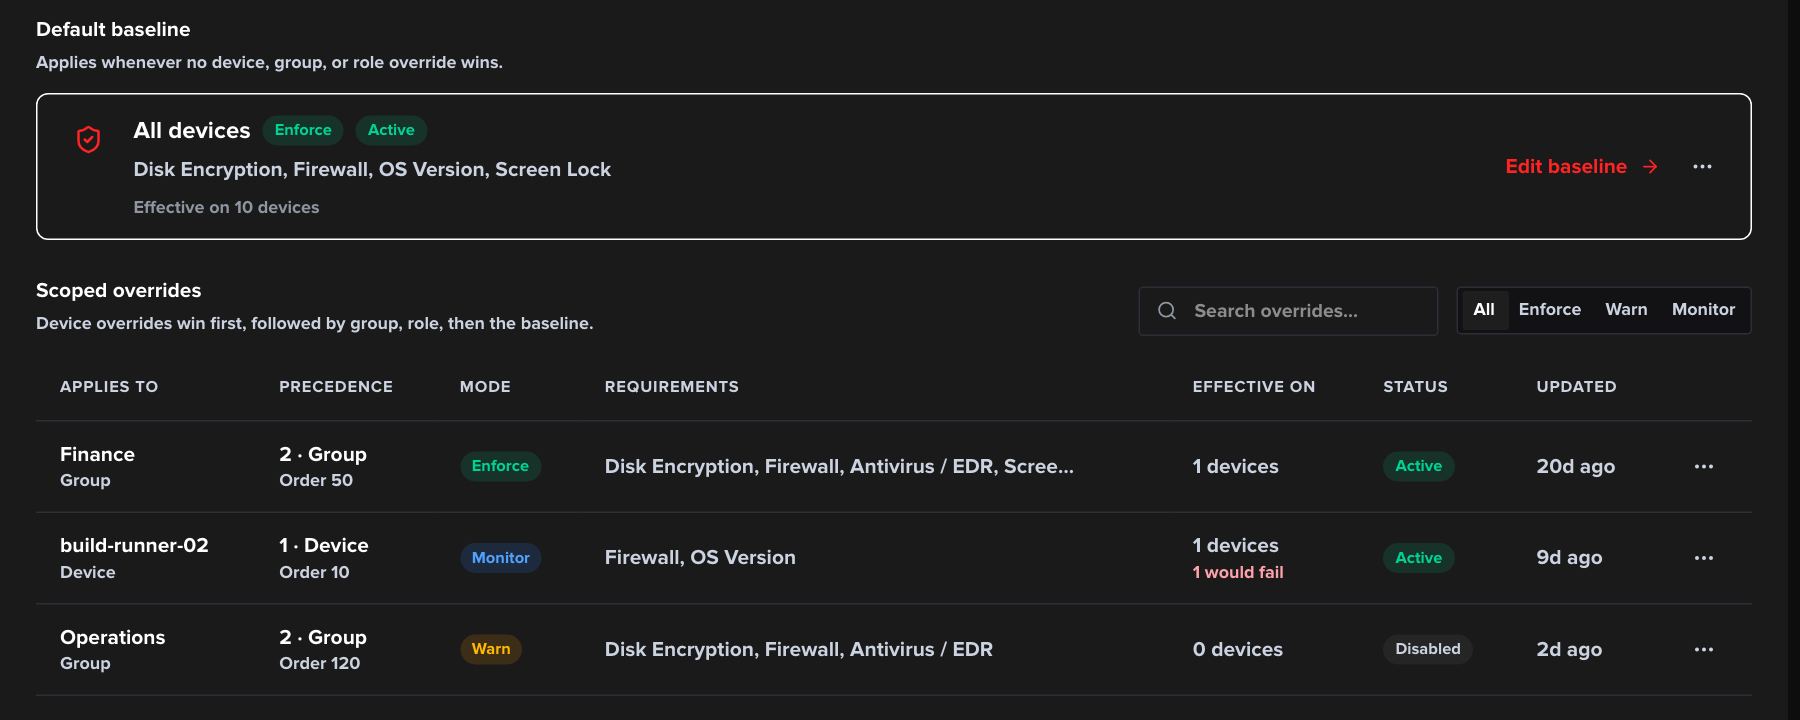
The baseline card sits above the Scoped overrides table; the Precedence column shows the scope rank and Order, and a row flags how many devices would fail.
Add a scoped override#
- Click Add Override.
- Choose Role, Group or Device and pick a target. If a catalog is down you see “Temporarily unavailable” and must choose another scope.
- Complete the mode, checks and action as above, then click Create Policy.
The override appears under Scoped overrides. Its Precedence column shows “1 · Device”, “2 · Group” or “3 · Role” and “Order {priority}”.
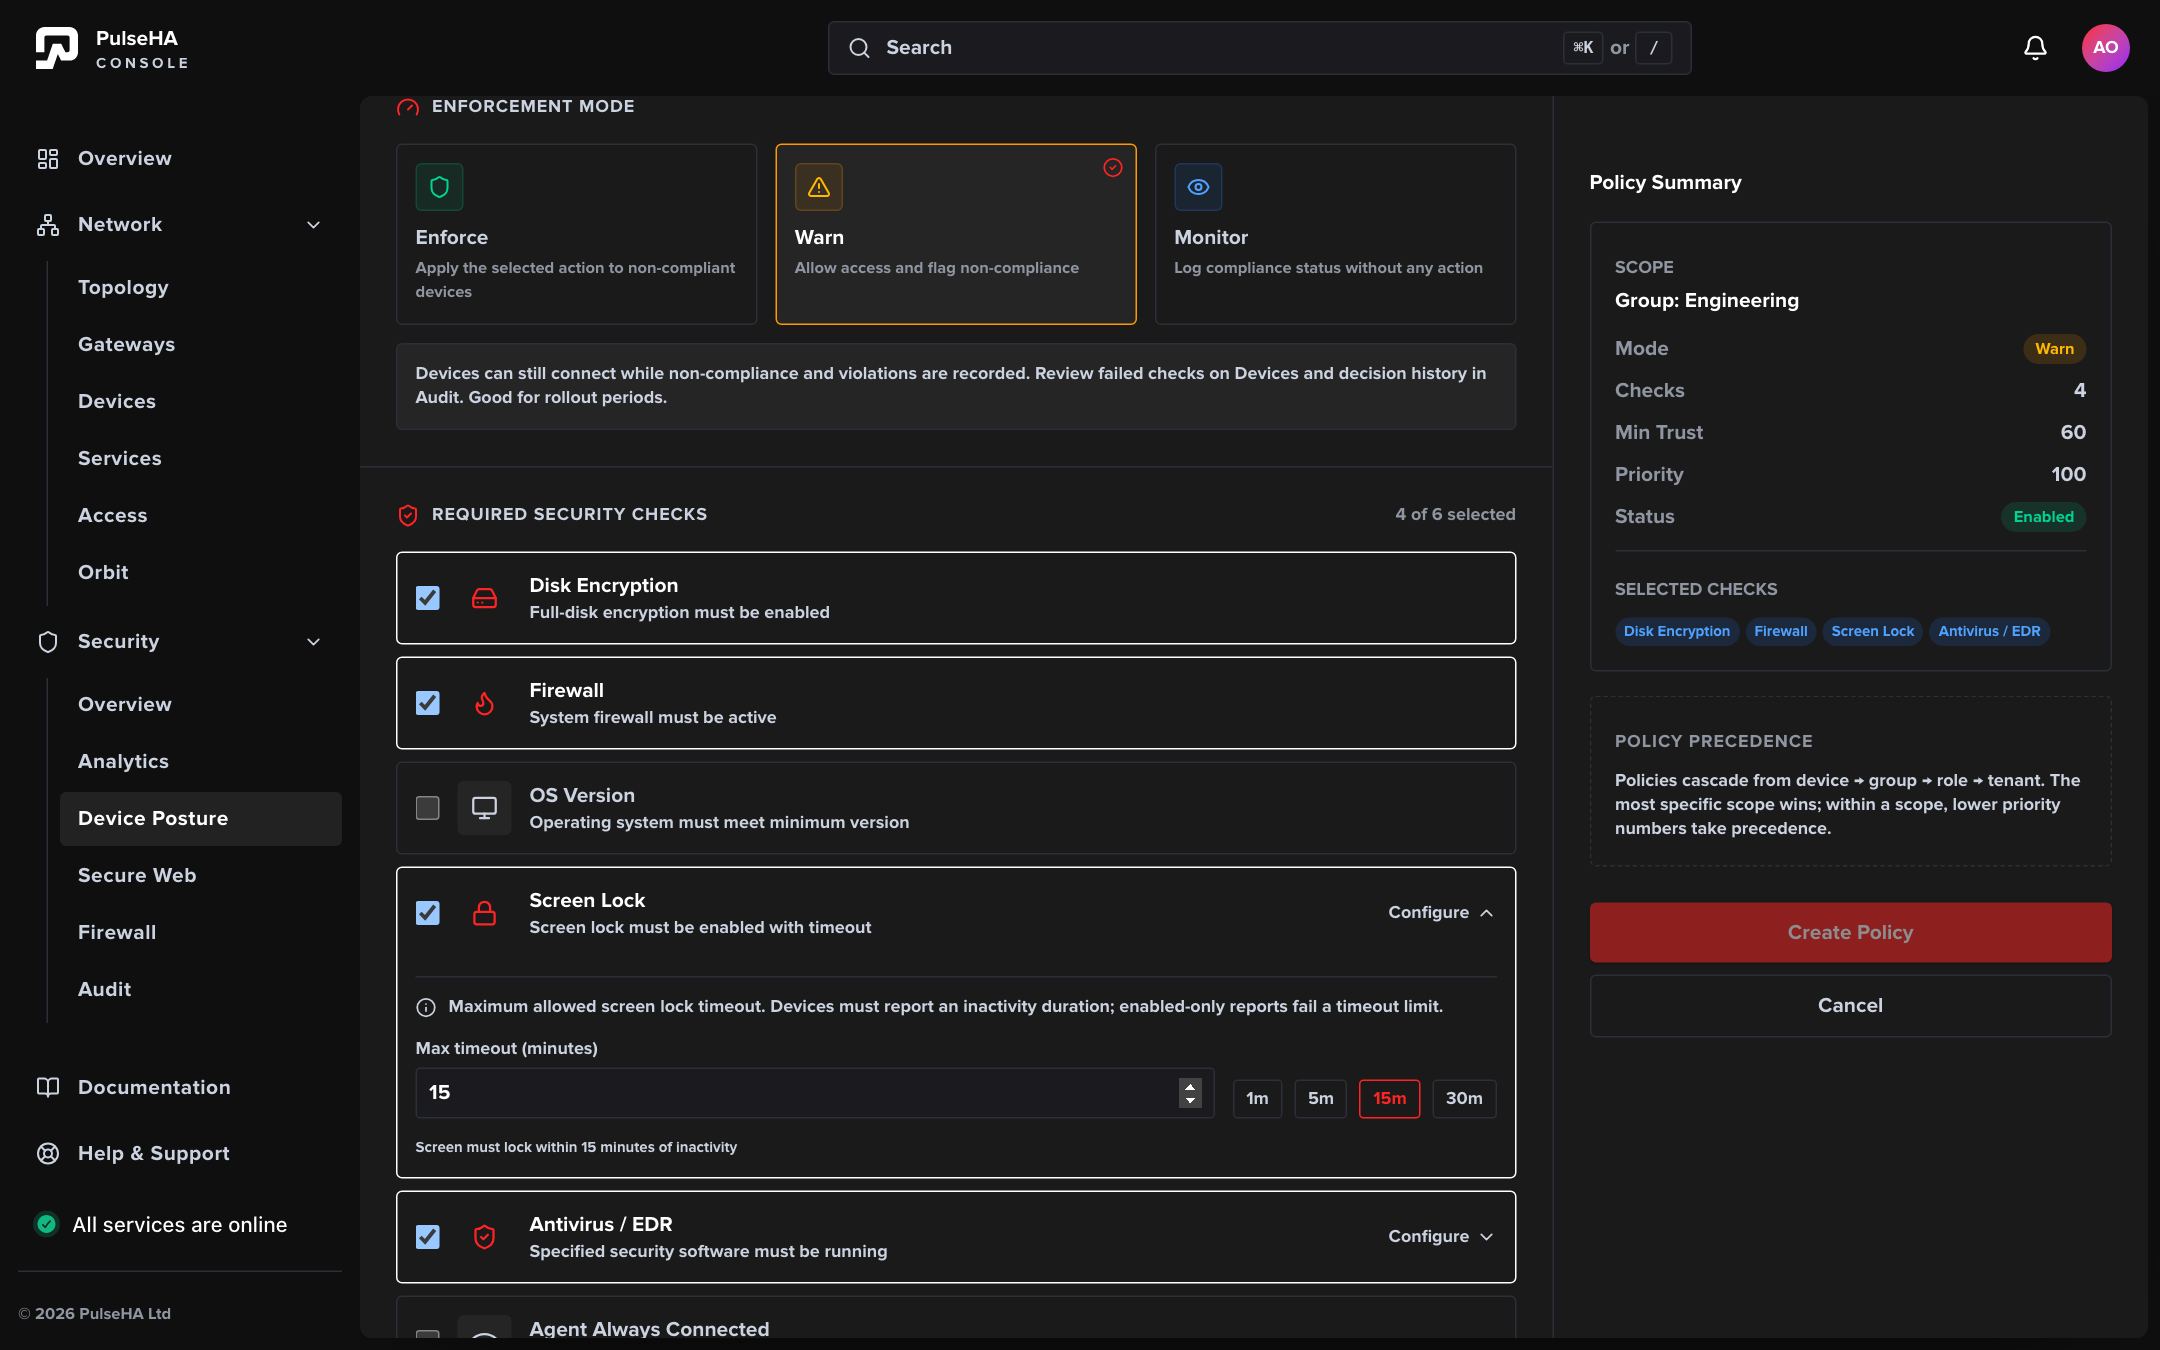
The Standard preset fills the form: Group scope with a target picked, Warn mode, and four of six checks ticked, with the Policy Summary tracking every change.
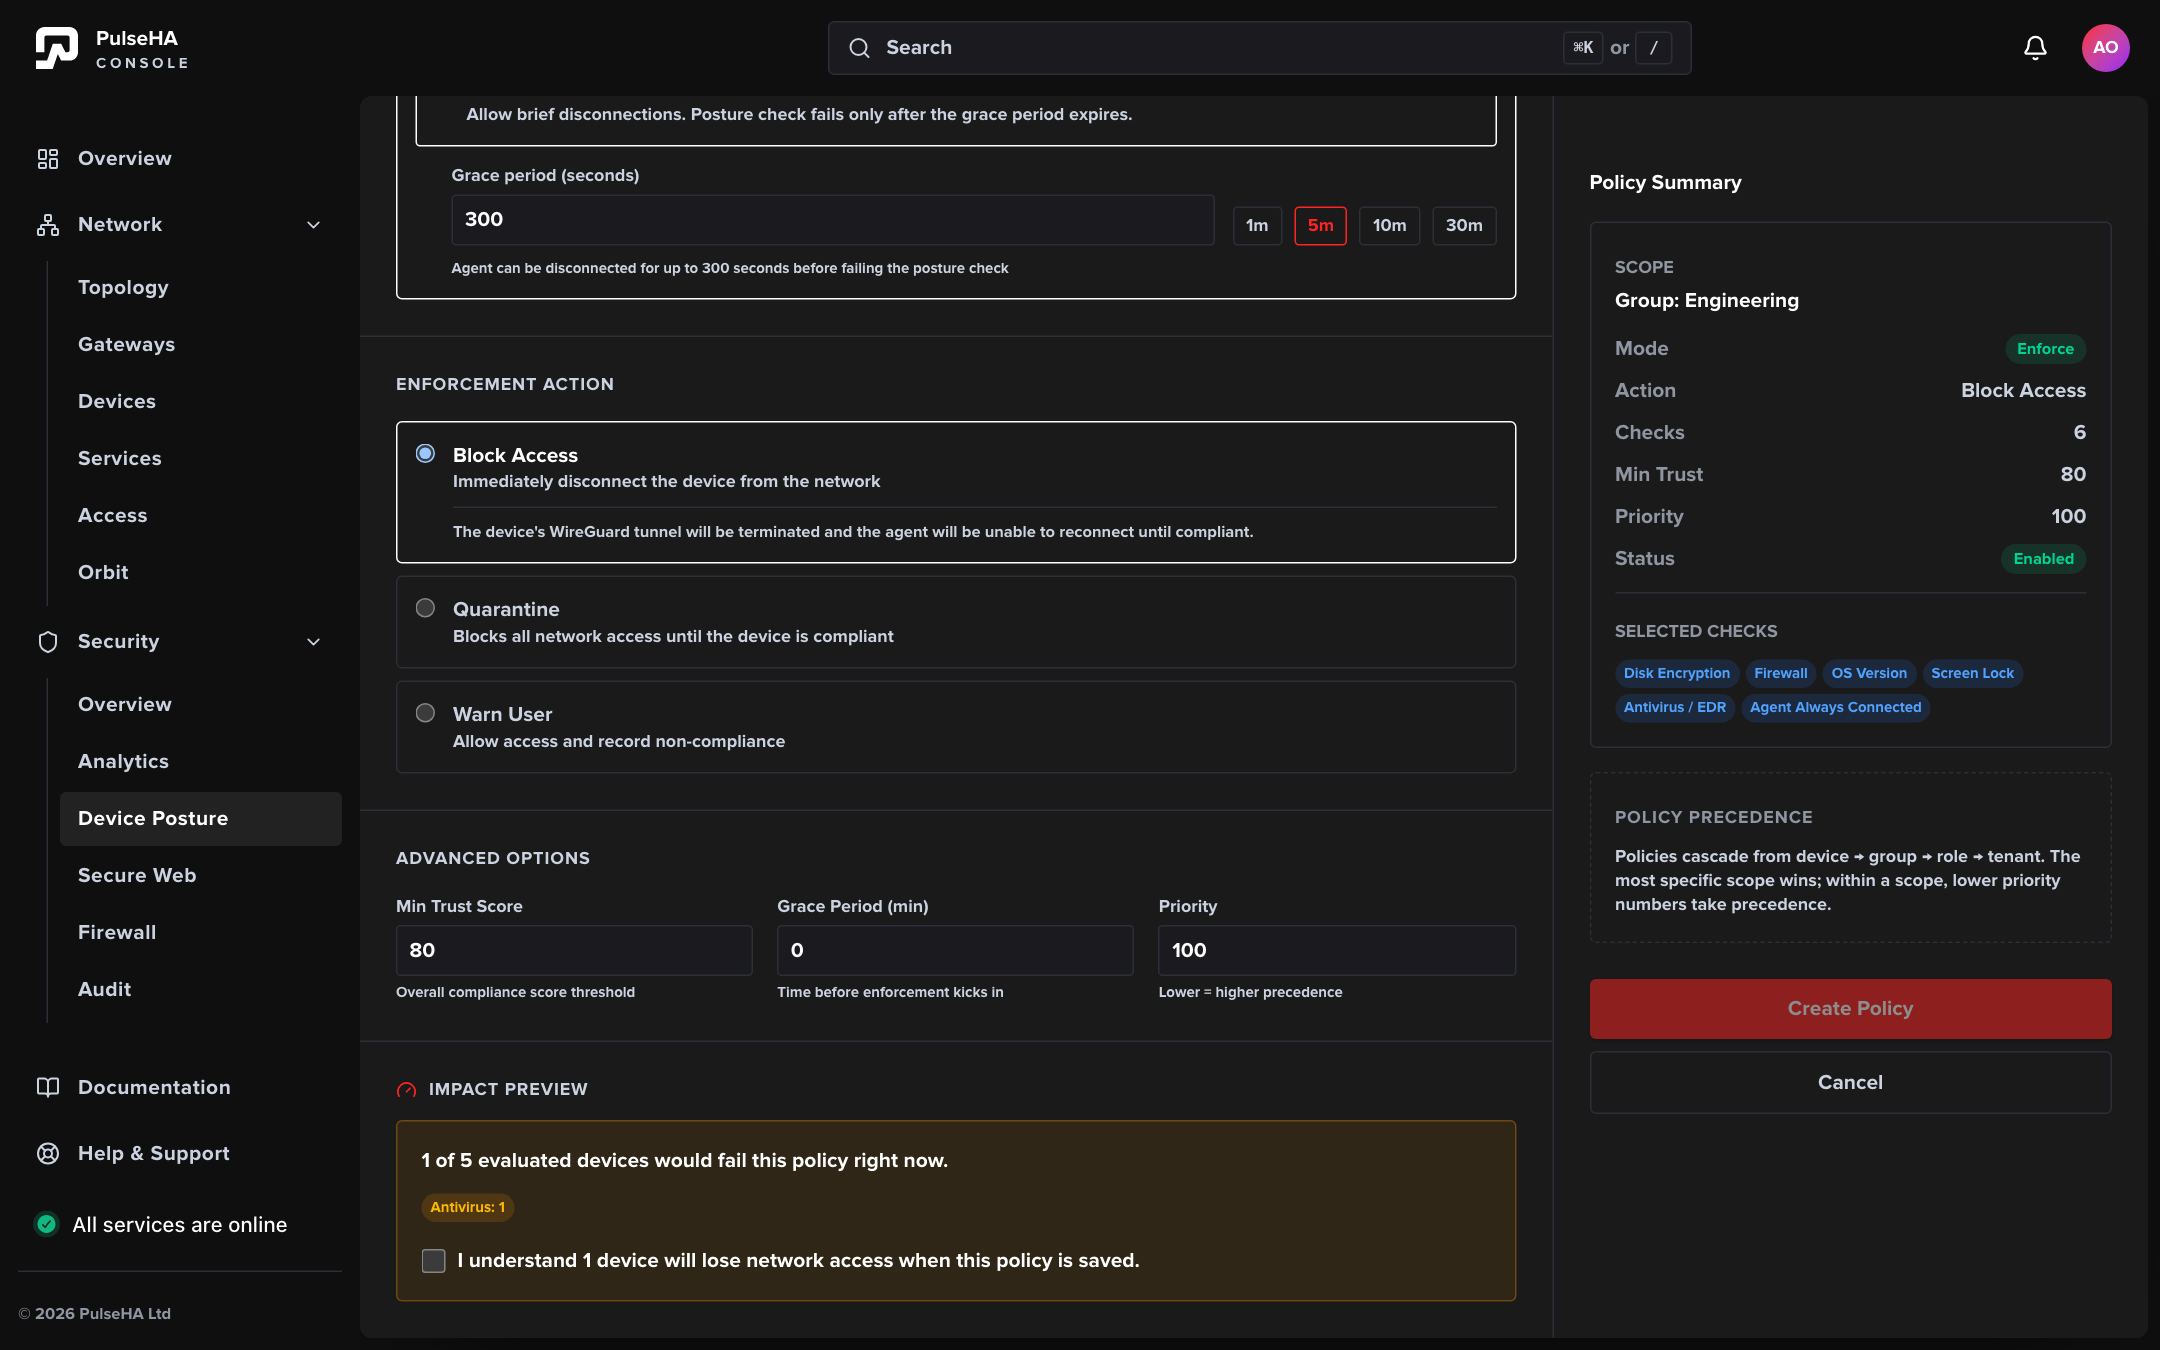
In Enforce mode the Impact Preview counts the devices that would fail today, names the failing check, and asks you to acknowledge the loss of access before Create Policy enables.
Enable or tighten a policy#
- Open the row menu and choose Enable policy.
- If the policy is in Enforce mode with a blocking action and some devices would fail or have no data, the dialog is titled Acknowledge and Enable Policy and warns “{n} devices may lose network access when this enforce policy is enabled.”
- Click Acknowledge and enable.
Move from Monitor to Warn to Enforce only after you have fixed the expected failures.
Reference#
Checks#
| Check | What it verifies |
|---|---|
| Disk Encryption | BitLocker, FileVault, or LUKS/dm-crypt |
| Firewall | Windows Firewall, macOS Application Firewall, or ufw, firewalld or iptables |
| OS Version | Minimum version per platform. Leave a platform blank to accept any version. |
| Screen Lock | Max timeout (minutes), 1 to 60. Devices must report an inactivity duration. |
| Antivirus / EDR | Any AV/EDR or Specific Products Only from a list of named products |
| Agent Always Connected | Strict Mode fails on any disconnection. Grace Mode fails after a grace period of 30 to 3600 seconds (default 300). |
Modes and actions#
| Setting | Effect |
|---|---|
| Monitor | Logs compliance status. No user notification, no block. |
| Warn | Devices connect. Non-compliance is recorded in Devices and Audit. |
| Enforce | Applies the chosen action to non-compliant devices. |
| Block Access | Terminates the device’s WireGuard tunnel. The agent cannot reconnect until compliant. |
| Quarantine | Currently equivalent to Block Access. Remediation-only access is planned but not available. |
| Warn User | Device keeps access; non-compliance is recorded. |
Precedence#
Device overrides win first, then group, then role, then the baseline. Within one scope, lower Order wins. Equal order is broken by stricter mode (enforce over warn over monitor), then lowest policy ID. Disabled policies are skipped. Devices matching several overrides at one scope appear under Overlapping overrides.
Overview cards#
Fleet compliance (compliant devices as a percentage of evaluated devices), Non-compliant, Avg trust score and Posture policies (enabled count, with how many are enforcing). A device with no posture report counts as unknown. A device with no effective policy is not covered.
Posture reports older than five minutes are treated as stale by default and add a stale-report violation. In enforce mode, devices with no posture data are blocked until they report. Never treat unknown or stale evidence as compliant.
Troubleshooting#
- “Device posture data could not be loaded” with Retry. The overview endpoint failed. Retry, then check control plane health.
- “Some posture targets are temporarily unavailable”. A role, group or device catalog did not load. Those scopes cannot be selected until it does.
- “Saving is disabled until the preview succeeds.” The impact preview failed. Fix the form error it reports or retry.
- “enable the tenant baseline before enabling posture overrides” or “disable posture overrides before disabling the tenant baseline”. The baseline must be enabled while any override is enabled.
- “a posture policy already exists for this subject”. Only one policy per scope target is allowed. Edit the existing one.
- Banner “N devices have no effective posture policy”. Add or enable the baseline.
Related tasks#
- Audit to review posture decisions under the Posture category.
- Devices to see failed checks per device.
- Device policies to configure agent behaviour.
- Device trust for device authorisation.
- Reports for fleet compliance summaries.